Blue Goat CyberBlue Goat CyberSMMedical Device Cybersecurity
    Start here
    Services
    • FDA Premarket Cybersecurity Package
    • Medical Device Penetration Testing
    • Medical Device Threat Modeling
    • FDA Deficiency Response
    • FDA Postmarket Cybersecurity
    • MedTech Compliance Bundle
    See all services
    Products

    Blue Goat products

    • GoatWatch logoGoatWatchSBOM risk management for medical devices
    About
    Resources

    Learn

    • Blog
    • Podcast
    • Webinars
    • Talks & workshops
    • Glossary
    • FAQs

    Playbooks & Tools

    • Guides
    • Playbooks (PDF)
    • Infographics
    • Interactive Tools

    Signals & Proof

    • Goat FeedNew
    • News
    • Medical Device Security News
    • The Goat's Weekly
    • Case Studies
    • Proof / Receipts
    All resources, topic hubs, & collections →
    ⌘K
    Book Strategy SessionHow to prepare →
    Blue Goat Cyber

    Full-service medical device cybersecurity. We protect patients by securing connected medical devices from design through postmarket.

    275+ FDA submissions supported, zero cybersecurity rejections · Mission: 1,000 by 2028

    SDVOSB · Service-Disabled Veteran-Owned Small Business

    We sponsor 10 community projects →

    Services

    • FDA Premarket Cybersecurity Package
    • FDA Deficiency Response
    • Medical Device Threat Modeling
    • Medical Device Penetration Testing
    • FDA Postmarket Cybersecurity
    • All services →
    Services
    • FDA Premarket Cybersecurity Package
    • FDA Deficiency Response
    • Medical Device Threat Modeling
    • Medical Device Penetration Testing
    • FDA Postmarket Cybersecurity
    • All services →

    Company

    • About
    • Core values
    • Manifesto
    • Leadership
    • Why Us
    • Partners
    • Careers
    • Press
    • Press kit
    • Contact
    • Company overviewPDF
    Company
    • About
    • Core values
    • Manifesto
    • Leadership
    • Why Us
    • Partners
    • Careers
    • Press
    • Press kit
    • Contact
    • Company overviewPDF

    Resources

    • Blog
    • Guides
    • Podcast
    • Case studies
    • Monthly Pulse newsletter
    • All resources →
    Resources
    • Blog
    • Guides
    • Podcast
    • Case studies
    • Monthly Pulse newsletter
    • All resources →

    Get in touch

    • info@bluegoatcyber.com
    • 844-939-GOAT
    • Book a strategy session →
    • 1776 N Scottsdale Rd, Unit 727
      Scottsdale, AZ 85257Serving clients worldwide

    Follow

    © 2026 Blue Goat Cyber. All rights reserved.

    • Privacy
    • Terms
    • Cookies
    • Sitemap
    • Accessibility
    • CVD

    MedTech Cybersecurity · Since 2022

    A goat standing on a rocky mountain ridge at night
    About

    We protect patients by helping MedTech teams build secure devices.

    Founded by Christian Espinosa, a mountain climber and former military cyber operator. Named after the resilience of mountain goats - and built on the belief that medical device cybersecurity deserves a specialist.

    FDA 2026 · AAMI SW96 · ISO 13485 · ISO 14971
    • Jump to
    • Purpose
    • Vision
    • Mission

    Built on the standards FDA reviewers expect

    • FDA 2026Premarket cyber
    • §524BFD&C Act
    • AAMI SW96Security risk
    • ISO 13485Quality system
    • ISO 14971Risk management
    • IEC 62304Software lifecycle
    • SPDFSecure dev framework
    • SBOMSoftware bill of materials
    Our story

    A mission born from expertise - and a personal resolve.

    Download the Company Overview (PDF, 7 pages)Read the Company OverviewOne-pager (PDF)

    Blue Goat Cyber's story starts a decade before the company existed. In 2014, founder Christian Espinosa launched Alpine Security to help manufacturers navigate FDA expectations and protect the patients who depend on connected devices. After selling Alpine in 2020, a serious health scare gave Christian a firsthand appreciation for how much modern medicine depends on technology working safely, reliably, and securely.

    In 2022, he founded Blue Goat Cyber with a sharper, more personal mission: protect lives by making sure medical devices are secure by design and ready for FDA scrutiny. Since then, the team has supported submissions for startups and global manufacturers alike - including Intuitive Surgical, bioMérieux, Nova Biomedical, Inogen, and Natera - across robotic surgery systems, diagnostic platforms, blood analyzers, wearables, and SaMD.

    We're a service-disabled veteran-owned business. 275+ FDA submissions supported, zero cybersecurity rejections. Every engagement is fixed-fee with retesting included, and if the FDA raises a cybersecurity question, we answer it at no extra cost until the cybersecurity portion is closed. That's how we structure the work; clearance is always the FDA's decision.

    From the radiology report · 2022
    “Diagnosed with acute DVT across the left femoral, popliteal, gastrocnemius, posterior tibial, peroneal, and soleal veins. PA notified immediately.”

    A portable Doppler ultrasound caught it. The device worked because someone designed it to. That’s why we only secure medical devices, and why we treat every submission like a life depends on it.

    Christian Espinosa, Founder & CEO of Blue Goat Cyber
    A health scare made the mission personal. Patients depend on connected devices working safely - every time. That's not a slogan. It's why we only do MedTech.
    Christian Espinosa · Founder & CEO
    Where the name comes from

    Why Blue Goat?

    Christian is an avid mountain climber. On the trails, he's watched goats find footing on terrain that would stop almost anything else - relentless, resilient, focused on the next foothold. That's the discipline we wanted the company to embody.

    The Blue is for the impossibly clear sky over a snow-covered ridgeline - clarity, trust, and limitless potential. Together it captures what we're trying to bring to MedTech security: steady footing on hard terrain, with no shortcuts to the summit.

    Purpose

    Medical device security is patient safety.

    Why we exist: so the devices people depend on can't be turned against them.

    Vision

    Connected medical devices that are secure by design and resilient for their entire service life.

    The world we are working toward, with no end date.

    Mission

    By 2028, help medical device teams get 1,000 devices through FDA review with zero cybersecurity-driven rejections, and teach the industry to start cybersecurity early.

    What we do daily, with a deadline: secure the devices in front of us, and through books, stages, podcasts, webinars, and mentoring, help every other team understand what cybersecurity means for their device before it costs them.
    Credibility

    Track record that backs the story.

    The numbers behind the engagements - and the manufacturers who've trusted us with their submissions.

    In-house

    Cybersecurity scope delivered in-house, never subcontracted

    Submissions

    Medical device submissions supported

    Team experience

    MedTech security experience, starting at Christian's first company, Alpine Security, and carried into Blue Goat

    SDVOSB

    Certified

    Service-disabled veteran-owned business

    1. 01

      275+

      Submissions supported

      Across many device types

    2. 02

      About 50

      FDA deficiency letters reviewed

      We know what reviewers ask

    3. 03

      2022

      Founded

      MedTech security only

    4. 04

      Red team

      Founder's red-team and DoD cyberwarfare background

      We test like attackers

    Counts as of October 2026.

    Trusted by MedTech leaders

    • Intuitive Surgical logo, Blue Goat Cyber client
    • bioMérieux logo, Blue Goat Cyber client
    • Natera logo, Blue Goat Cyber client
    • Inogen logo, Blue Goat Cyber client
    • Medivis logo, Blue Goat Cyber client
    • Velico Medical logo, Blue Goat Cyber client

    Global client footprint

    MedTech teams we secure, mapped

    108+HQ locations
    19Countries

    Hover any pin to see the HQ location. Pinch / scroll to zoom. Representative selection of MedTech, IVD, SaMD, and digital-health organizations Blue Goat Cyber has supported across 19 countries.

    Memberships

    Member, Medical Technology Enterprise Consortium (MTEC)

    Blue Goat Cyber is a member of MTEC, a nonprofit consortium that brings together medical technology companies, researchers, and government to speed up the development of medical solutions. Christian Espinosa presented the MTEC webinar on the eight cybersecurity deficiencies the FDA raises most often.

    Our MTEC member listing →Watch the MTEC webinar →

    In the press & on stage

    Recent recognition and speaking engagements

    View all coverage →
    • MedTech World North America 2026

      Cybersecurity Partner of the Year

    • MedTech Malta 2025

      MedTech Service Provider Excellence Award

    • MedTech Innovator APAC

      Selected for Asia Pacific finals

    • MedTech World Middle East

      Title Sponsor, Dubai 2026

    • LSI USA '26

      Sponsor & panelist, Dana Point

    • Med Device Cyber Podcast

      Christian Espinosa, host

    Success outcomes

    What commitment-backed work has produced.

    • Cleared 510(k), De Novo, PMA, and IDE submissions across robotic surgery, diagnostics, wearables, and SaMD.
    • Resolved FDA cybersecurity deficiency letters at no additional cost - every engagement is commitment-backed.
    • Reduced average premarket cybersecurity review cycles for repeat clients by catching gaps before submission.
    • Stood up post-market SBOM, vulnerability monitoring, and coordinated disclosure programs aligned to Section 524B.
    Devices we secure

    From robotic surgery to wearables.

    Every category below is something we've taken through FDA cybersecurity review.

    Robotic surgery

    Endoscopic, laparoscopic, and surgical robotics platforms.

    Diagnostics & IVD

    Hematology, molecular diagnostics, and clinical analyzers.

    Wearables

    Continuous monitors, biosensors, and patient-worn devices.

    SaMD

    Software as a medical device, mobile, and cloud companions.

    Implantables

    Pacemakers, neurostimulators, and active implantable devices.

    Imaging

    AI-enabled imaging systems and PACS-integrated platforms.

    Drug delivery

    Infusion pumps, autoinjectors, and connected combination products.

    Patient monitors

    Bedside, ambulatory, and remote patient monitoring.

    Milestones

    How we got here.

    A decade of MedTech cybersecurity work - walk the path from Alpine Security to Blue Goat Cyber.

    Jump to year

    1. 2026Company

      Judge, Sponsor, & Mentor - MedTech Innovator Asia Pacific 2026

      Blue Goat Cyber gives back to the global MedTech community as a judge, sponsor, and mentor for MedTech Innovator Asia Pacific - the world's largest accelerator for medical device innovation - helping APAC startups navigate FDA, EU MDR, and global cybersecurity compliance.

    2. 2026Award

      Medical Device Cybersecurity Solution of the Year

      MedTech Outlook names Blue Goat Cyber its 2026 Medical Device Cybersecurity Solution of the Year - recognizing patient-safety-first engagements that deliver market access and regulatory clearance without the chaos.

    3. 2025Company

      275+ FDA submissions supported, zero cybersecurity rejections

      275+ FDA submissions supported, zero cybersecurity rejections, across 12+ device classes. Expand the team with senior MedTech security and regulatory hires.

    4. 2025Award

      MedTech Service Provider Excellence Award

      Awarded at the MedTech World Malta 2025 Awards Gala (sponsored by the Malta Medicines Authority) for global leadership in medical-device cybersecurity - threat modeling, secure-by-design, SBOM, and lifecycle vulnerability management.

    5. 2026Award

      Medical Device Cybersecurity Partner of the Year

      MedTech World North America 2026 Awards (in collaboration with CS Lifesciences) names Blue Goat Cyber Cybersecurity Partner of the Year - recognition of our patient-safety-first approach to FDA cybersecurity submissions and global medical device security partnerships.

    6. 2026Industry

      FDA finalizes premarket cybersecurity guidance

      On February 3, 2026, the FDA finalizes "Cybersecurity in Medical Devices: Quality Management System Considerations and Content of Premarket Submissions" (superseding the September 27, 2023 version and the June 2025 update). Defines the seven-section submission format reviewers now enforce at Technical Screening.

    7. 2025Industry

      FDA AI-enabled device guidance released

      FDA's January 2025 guidance sets expectations for AI-enabled medical devices - transparency, real-world monitoring, change control, and cybersecurity across the model lifecycle.

    8. 2024Content

      Owned media: MDC Podcast + Webinar series launch

      Christian launches the Med Device Cyber Podcast and a companion technical webinar series - translating FDA expectations, threat modeling, SBOM, and postmarket security for product, quality, and regulatory leaders.

    9. 2023Industry

      FDA Section 524B becomes law (PATCH Act)

      Section 524B of the FD&C Act gives FDA refuse-to-accept authority for cyber devices and mandates SBOMs, threat models, and postmarket plans in every premarket submission. Cybersecurity becomes table stakes for clearance.

    10. 2023Content
      The In-Between: Life in the Micro book cover

      The In-Between: Life in the Micro published

      Christian releases his memoir The In-Between: Life in the Micro (Shrinking Ego, Dec 12, 2023) - a focused look at the small moments that shape relationships, business, and life.

    11. 2022Company

      Blue Goat Cyber founded

      Christian leaves CISO Global and launches Blue Goat Cyber from Pocatello, Idaho - a medical-device-only specialist with commitment-backed engagements, fixed-fee pricing, and end-to-end coverage from premarket through postmarket.

    12. 2022Company

      A personal health scare

      In O'Fallon, IL, a portable Doppler ultrasound helps diagnose Christian's life-threatening blood clots. The stakes of connected-device safety become personal.

    13. 2021Content
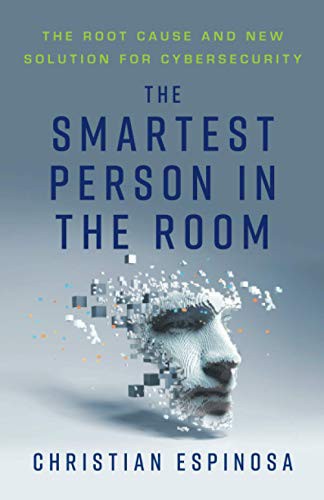
      The Smartest Person in the Room book cover

      The Smartest Person in the Room published

      Christian publishes The Smartest Person in the Room - a leadership book on the human side of cybersecurity, drawn from years of running red teams and building Alpine.

    14. 2020Company

      Alpine sold to Cerberus Sentinel - 50+ submissions cleared

      By the time Alpine is sold to Cerberus Sentinel, the team has cleared 50+ medical device cybersecurity submissions (510(k), De Novo, PMA) across imaging, diagnostics, and connected devices with zero clearance failures - the foundation of the methodology Blue Goat Cyber would later productize.

    15. 2015Company

      Alpine launches MedTech cybersecurity division

      Alpine Security spins up one of the earliest dedicated MedTech cybersecurity practices - pen testing, threat modeling, and FDA-aligned compliance support for medical device manufacturers.

    16. 2014Company

      Alpine Security founded

      Christian Espinosa founds Alpine Security in Fairview Heights, IL - a cybersecurity firm built on hands-on penetration testing, incident response, and security training.

    Core beliefs

    What we stand for.

    Seven beliefs that shape how we approach every medical device cybersecurity engagement. See scenarios and examples for each →

    Patient safety comes first

    Every patient deserves secure, reliable medical devices designed to protect lives without compromise. Safeguarding the people who depend on your devices is our top priority.

    Security enables innovation

    Cybersecurity is the foundation for advancing healthcare. By addressing risks early, we empower manufacturers to deliver groundbreaking, life-saving solutions with confidence.

    Trust is earned through action

    Trust is built by delivering solutions that meet the highest standards of security and compliance - not just compliant, but truly secure.

    Proactive prevents future threats

    We work ahead of emerging threats so you stay ahead of risk. Proactive measures prevent costly vulnerabilities and ensure long-term device security.

    Compliance is the starting point

    Meeting regulatory requirements is just the beginning. True success means devices that inspire trust and protect patients in a rapidly evolving landscape.

    Collaboration drives success

    We work side-by-side with manufacturers to solve challenges and build customized solutions. Your success is our mission.

    The stakes demand excellence

    Lives depend on what we do. We're committed to delivering exceptional cybersecurity solutions every time, upholding the highest standards of quality and care.

    How we operate

    Team core values.

    The day-to-day mantras every Blue Goat team member lives by.

    • Think flexibly to solve problems
    • Find the opportunity in every situation
    • Listen carefully, respond clearly
    • Own the problem, find the solution
    • Grow beyond your comfort zone
    • Obsess over critical details
    • Learn fast, learn often
    Our team

    Specialists, not generalists.

    A focused team of MedTech security operators - small enough that you always know who's accountable.

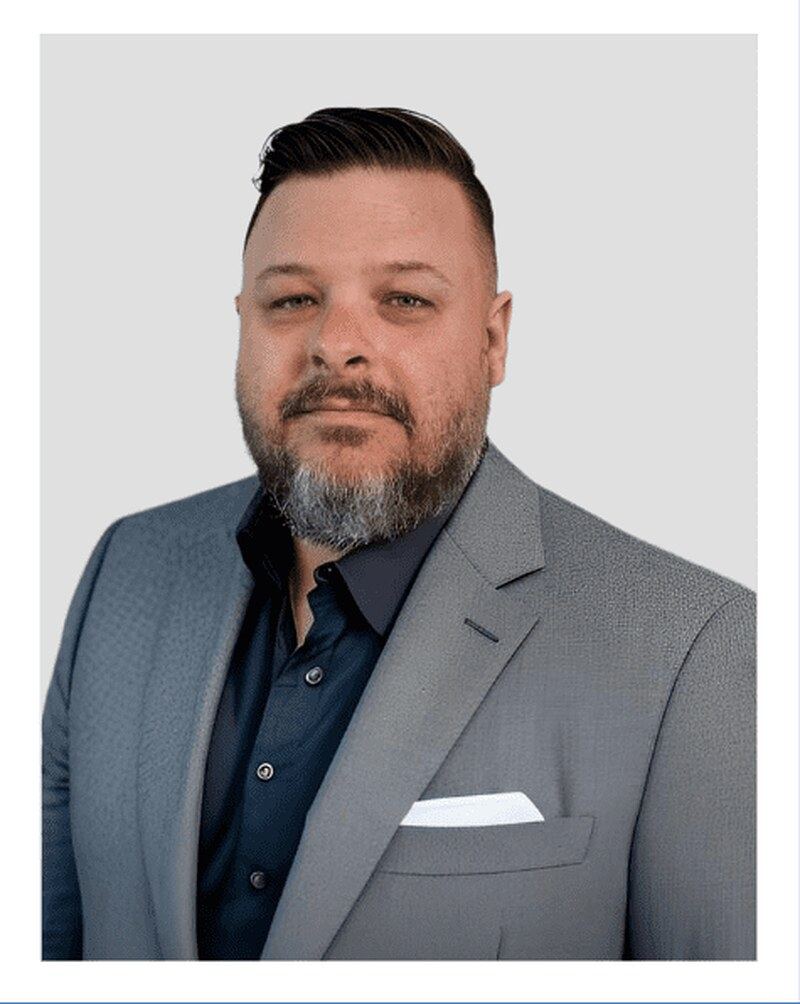
    Headshot of Christian Espinosa, Founder & CEO at Blue Goat Cyber

    Christian Espinosa

    Founder & CEO

    U.S. Air Force Academy graduate and veteran with 30+ years in cybersecurity. Founded Alpine Security in 2014 (acquired 2020), then Blue Goat Cyber in 2022. Blue Goat track record: 275+ FDA submissions supported, zero cybersecurity rejections. Author of three books including The Smartest Person in the Room. Ironman triathlete and mountaineer.

    Connect on LinkedIn
    Headshot of Myles Kellerman, CTO at Blue Goat Cyber

    Myles Kellerman

    CTO

    Chief Technology Officer leading medical device and IoMT security testing, threat modeling, and pen testing aligned with FDA premarket and postmarket cybersecurity expectations. Oversees device, application, red team, and physical assessments across Class II and Class III programs, plus internal tooling that keeps submission-grade evidence consistent. 18+ years in IT, 13+ in cybersecurity, with earlier work on aircraft and embedded defense systems that translates directly to safety-critical MedTech.

    Connect on LinkedIn
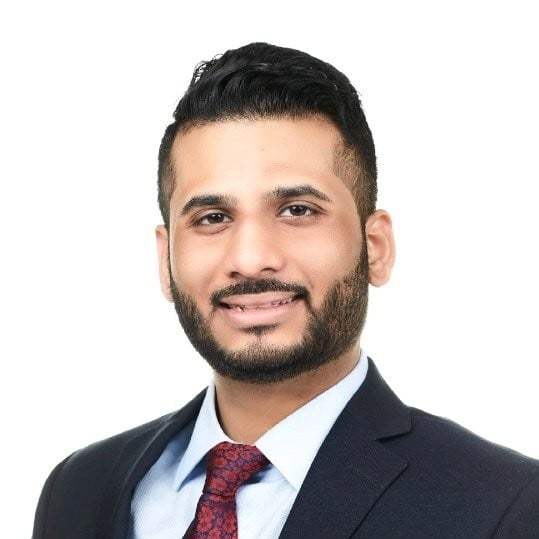
    Professional headshot of Jordan John, VP of Regulatory Affairs & Compliance at Blue Goat Cyber - a smiling man with short dark hair and a beard, wearing a navy suit, light blue shirt, and red patterned tie, photographed against a plain white background.

    Jordan John

    VP, Regulatory Affairs & Compliance

    Owns the regulatory and compliance lane across FDA premarket and postmarket submissions. Aligns cybersecurity evidence with Section 524B, eSTAR, and the broader regulatory file so every package holds together end-to-end.

    Headshot of Melissa Espinosa, VP, Strategic Partnerships at Blue Goat Cyber

    Melissa Espinosa

    VP, Strategic Partnerships

    Leads Blue Goat's channel and partner network across MedTech consulting, regulatory, and technology firms. A former cardiac stepdown nurse, she brings a bedside view of how device security failures reach patients - and uses it to shape partnerships that keep clinical risk, not just compliance, at the center of every engagement.

    Connect on LinkedIn
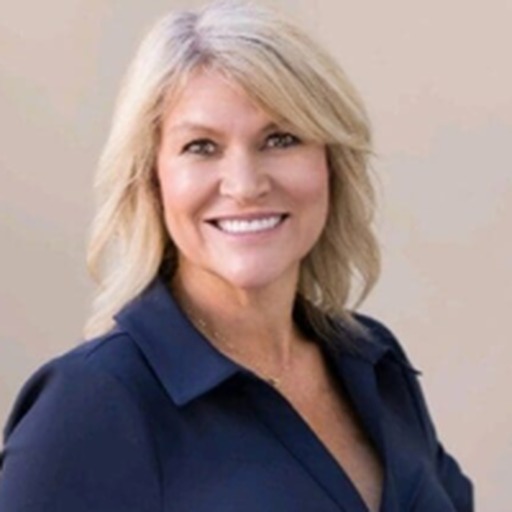
    Headshot of Kristy Kennedy, VP, Sales at Blue Goat Cyber

    Kristy Kennedy

    VP, Sales

    Global commercial leader focused on medical device and life sciences. 25+ years helping MedTech manufacturers commercialize regulated products - from Class II device launches to distributor and OEM partnerships - now applied to helping device makers scope FDA-aligned cybersecurity engagements without slowing their submission timeline.

    Connect on LinkedIn
    Professional headshot of Michelle Hughes, Director of Operations at Blue Goat Cyber - a smiling Black woman with short curly hair, wearing coral-pink top and a blue-and-white striped blazer, photographed indoors against a soft neutral background.

    Michelle Hughes

    Director of Operations

    Drives complex MedTech cybersecurity engagements from kickoff through FDA clearance. Coordinates technical, QA, and regulatory workstreams to keep submissions moving and clients informed at every checkpoint.

    Professional headshot of Sarah Beach, Senior Project Manager at Blue Goat Cyber - a white woman with long straight auburn hair, wearing a white blouse, photographed against a plain light-gray background with a neutral expression.

    Sarah Beach

    Senior Project Manager

    Owns engagement timelines, deliverables, and FDA interactions end-to-end. Keeps threat models, pen tests, SBOMs, and submission packages on rails so engineering and regulatory teams stay aligned without surprises.

    Read full leadership bios→
    FAQ

    FDA cybersecurity questions, answered.

    What MedTech founders, regulatory leads, and product security teams ask us most often - and how our process delivers a submission-ready cybersecurity package.

    Blue Goat in the Wild

    On stage, on the floor, and on the road

    Title Sponsor of MedTech World. Sponsor/judge/mentor at MedTech Innovator APAC, HLTH, AdvaMed, Verge across US, EMEA, APAC.

    Reception · MedTech World Dubai
    Speaking · MedTech World
    Panel · MedTech Innovator APAC · Singapore (Judge & Mentor)
    Panel · MedTech World Dubai (DHA, EHS, Malta)
    Panel · CS Lifesciences
    Interview · MedTech World
    Interview · KPMG at MedTech World
    Booth · HLTH
    Booth · The MedTech Conference · AdvaMed
    Booth · LSI Europe (Cybersecurity Sponsor)
    Booth · 'Patient Safety, Not Only Data Protection' · MedTech World
    Sponsor Floor · MedTech World
    Partnership · Pen Testing Booth
    Partnership · Hong Kong MedTech Association
    Site Visit · Surgical Robotics Lab · Hong Kong
    Keynote · LSI Asia '26 · Singapore
    Booth · LSI Asia '26 (Cybersecurity Sponsor)
    Booth · LSI Asia '26 · Melissa on the floor
    Booth · LSI Asia '26 · Melissa and Dinia
    Gala · LSI Asia '26 · Christian and Melissa
    Gala · LSI Asia '26 · With peers and partners
    Luncheon panel · MedTech World Asia '26 · Hong Kong
    Awards dinner · MedTech World Asia '26
    Gala · MedTech World Singapore
    Podcast guest · Singapore studio
    Booth · MedTech World Bay Area 2025 (Gold Sponsor)
    Awards · MedTech World 2025
    Evening reception · MedTech World Dubai
    Panel · MedTech World Middle East
    Main stage · MedTech World 2026
    Black-tie gala · MedTech World
    Booth · HLTH
    Booth table · MedTech World
    Teaching · MedTech Innovator APAC 2025
    Desert tour talk · MedTech World Dubai
    With Tai Tan · MedTech World
    Book signing · The Smartest Person in the Room
    Podcast interview · MedTech World Malta
    Give back

    Programs and projects we sponsor and support

    We reinvest in the MedTech cybersecurity community by mentoring innovators and building free public resources. These are the programs and projects Blue Goat Cyber proudly sponsors or supports.

    MedTech Innovator APAC thumbnail
    Featured · Judge, sponsor, & mentor

    MedTech Innovator APAC

    Judge, sponsor, & mentor for APAC MedTech innovators

    Blue Goat Cyber proudly gives back to MedTech Innovator APAC as a judge, sponsor, and mentor - helping early-stage MedTech companies across the Asia Pacific region strengthen cybersecurity and FDA-readiness as they scale.

    Visit site
    • Code Blue Chart thumbnail

      Code Blue Chart

      Public timeline of MedTech cyber events

      A sourced, public-record timeline of 86+ medical-device cybersecurity events from 1985 to today - recalls, FDA/CISA advisories, and incidents tied to patient harm.

      Visit site
    • Med Device Cyber Podcast thumbnail

      Med Device Cyber Podcast

      Conversations with MedTech security leaders

      Interviews and field notes for product security, regulatory, and engineering teams shipping safer connected devices.

      Visit site
    • MDC Crosswalk thumbnail

      MDC Crosswalk

      Map controls across MedTech standards

      A free crosswalk between FDA guidance, ANSI/AAMI SW96, ISO 13485, ISO 14971, and related frameworks - built to save submission and audit prep time.

      Visit site
    • MedTech Cyber Tips thumbnail

      MedTech Cyber Tips

      Bite-sized guidance for builders

      Short, practical tips for engineers, regulatory leads, and founders working on connected medical devices.

      Visit site
    • AI SaMD thumbnail

      AI SaMD

      AI/ML-enabled SaMD resources

      A focused resource on cybersecurity, safety, and regulatory expectations for AI/ML-enabled Software as a Medical Device.

      Visit site
    • MDC Misconceptions thumbnail

      MDC Misconceptions

      Debunking medical device cybersecurity myths

      A free public resource that calls out the most common myths about medical device cybersecurity - from "we passed pen testing, so we're FDA-ready" to "SBOMs are just a list." Built to help manufacturers separate marketing from regulatory reality.

      Visit site
    • MedTech Terms thumbnail

      MedTech Terms

      Plain-English MedTech & cyber glossary

      A free, plain-English glossary of medical device, regulatory, and cybersecurity terminology - built to help engineers, regulatory teams, and founders speak the same language as FDA reviewers and notified bodies.

      Visit site
    • MedTech Launch Guide thumbnail

      MedTech Launch Guide

      Step-by-step playbook for launching a MedTech company

      A free, founder-focused guide covering the practical steps to start, fund, and launch a medical device company - from idea validation and regulatory strategy through clinical, reimbursement, and commercialization.

      Visit site
    • APPSUK Foundation thumbnail
      Charity sponsor

      APPSUK Foundation

      Healthcare and humanitarian relief in Pakistan

      Blue Goat Cyber proudly supports the APPSUK Foundation - the charitable arm of the Association of Pakistani Physicians and Surgeons of the United Kingdom - funding mobile health units, cataract clinics, prosthetic limbs, education, and disaster relief for underserved communities in Pakistan.

      Visit site

    About these sponsorships

    How do you choose which projects to sponsor?
    +
    We back independent, non-commercial efforts that materially help the MedTech cybersecurity community - open educational resources, podcasts, mentorship programs, and public datasets. We prioritize projects with a clear public benefit, transparent ownership, and no conflicts of interest with our client work.
    Can my project apply for sponsorship?
    +
    Yes. Reach out through our contact page with a short description of the project, who it serves, and what kind of support you're looking for. We review new requests on a rolling basis and respond even when we can't sponsor.
    How often is this list updated?
    +
    We refresh the list quarterly, and immediately whenever a sponsorship starts, ends, or changes scope - so what you see here always reflects active commitments.
    Ready when you are

    Secure your device before it reaches patients.

    30-minute strategy session. No cost, no commitment - just answers from people who've supported 275+ FDA submissions, with zero cybersecurity rejections.

    Book strategy sessionExplore services