Blue Goat CyberBlue Goat CyberSMMedical Device Cybersecurity
    Start here
    Services
    • Medical Device Cybersecurity Consulting
    • FDA Premarket Cybersecurity Package
    • Medical Device Penetration Testing Services
    • FDA Deficiency Response
    • FDA Postmarket Cybersecurity
    • Medical Device Threat Modeling
    • eSTAR Cybersecurity Documentation Support
    See all services
    Products

    Blue Goat products

    • GoatWatch logoGoatWatchSBOM risk management for medical devices
    About
    Resources

    Learn

    • Blog
    • Podcast
    • Webinars
    • Talks & workshops
    • Glossary
    • FAQs

    Playbooks & Tools

    • Guides
    • Playbooks (PDF)
    • Infographics
    • Interactive Tools

    Signals & Proof

    • Goat FeedNew
    • News
    • Medical Device Security News
    • The Goat's Weekly
    • Case Studies
    • Proof / Receipts
    All resources, topic hubs, & collections →
    ⌘K
    Book Strategy SessionHow to prepare →
    Blue Goat Cyber

    Full-service medical device cybersecurity. We protect patients by securing connected medical devices from design through postmarket.

    275+ FDA submissions supported, zero cybersecurity rejections · Mission: 1,000 by 2028

    SDVOSB · Service-Disabled Veteran-Owned Small Business

    We sponsor 10 community projects →

    Services

    • FDA Premarket Cybersecurity Package
    • FDA Deficiency Response
    • Medical Device Threat Modeling
    • Medical Device Penetration Testing Services
    • FDA Postmarket Cybersecurity
    • All services →
    Services
    • FDA Premarket Cybersecurity Package
    • FDA Deficiency Response
    • Medical Device Threat Modeling
    • Medical Device Penetration Testing Services
    • FDA Postmarket Cybersecurity
    • All services →

    Company

    • About
    • Core values
    • Manifesto
    • Leadership
    • Why Us
    • Partners
    • Careers
    • Press
    • Press kit
    • Contact
    • Company overviewPDF
    Company
    • About
    • Core values
    • Manifesto
    • Leadership
    • Why Us
    • Partners
    • Careers
    • Press
    • Press kit
    • Contact
    • Company overviewPDF

    Resources

    • Blog
    • Guides
    • Podcast
    • Case studies
    • Monthly Pulse newsletter
    • All resources →
    Resources
    • Blog
    • Guides
    • Podcast
    • Case studies
    • Monthly Pulse newsletter
    • All resources →

    Get in touch

    • info@bluegoatcyber.com
    • 844-939-GOAT
    • Book a strategy session →
    • 1776 N Scottsdale Rd, Unit 727
      Scottsdale, AZ 85257Serving clients worldwide

    Follow

    © 2026 Blue Goat Cyber. All rights reserved.

    • Privacy
    • Terms
    • Cookies
    • Sitemap
    • Accessibility
    • CVD

    MedTech Cybersecurity · Since 2022

    The Receipts

    Proof, not adjectives.

    Securing medical devices since 2022. A track record across every major FDA cybersecurity shift - 275+ FDA submissions supported, zero cybersecurity rejections, the standards we map to, the certifications we hold, redacted deliverables you can review, and the press, podcasts, and clients who've vouched for us.

    Book a strategy sessionSee sample deliverables

    Last updated: Nov 2026 · Self-reported

    FDA submissions supported
    Cyber scope owned in-house
    Cyber-related RTAs
    Years in MedTech cyber
    Breakdown

    275+ FDA submissions supported, zero cybersecurity rejections. The breakdown.

    Competitors quote round numbers. We quote what's actually in the binder. Every entry below comes from a real FDA submission we supported between 2019 and today.

    220+
    510(k) submissions
    7
    De Novo submissions
    22
    PMA submissions
    14
    Device classes covered

    0 cybersecurity-related RTAs or AI-Rs across these submissions, as of this update. Numbers refresh quarterly.

    Track record

    Securing medical devices since 2022.

    A track record focused exclusively on medical device cybersecurity. Our methodology, templates, and review playbooks have been refined through every major FDA cybersecurity shift - draft guidance, the PATCH Act, Section 524B, the September 2023 premarket guidance, QMSR modernization, the June 2025 interim final guidance, and the Feb 3, 2026 final premarket guidance. When the rules change, our deliverables already match.

      2014

      Started in medical device cybersecurity

      Began securing connected medical devices when 'MedTech cybersecurity' was barely a category. Built our first FDA premarket cyber packages.

      2018

      FDA premarket cybersecurity guidance (draft)

      Adapted our methodology to FDA's draft premarket cybersecurity guidance - SBOM thinking, threat modeling, security risk management - well before it became table stakes.

      2023

      Section 524B becomes law

      Re-tooled deliverables for the new statutory authority: refuse-to-accept (RTA) for cyber, SBOMs in submissions, postmarket plans. Zero cyber-related RTAs since.

      2023

      FDA September 2023 premarket guidance (superseded)

      Aligned templates and traceability matrices to SPDF expectations and AAMI SW96 / TIR57 inputs. Later superseded by the June 2025 final and then the Feb 3, 2026 final guidance.

      2024

      QMSR (21 CFR Part 820) modernization published

      The FDA published the QMSR final rule harmonizing 21 CFR Part 820 with ISO 13485. We updated quality-system inputs, including cybersecurity risk management touchpoints, in anticipation of the Feb 2, 2026 effective date.

      2025

      FDA June 2025 premarket guidance (superseded)

      Interim final that clarified SPDF expectations, SBOM/VEX content, and reviewer patterns after two years of Section 524B enforcement. We refreshed every template between Sept 2023 and Feb 2026 to match. Superseded by the Feb 3, 2026 final.

      2026

      QMSR effective + FDA Feb 3, 2026 final premarket guidance

      QMSR (21 CFR Part 820 aligned to ISO 13485) took effect Feb 2, 2026; the FDA issued its final premarket cybersecurity guidance the next day. Current binding edition. Refreshed every template, threat model, and SBOM/VEX workflow to the seven-section submission format reviewers now enforce at Technical Screening - so reviewers find each section where they expect it.

    Twelve years of reps means our SPDF, threat model, SBOM/VEX, and AI-letter-response templates have been pressure-tested through hundreds of submissions - not invented yesterday in response to the latest guidance.

    Engagements

    Real engagements with real numbers.

    Anonymized to honor NDAs. Every standard, timeline, and deliverable is exactly what we shipped.

    All case studies
    Imaging & AI/SaMD

    Series-B imaging AI manufacturer (US, ~60 FTEs)

    30-day FDA response window

      Read engagement
      Cardiovascular

      Cardiac remote-monitoring manufacturer (US/EU dual market)

      16 weeks pre-submission (Jan - Apr 2025), first-cycle clearance in 84 days

        Read engagement
        Neuromodulation / Active Implantables

        Implantable neurostimulator manufacturer (Class III, life-sustaining)

        11 months across pre-PMA and PMA review (May 2024 - Apr 2025)

          Read engagement
          See the work

          Sample deliverables.

          Most firms won't show you what they actually ship. Here are real, redacted artifacts from real submissions - the same files we'd hand your team.

          Coming soon

          Redacted CycloneDX 1.5 SBOM

          Real SBOM from a Class II SaMD submission with 312 components mapped against KEV/EPSS. Client name and component fingerprints redacted.

          PDF · 14 pages

          Coming soon

          Threat model excerpt (STRIDE + ISO 14971)

          Two pages from a 47-threat STRIDE model showing the traceability matrix from threat → harm → control. Demonstrates AAMI SW96 conformance.

          PDF · 2 pages

          Coming soon

          FDA AI-R cybersecurity response letter

          12-page response to a real FDA cybersecurity AI Request, with reviewer questions verbatim and our line-by-line response. Submission identifiers redacted.

          PDF · 12 pages

          Coming soon

          Pen test executive summary

          Sample executive summary page from a medical device pen test report - finding rollup, severity heatmap, and remediation roadmap.

          PDF · 1 page

          Want a sample sent over? Email info@bluegoatcyber.com and we'll share the redacted version under a mutual NDA.

          Credentials

          Certifications.

          Held across the team. We don't list expired certs or letters that look impressive but aren't relevant to MedTech.

          CISSP
          (ISC)²
          Information security leadership
          CSSLP
          (ISC)²
          Secure software lifecycle
          OSCP
          Offensive Security
          Hands-on offensive testing
          CRTE
          Pentester Academy
          Red team enterprise
          CARTP
          Altered Security
          Azure red team
          GPEN
          GIAC
          Penetration testing
          Standards

          Standards we map to.

          Every deliverable cross-references the relevant guidance and standards line-by-line. No hand-waving.

          • FDA Premarket Cybersecurity Guidance (Feb 3, 2026 final)
          • FDA Section 524B (PATCH Act)
          • AAMI SW96:2023
          • AAMI TIR57
          • IEC 81001-5-1
          • IEC 62304
          • ISO 14971
          • NIST SP 800-30 / 800-53
          • MDCG 2019-16 (EU MDR)
          Browse the standards glossary
          Open methodology

          The work is published.

          Competitors saying the same words can't show the same work. Here's ours, in public.

          Penetration testing methodology

          Our full pen test methodology - published, not gatekept.

          Coordinated Vulnerability Disclosure (CVD)

          Public CVD policy with intake form. Researchers can report safely.

          Standards glossary

          Plain-English glossary of every FDA, AAMI, IEC, ISO standard we map to.

          Topic hubs

          Six topic hubs aggregating our work, guides, and references on each subject.

          In their words

          What clients say.

          All testimonials

          Blue Goat Cyber helped us navigate our first end-to-end cybersecurity testing for our wearable medical device. Their communication was excellent, their timeline exceeded expectations, and their report helped us achieve FDA clearance without any additional questions. It was a truly seamless experience.
          Anna Norman, VP of Product at InfoBionic.Ai
          Anna Norman
          VP of Product · InfoBionic.Ai

          Blue Goat provided testing on our system for cybersecurity and provided the necessary documentation to add to our regulatory submission. They were very knowledgeable in the requirements, and performed the testing onsite which made the logistics of equipment availability easier for us. The communication was excellent, and they were able to expedite the testing and provide final reports in a very short period of time. My experience with this team was fantastic and I would not hesitate to use them again in the future.

          Bernie Lane
          Engineer Manager · CSA Medical Inc

          Blue Goat Cyber takes the burden off our engineers and makes FDA cybersecurity requirements easy to understand. Their expertise and smooth process mean we can focus on our product, not the paperwork. The organized documentation, perfectly formatted for eSTAR, saves us countless hours.
          Amy Lynn, Chief Compliance Officer at Medivis
          Amy Lynn
          Chief Compliance Officer · Medivis
          Third-party

          Press, podcasts, and awards.

          Validation we didn't write ourselves.
          All awards
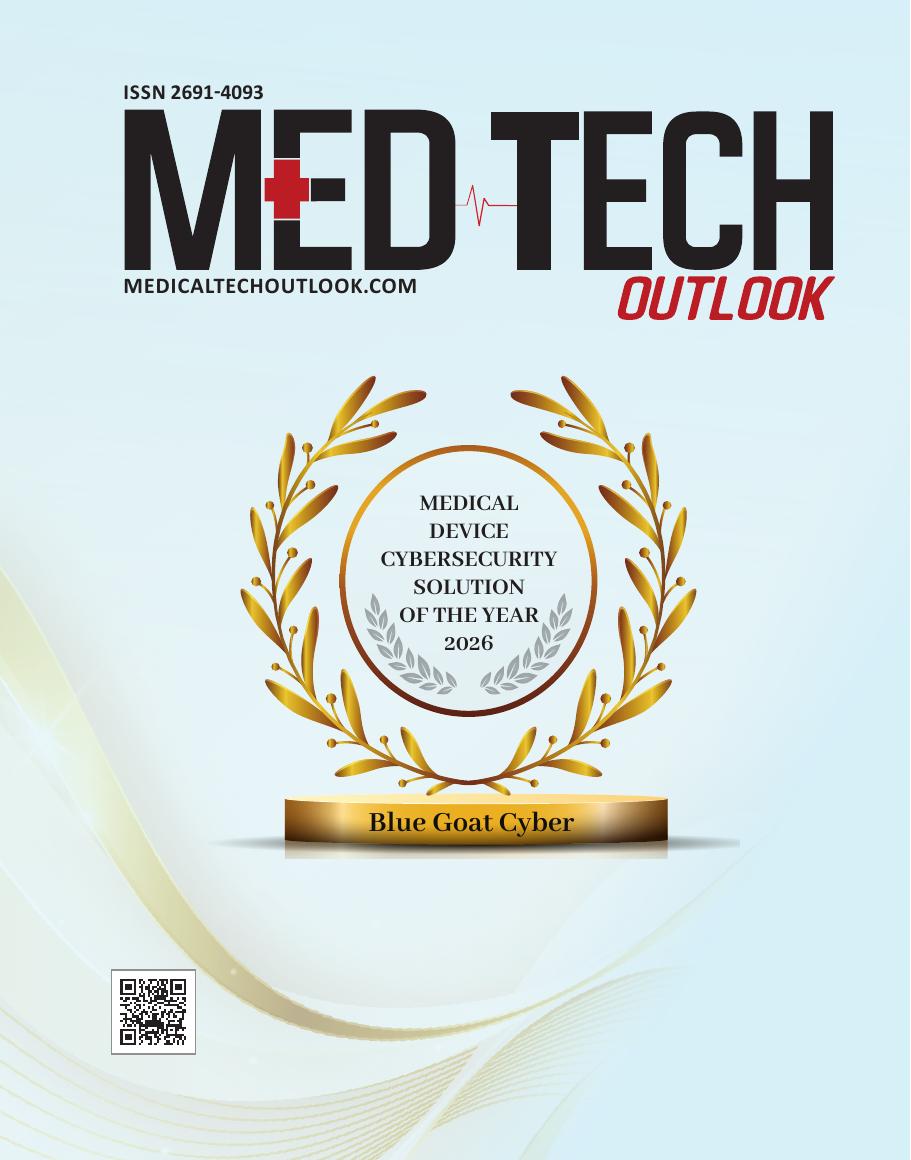
          Medical Device Cybersecurity Solution of the Year 2026 - Blue Goat Cyber cover story - featured in Medical Tech Outlook
          Award2026
          Medical Tech Outlook

          Medical Device Cybersecurity Solution of the Year 2026 - Blue Goat Cyber cover story

          View
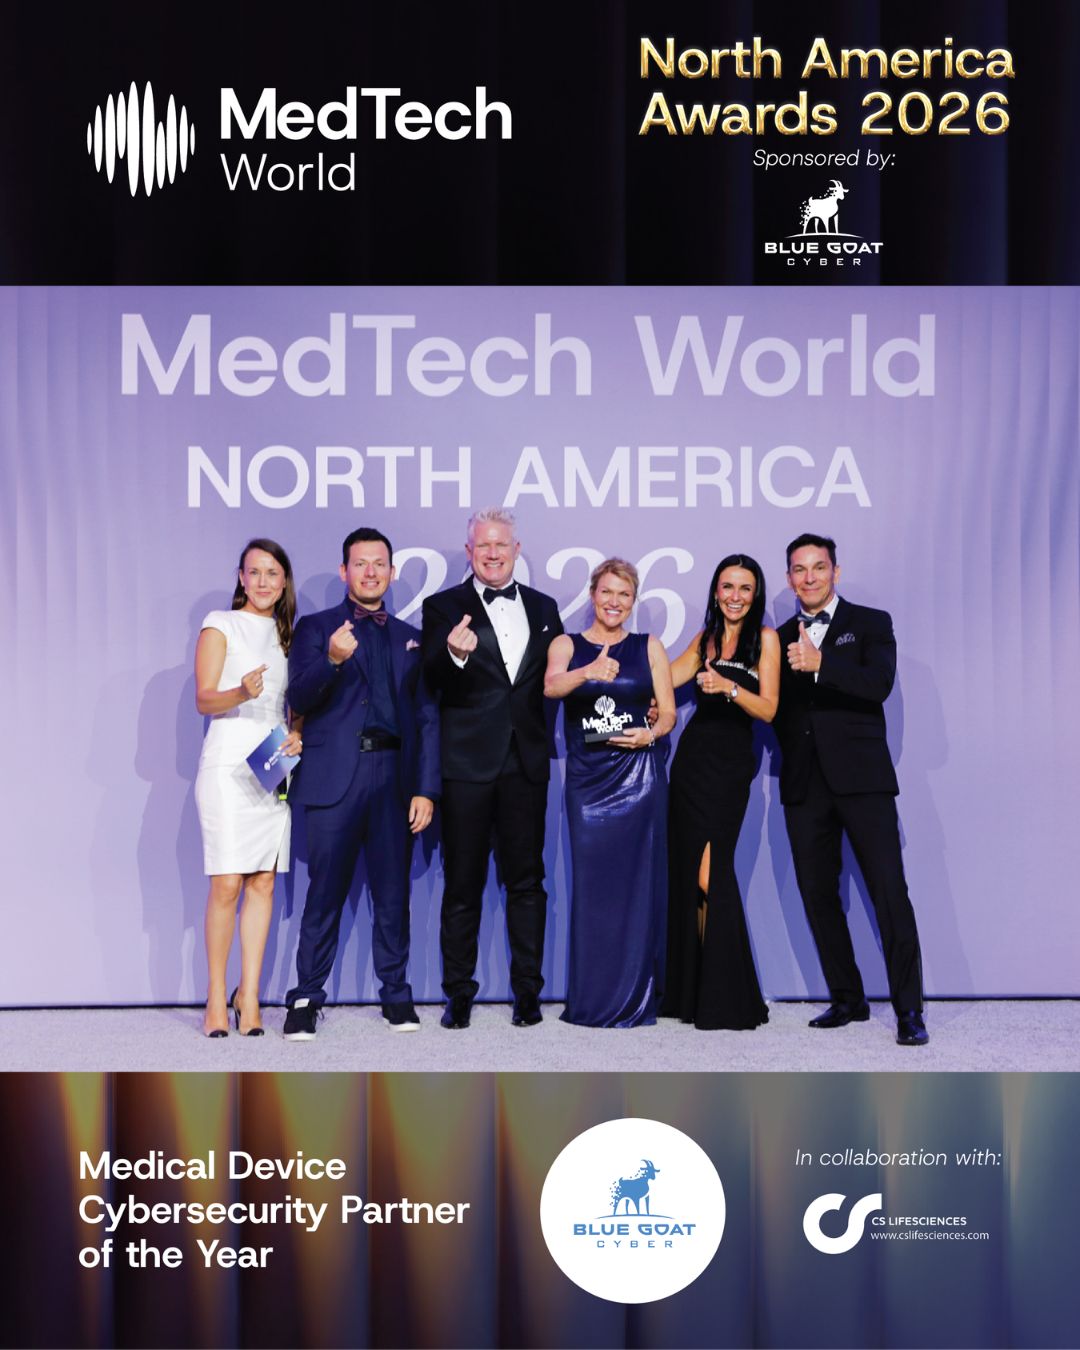
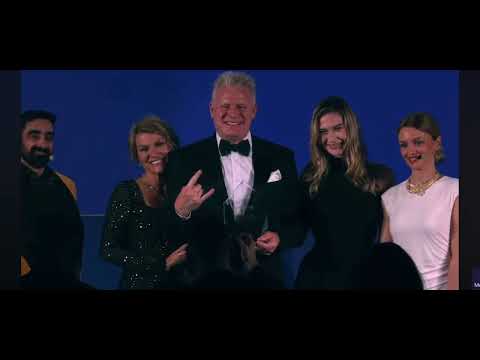
          Medical Device Cybersecurity Partner of the Year - 2026 - featured in MedTech World North America
          Award2026
          MedTech World North America

          Medical Device Cybersecurity Partner of the Year - 2026

          View
          MedTech Service Provider Excellence Award of the Year 2025 - announcement - featured in MedTech World Malta
          Award2025
          MedTech World Malta

          MedTech Service Provider Excellence Award of the Year 2025 - announcement

          View
          Christian Espinosa on FDA cybersecurity expectations and 510(k) pitfalls - featured in The Med Device Cyber Podcast
          Podcast2026
          The Med Device Cyber Podcast

          Christian Espinosa on FDA cybersecurity expectations and 510(k) pitfalls

          View

          Comparing vendors? Send them this page.

          When a competitor uses the same words we do, ask them for the same receipts: named submission breakdown, 0 cyber-related RTAs, certifications with verifiable holders, redacted SBOMs and threat models you can read, and a published methodology.

          Book a strategy sessionSend us a note
          Ready when you are

          Secure your device before it reaches patients.

          30-minute strategy session. No cost, no commitment - just answers from people who've supported 275+ FDA submissions, with zero cybersecurity rejections.

          Book strategy sessionExplore services