Practical playbooks, checklists and decoders we use on every engagement - organized by lifecycle stage.
Looking for a quick answer instead? The FDA medical device cybersecurity FAQ covers Section 524B scope, SBOMs, threat models, CR515 and GMLP, deficiencies, and postmarket duties.
70 guides
Foundational pillars for teams new to FDA medical device cybersecurity.
Why generic IT-security vendors keep blowing FDA submissions - and what to demand from a true MedTech specialist.
Read the guide
FDA cybersecurity guidance for medical devices in plain language: the Feb 3, 2026 final guidance, Section 524B, the 18 deliverables and eSTAR v7.0 filing.
Read the guide
FDA cybersecurity requirements for medical devices under Section 524B: the SBOM, SPDF evidence and postmarket vulnerability plan every cyber device submission needs.
Read the guide
The quantum-resistant algorithms that matter for medical devices, what they cost in flash and bandwidth, the published migration deadlines, and what the FDA expects in your submission today.
Read the guide
FDA Section 524B, IEC 81001-5-1, AAMI TIR57, ISO 14971 and more - what they require, how they connect, and what the FDA expects to see.
Read the guide
A practical playbook for implementing the Secure Product Development Framework across your QMS and SDLC.
Read the guide510(k), De Novo, PMA, and eSTAR-ready deliverables for premarket filings.
How Section 524B and the Feb 2026 guidance apply to drug-device combination products, including the CDER/CDRH lead-center split.
Read the guide
What goes in the Cybersecurity Management Plan reviewers expect in eSTAR v7.0 Slot 1: scope, governance, QMS integration, postmarket commitments, and the most common deficiency patterns.
Read the guide
Learn the specific cybersecurity requirements for a successful De Novo submission. Ensure FDA compliance with threat modeling, SBOM, and pen testing.
Read the guide
Early-stage medical device cybersecurity checklist for connected wearables, mobile apps and cloud platforms: 14 prototype-stage items to settle before formal FDA premarket work begins.
Read the guide
eSTAR 7.1 submission checklist: every step of a 510(k), De Novo, or PMA eSTAR, from downloading the template and preparing documents to paying the fee and sending it to the FDA.
Read the guide
How to package the 18 cybersecurity deliverables into 8 named attachment groupings in eSTAR v7.0, with the most common RTA trigger for each grouping.
Read the guide
A practitioner's checklist of the cybersecurity triggers that cause FDA Refuse-to-Accept (RTA) holds under Section 524B, and how to clear each one before you submit.
Read the guide
A reviewer's-eye technical screening checklist for FDA cyber-device submissions: artifacts, formats, traceability, and the failure modes that turn a soft deficiency into a hold.
Read the guide
How cybersecurity expectations differ across FDA pathways - 510(k), De Novo, PMA, HDE, IDE, Q-Sub, and PDP - under Section 524B and the February 2026 final guidance.
Read the guide
How to author a Predetermined Change Control Plan the FDA will accept: modifications protocol, methods, impact assessment, and cybersecurity coverage.
Read the guide
Master FDA PMA cybersecurity requirements. Learn the technical documentation, risk management, and SPDF requirements needed for a successful Class III submissio
Read the guide
All 18 FDA premarket cybersecurity deliverables, mapped to the February 2026 guidance sections and the non-IVD eSTAR v7.0 fields. Used on 275+ submissions.
Read the guide
Ensure your 510(k) or PMA is compliant. Use our checklist for FDA premarket cybersecurity submissions, covering SBOM, threat models, and pen testing.
Read the guide
Everything a Class III PMA cybersecurity package needs - and how a single integrated team delivers threat modeling, SBOM, pen testing, postmarket plan, and reviewer engagement.
Read the guide
The exact cybersecurity package that gets through 510(k) review without an AI letter. Eight artifacts, common rejection patterns, and a 30-day pre-submission readiness check.
Read the guideWhat cybersecurity documentation an IDE application needs under 21 CFR 812 and the FDA February 3, 2026 premarket guidance, and why Section 524B does not apply.
Read the guideAssemble the cybersecurity content of an IDE application: Appendix 3's five elements, the binding 21 CFR 812.25 requirements behind them, and risk-scaled documentation breadth.
Read the guideHow to write a Predetermined Change Control Plan FDA will accept - structure, the three required components, performance bounds, and a worked example.
Read the guide
A printable, item-by-item checklist for the cybersecurity content of an FDA premarket submission - aligned to the February 2026 final guidance.
Read the guideSTRIDE, ISO 14971, and hazard analysis artifacts reviewers accept.
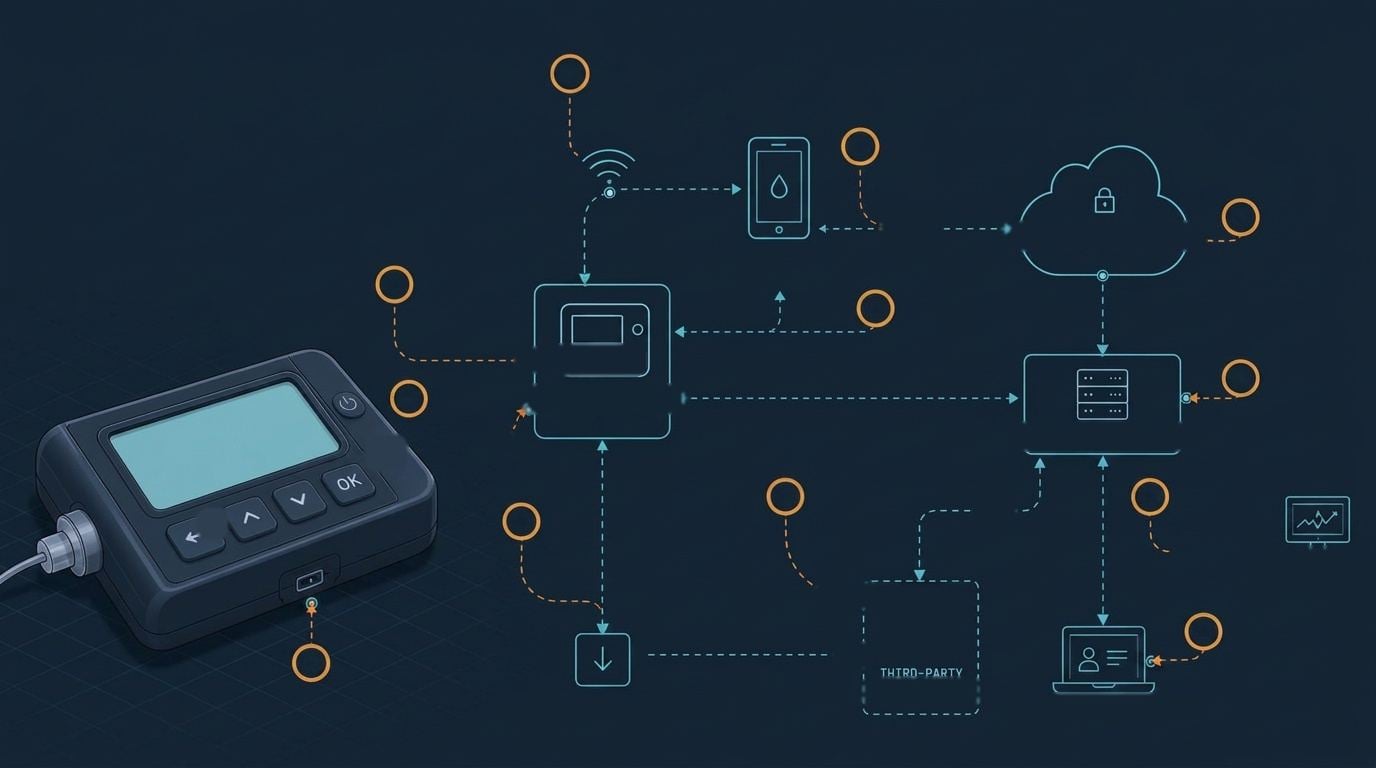
Where threat models fall short of FDA expectations under the 2026 cybersecurity guidance - and how to fix the gaps.
Read the guide
Compare AAMI TIR57 vs TIR97. Learn how these cybersecurity risk management standards differ and how to apply them for FDA premarket and postmarket compliance.
Read the guideThe four security architecture views the FDA's 2026 premarket guidance recommends: global system, multi-patient harm, updatability and patchability, and security use case views, with what each must show.
Read the guide
Step-by-step template to build a threat model FDA reviewers will accept - architecture views, STRIDE, safety mapping, control traceability, and a worked example.
Read the guide
Learn how to implement IEC 81001-5-1 security risk assessments for FDA compliance. Expert guidance on medical device lifecycle security mapping.
Read the guide
How safety hazard analysis and security risk analysis run in parallel and converge at the patient-harm column, with a side-by-side mapping table.
Read the guide
Master STRIDE threat modeling for medical devices. Learn to identify risks, meet FDA premarket requirements, and secure your MedTech ecosystem. Read our guide.
Read the guideSBOM generation, VEX, and third-party vulnerability management.
What an AI bill of materials is, how it differs from an SBOM, the fields the FDA expects for AI-enabled devices, and how to generate one in CycloneDX or SPDX.
Read the guide
How CPE and PURL identifiers differ, why medical device SBOMs need both, and how to map PURL to CPE for FDA postmarket CVE monitoring under Section 524B.
Read the guide
Does the FDA prefer CycloneDX or SPDX? Compare SBOM formats for medical device cybersecurity compliance and premarket 510(k) submissions.
Read the guide
FDA SBOM requirements for medical devices: required format, the seven minimum elements, vulnerability mapping, submission deadlines, and the most-cited reviewer deficiencies.
Read the guide
How to maintain SBOMs across a fleet of cleared devices - regeneration cadence, vulnerability triage, VEX, and the postmarket cybersecurity plan that ties it together.
Read the guide
What an SBOM is, why the FDA requires one under Section 524B, SPDX vs CycloneDX, how to generate and submit one, and how it powers postmarket vulnerability management.
Read the guideWhere the SBOM belongs in a 510(k) eSTAR submission, what has to accompany it, how it ties to the vulnerability assessment, and the placement errors that trigger deficiencies.
Read the guide
Master SBOM vulnerability management for medical devices. Learn to track, triage, and mitigate software risks to meet FDA premarket and postmarket requirements.
Read the guide
Learn how VEX documents complement SBOMs for FDA medical device compliance. Expert guidance on Vulnerability Exploitability eXchange for MedTech manufacturers.
Read the guideThe FDA accepts CycloneDX and SPDX SBOMs in machine-readable form. Version floors, file types, required fields, and the format mistakes that trigger deficiencies.
Read the guideSupplier SBOM responsibility under FDA Section 524B: the manufacturer owns the device SBOM, what to require in supplier contracts, and how to document gaps reviewers will accept.
Read the guidePenetration testing, security controls, and testing taxonomy proof.
Real, recurring vulnerabilities we uncover during penetration testing on Class II/III connected medical devices.
Read the guide
Ten families of cybersecurity testing the Feb 2026 guidance expects, mapped to eSTAR v7.0 slots and recognized standards.
Read the guide
How to scope penetration testing for an FDA submission so the report holds up under reviewer scrutiny. Required attack surfaces, evidence depth, and how scope differs by pathway.
Read the guide
The 8 security control categories every cyber device must cover, and the evidence FDA expects for each one.
Read the guide
What security requirements testing means in the FDA's Feb 2026 guidance, how boundary analysis works, and why it is verification you own rather than a test a lab can run for you.
Read the guide
What medical device penetration testing is, why the FDA requires it under Section 524B, the four FDA-expected test categories, scope by device archetype, and what a credible deliverable contains.
Read the guideMonitoring, CVD, legacy devices, and FDA deficiency letter workflows.
The most common deficiencies we see in 510(k), De Novo, and PMA cybersecurity packages - and how to avoid each one.
Read the guide
Analyze real-world FDA cybersecurity deficiency letter examples. Learn how to address RTA and AI deficiency requests for 510(k) and PMA submissions.
Read the guideStep-by-step checklist for responding to FDA cybersecurity deficiency letters without losing your submission timeline.
Read the guideA field-tested playbook for responding to FDA cybersecurity deficiencies inside the 180-day clock - triage, gap analysis, fix sequence, and reviewer-ready format.
Read the guideSBOM reconstruction, vulnerability triage without source code, and end-of-support communication for devices cleared before Section 524B.
Read the guide
Master Coordinated Vulnerability Disclosure (CVD) for medical devices. Learn FDA requirements, ISO/IEC 29147 standards, and how to handle security researchers.
Read the guide
Ensure FDA compliance with our guide to postmarket cybersecurity monitoring for medical devices. Master vulnerability intake, risk assessments, and disclosure.
Read the guide
What you need in place after clearance to satisfy FDA postmarket expectations and stay ahead of vulnerabilities.
Read the guide
Stand up a Vulnerability Disclosure Program and Coordinated Vulnerability Disclosure workflow that satisfies FDA, aligns to ISO/IEC 29147 / 30111, and actually works for a small MedTech security team.
Read the guideEU MDR, AI Act, IVD, SaMD, HIPAA, and cross-framework crosswalks.
What CR34971 adds on top of ISO 14971, the AI-specific risk categories it covers, and how to integrate it with your existing risk file.
Read the guideWhat AAMI CR515:2025 covers for machine learning-enabled devices, the ML threats generic threat modeling misses, and how it interlocks with GMLP, PCCP, AIBOM, and Section 524B.
Read the guideHow Section 524B and AAMI SW96 apply to clinical analyzers, point-of-care, and connected IVD platforms, plus the pitfalls IVD teams hit.
Read the guide
How EU AI Act Article 15 obligations compare to the FDA's PCCP framework and Section 524B for AI/ML SaMD.
Read the guide
How EU MDR/IVDR cybersecurity requirements compare to FDA Section 524B and the February 2026 guidance - Annex I §17.2, MDCG 2019-16, SBOM, vulnerability handling, and postmarket obligations.
Read the guidePlain-English breakdown of FDA's 2025 draft AI guidance: what it adds beyond PCCP and GMLP, transparency labeling expectations, and what reviewers want to see.
Read the guideEach of the FDA/Health Canada/MHRA Good Machine Learning Practice principles mapped to concrete engineering, QMS, and documentation controls.
Read the guide
Overview and crosswalk of the five frameworks every MedTech innovator must satisfy after FDA clearance - shared controls, sequencing, and FAQs.
Read the guide
How the HHS HPH Cybersecurity Performance Goals map to manufacturer obligations, MDS2 disclosures, and Section 524B evidence.
Read the guideIEC 60601 is an electrical safety and EMC family, not a cybersecurity standard. What each sub-part covers, where it touches security, and the standards that actually apply.
Read the guideISO/TR 80002-2:2017 governs validation of non-device software used in the quality system. How it applies to SBOM generators, SCA scanners, threat modeling tools, and signing pipelines.
Read the guide
Master SaMD cybersecurity FDA requirements. Learn premarket submission needs, SBOM standards, and postmarket monitoring for SaMD under Section 524B.
Read the guideBook a 30-minute strategy session and we'll map the guides to your actual device, timeline and gaps.
