
Standards
How the medical device cybersecurity standards fit together
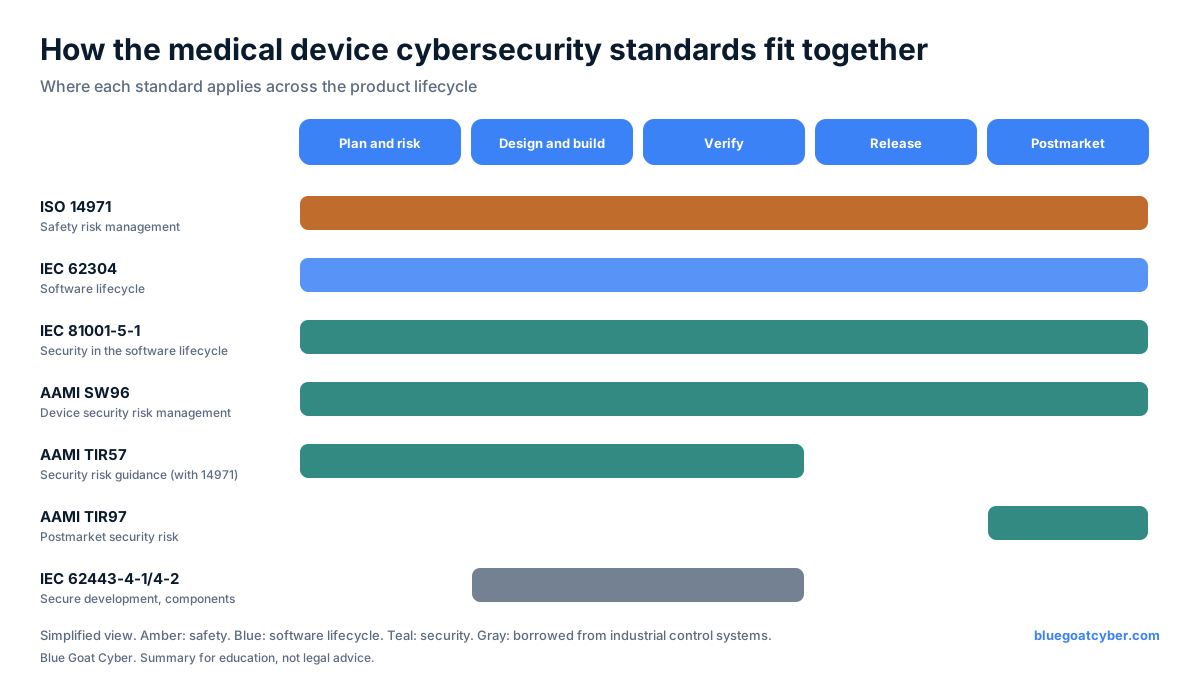
ISO 14971, IEC 62304, IEC 81001-5-1, AAMI SW96, TIR57, TIR97, and IEC 62443 mapped across the product lifecycle.
What the graphic says
The full text version, so the content is readable without the image.
Where each standard applies
A simplified view across plan and risk, design and build, verify, release, and postmarket.
- ISO 14971
- Safety risk management across the whole lifecycle.
- IEC 62304
- Software lifecycle processes across the whole lifecycle.
- IEC 81001-5-1
- Security activities in the health software lifecycle, start to finish.
- AAMI SW96
- Security risk management for device manufacturers, start to finish.
- AAMI TIR57
- Security risk guidance used with ISO 14971, mostly planning through verification.
- AAMI TIR97
- Security risk management after the device is on the market.
- IEC 62443-4-1 and 4-2
- Secure development and component requirements borrowed from industrial control systems, often used in design and verification.
Ready when you are
Get FDA cleared without the cybersecurity headaches.
30-minute strategy session. No cost, no commitment - just answers from people who've shipped 275+ devices supported.