Blue Goat CyberBlue Goat CyberSMMedical Device Cybersecurity
    Start here
    Services
    • FDA Premarket Cybersecurity Package
    • Medical Device Penetration Testing
    • Medical Device Threat Modeling
    • FDA Deficiency Response
    • FDA Postmarket Cybersecurity
    • MedTech Compliance Bundle
    See all services
    Products

    Blue Goat products

    • GoatWatch logoGoatWatchSBOM risk management for medical devices
    About
    Resources

    Learn

    • Blog
    • Podcast
    • Webinars
    • Talks & workshops
    • Glossary
    • FAQs

    Playbooks & Tools

    • Guides
    • Playbooks (PDF)
    • Infographics
    • Interactive Tools

    Signals & Proof

    • Goat FeedNew
    • News
    • Medical Device Security News
    • The Goat's Weekly
    • Case Studies
    • Proof / Receipts
    All resources, topic hubs, & collections →
    ⌘K
    Book Strategy SessionHow to prepare →
    Blue Goat Cyber

    Full-service medical device cybersecurity. We protect patients by securing connected medical devices from design through postmarket.

    275+ FDA submissions supported, zero cybersecurity rejections · Mission: 1,000 by 2028

    SDVOSB · Service-Disabled Veteran-Owned Small Business

    We sponsor 10 community projects →

    Services

    • FDA Premarket Cybersecurity Package
    • FDA Deficiency Response
    • Medical Device Threat Modeling
    • Medical Device Penetration Testing
    • FDA Postmarket Cybersecurity
    • All services →
    Services
    • FDA Premarket Cybersecurity Package
    • FDA Deficiency Response
    • Medical Device Threat Modeling
    • Medical Device Penetration Testing
    • FDA Postmarket Cybersecurity
    • All services →

    Company

    • About
    • Core values
    • Manifesto
    • Leadership
    • Why Us
    • Partners
    • Careers
    • Press
    • Press kit
    • Contact
    • Company overviewPDF
    Company
    • About
    • Core values
    • Manifesto
    • Leadership
    • Why Us
    • Partners
    • Careers
    • Press
    • Press kit
    • Contact
    • Company overviewPDF

    Resources

    • Blog
    • Guides
    • Podcast
    • Case studies
    • Monthly Pulse newsletter
    • All resources →
    Resources
    • Blog
    • Guides
    • Podcast
    • Case studies
    • Monthly Pulse newsletter
    • All resources →

    Get in touch

    • info@bluegoatcyber.com
    • 844-939-GOAT
    • Book a strategy session →
    • 1776 N Scottsdale Rd, Unit 727
      Scottsdale, AZ 85257Serving clients worldwide

    Follow

    © 2026 Blue Goat Cyber. All rights reserved.

    • Privacy
    • Terms
    • Cookies
    • Sitemap
    • Accessibility
    • CVD

    MedTech Cybersecurity · Since 2022

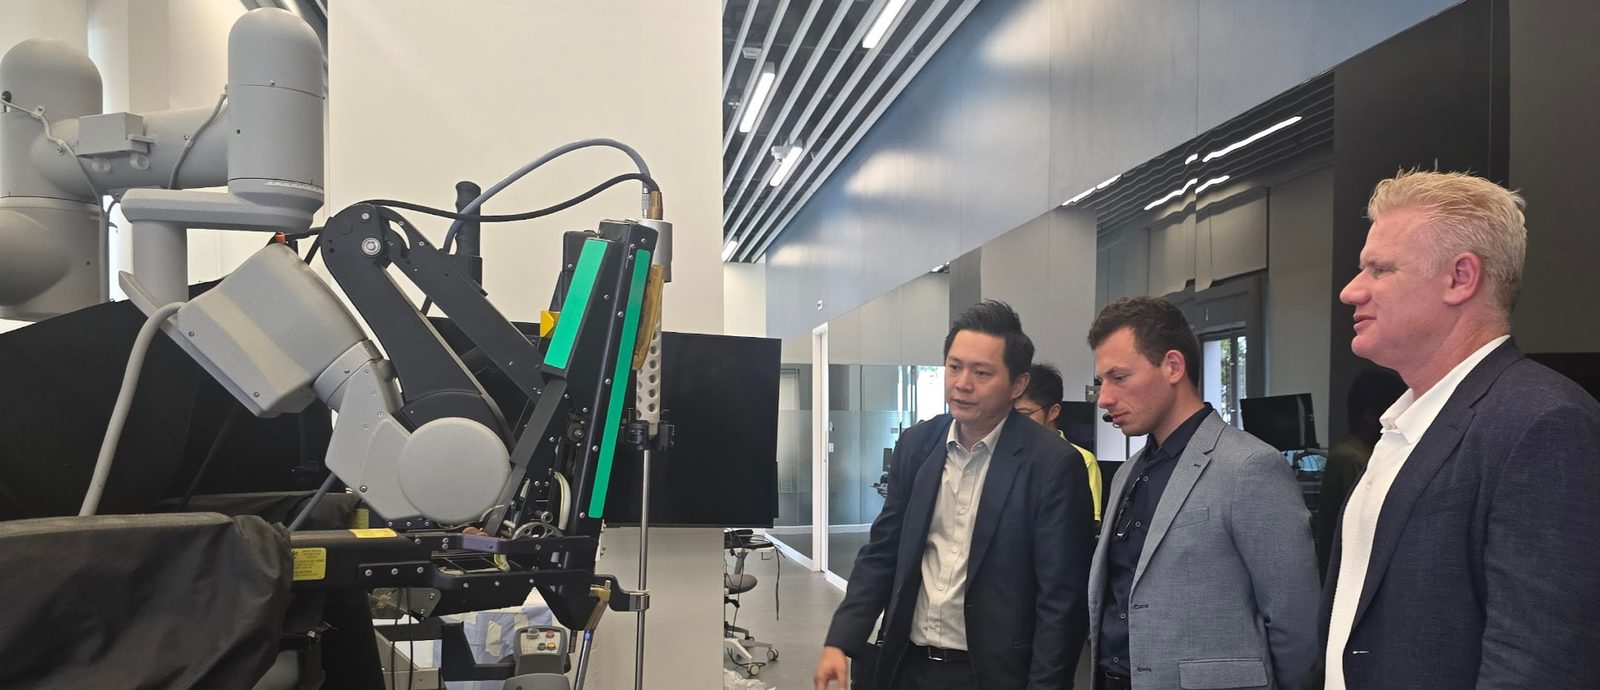
    Blue Goat Cyber team on a surgical robotics manufacturing floor in Hong Kong, reviewing a robotic arm
    Careers

    Work on the security of devices that keep people alive.

    We are a remote, high-trust, high-ownership team securing the medical devices that modern healthcare runs on.

    See 4 open rolesCareer pathscareers@bluegoatcyber.com

    Blue Goat Cyber is a medical device cybersecurity company dedicated to protecting patient lives by securing the technologies that power modern healthcare. We support medical device manufacturers as they build, test, and launch secure devices that meet FDA expectations and operate safely in the real world.

    We are a remote, high-trust, high-ownership team that values clear communication, rigorous thinking, proactive problem solving, continuous learning, and attention to critical details. We expect every team member to own their work, communicate clearly, and support the mission without ego.

    Benefits

    • Health, dental, and vision
    • 401(k)
    • Educational allowance for training and certifications
    • 10 paid holidays a year, plus paid time off and sick leave
    • Flexible scheduling
    • Fully remote in the US, paid every two weeks
    • Your own laptop, with project hardware and lab gear covered

    Open roles (4)

    Senior Regulatory Affairs Technical Writer (Medical Device Cybersecurity)

    Lead the cybersecurity documentation for 510(k), De Novo, and PMA submissions, turning complex device, regulatory, and security material into clear, submission-ready work, and raise the bar for the writers around you.

    Open
    Location
    Remote (United States), minimal travel
    Employment type
    Full-time employee
    View the full roleApply now

    Medical Device Penetration Tester

    Run deep-dive penetration tests across medical devices, firmware, mobile apps, APIs, and cloud components, then translate findings into regulator-ready evidence.

    Open
    Location
    Remote (United States), up to 40% client travel as required
    Employment type
    Full-time
    View the full roleApply now

    Senior Medical Device Penetration Tester

    Lead medical device penetration tests from scoping to debrief, mentor other testers, and run deep-dive testing across medical devices, firmware, mobile apps, APIs, and cloud components, then translate findings into regulator-ready evidence.

    Open
    Location
    Remote (United States), up to 40% client travel as required
    Employment type
    Full-time
    View the full roleApply now

    Medical Device Cybersecurity Sales Engineer

    Run discovery calls, scope medical device cybersecurity projects accurately, and write proposals that the delivery team can actually execute.

    Open
    Location
    Remote (United States), occasional client and event travel
    Employment type
    Full-time employee, 40 hours per week
    View the full roleApply now

    Not hiring right now

    These roles are paused. Read what the work involves, and write to careers@bluegoatcyber.com if you want to hear when one reopens.

    Project Manager, Medical Device Cybersecurity

    Remote (United States), with overlap to 9 to 5 ET

    Closed

    Business Development Manager, Medical Device Cybersecurity

    Remote (United States), with regular medtech event travel

    Closed

    Content and Social Media Manager

    Remote (United States), occasional event travel

    Closed

    Us, actually working

    Real photos from conferences and team meetups, not stock images of people pointing at monitors.

    Christian Espinosa and colleagues standing beside a surgical robotic arm on a manufacturing floor during a factory tour in Hong Kong
    Surgical robotics floor tour, Hong KongSeeing how a device is actually built before we decide how to attack it.
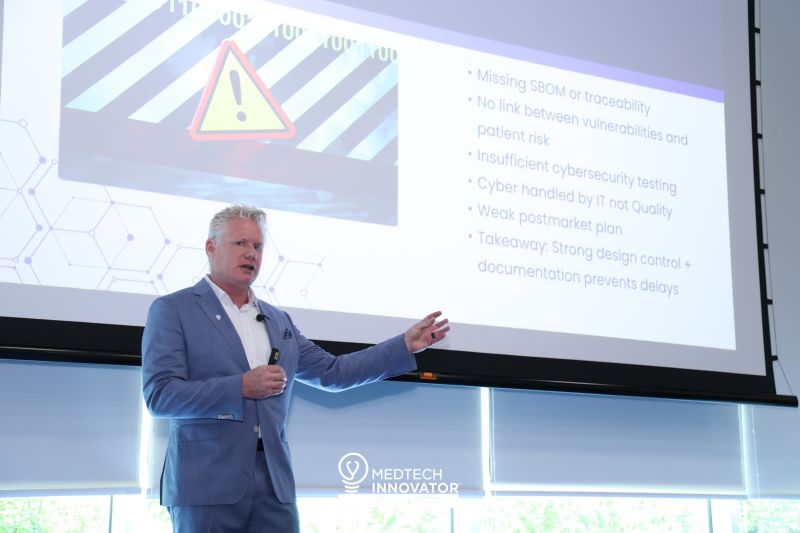
    Christian Espinosa teaching beside a projected slide on medical device cybersecurity misconceptions at MedTech Innovator APAC 2025 in Singapore
    Teaching session, MedTech Innovator APAC 2025Walking device teams through the cybersecurity mistakes that stall FDA review.
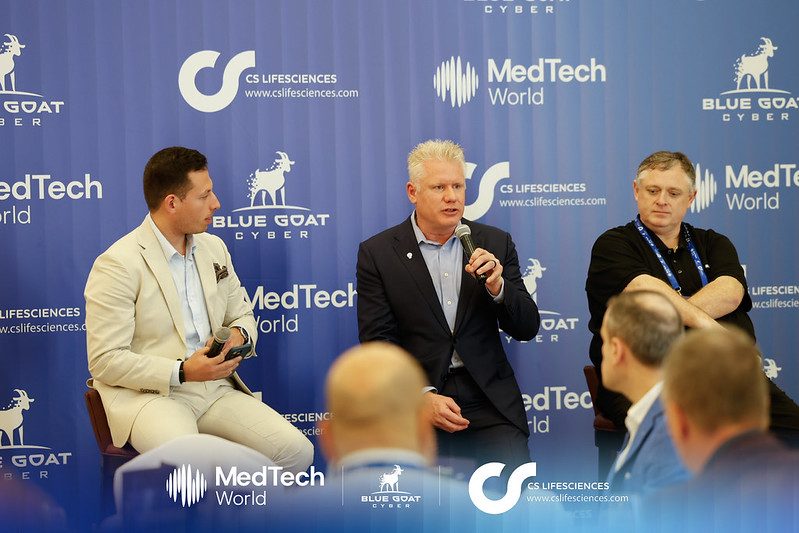
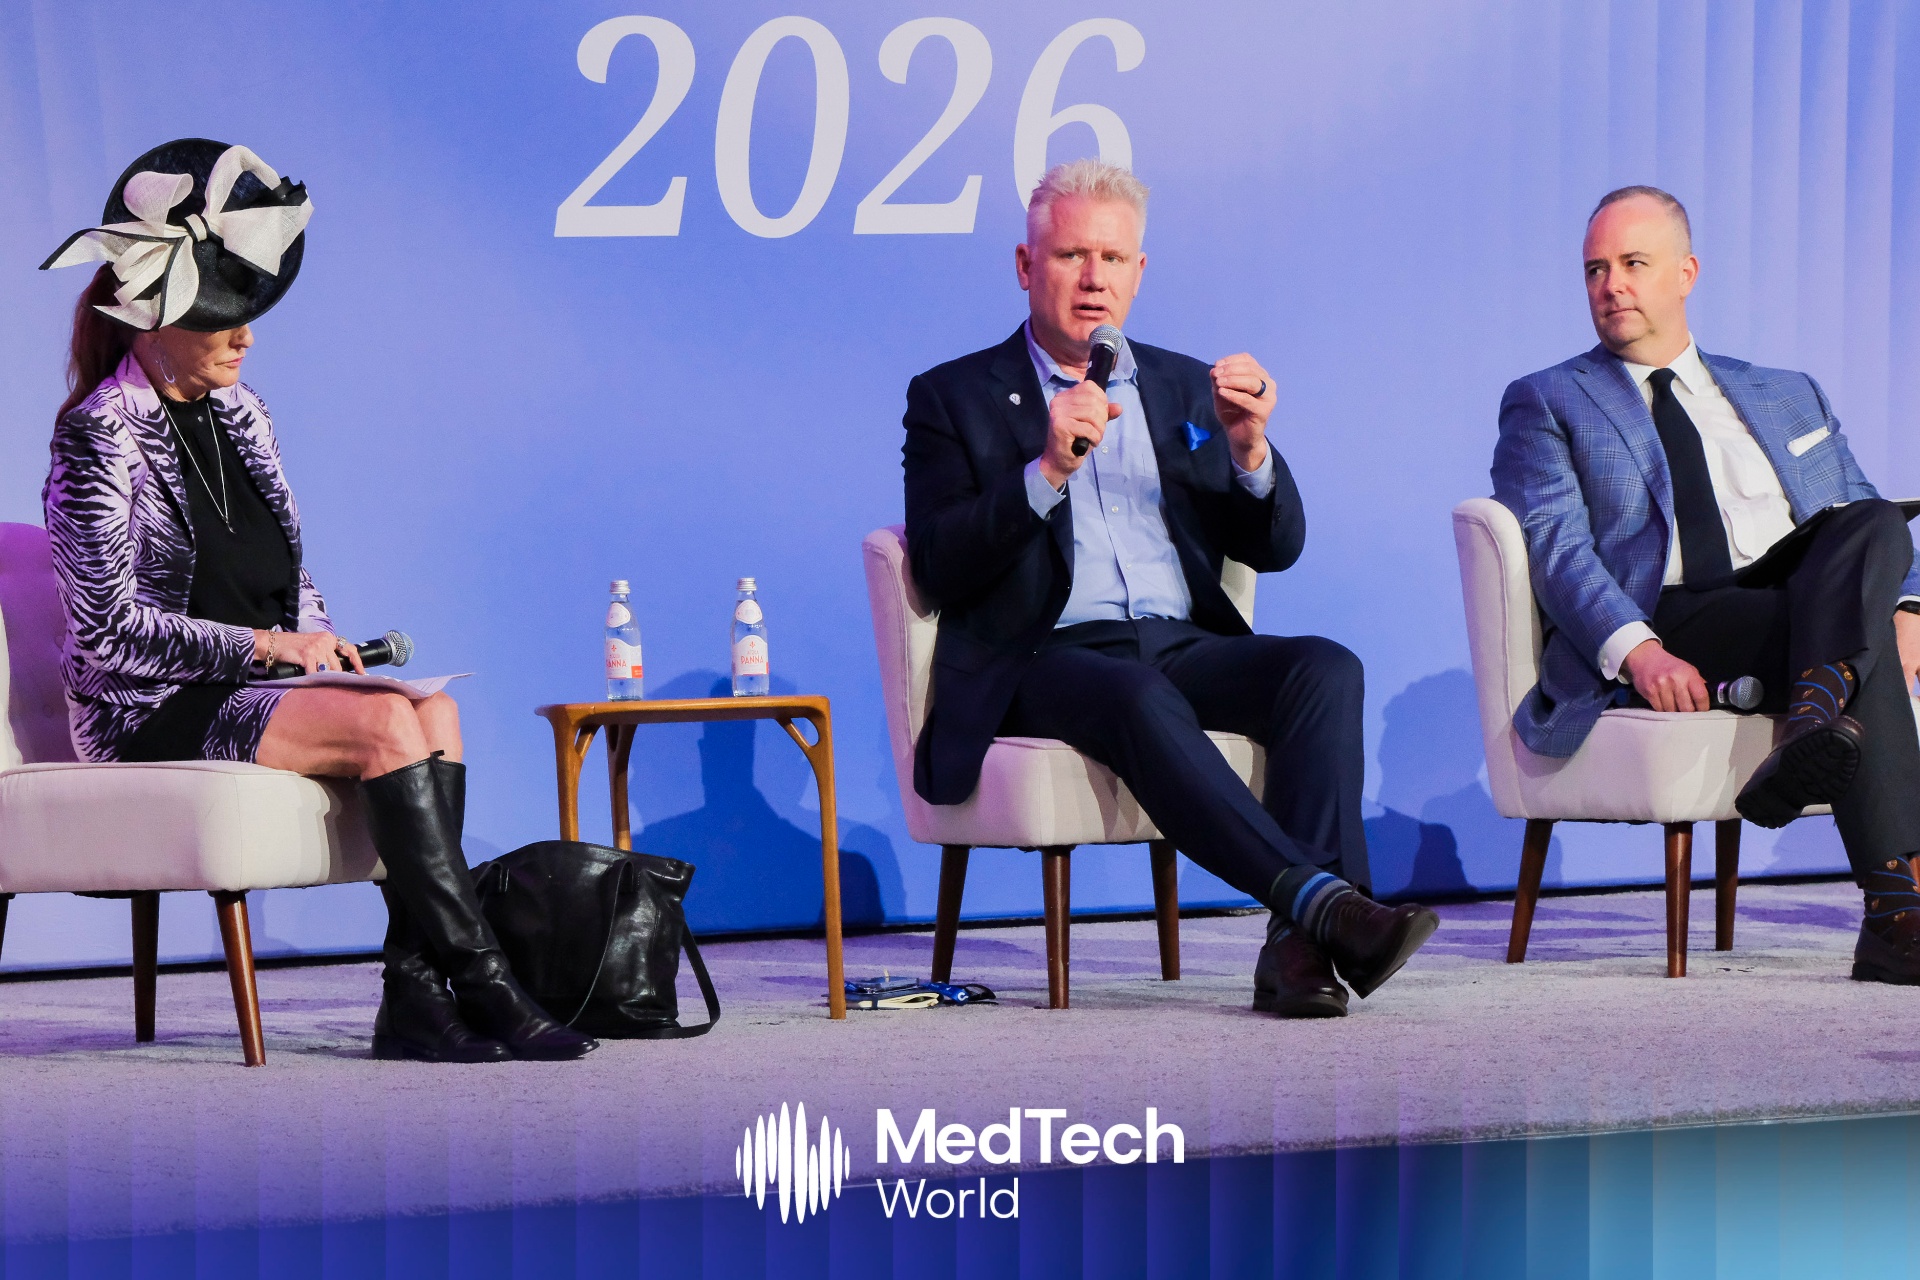
    Christian Espinosa speaking into a microphone on a three person medical device cybersecurity panel at MedTech World Dubai 2026
    Cybersecurity panel, MedTech World Dubai 2026Answering manufacturer questions on stage, not from a slide deck.
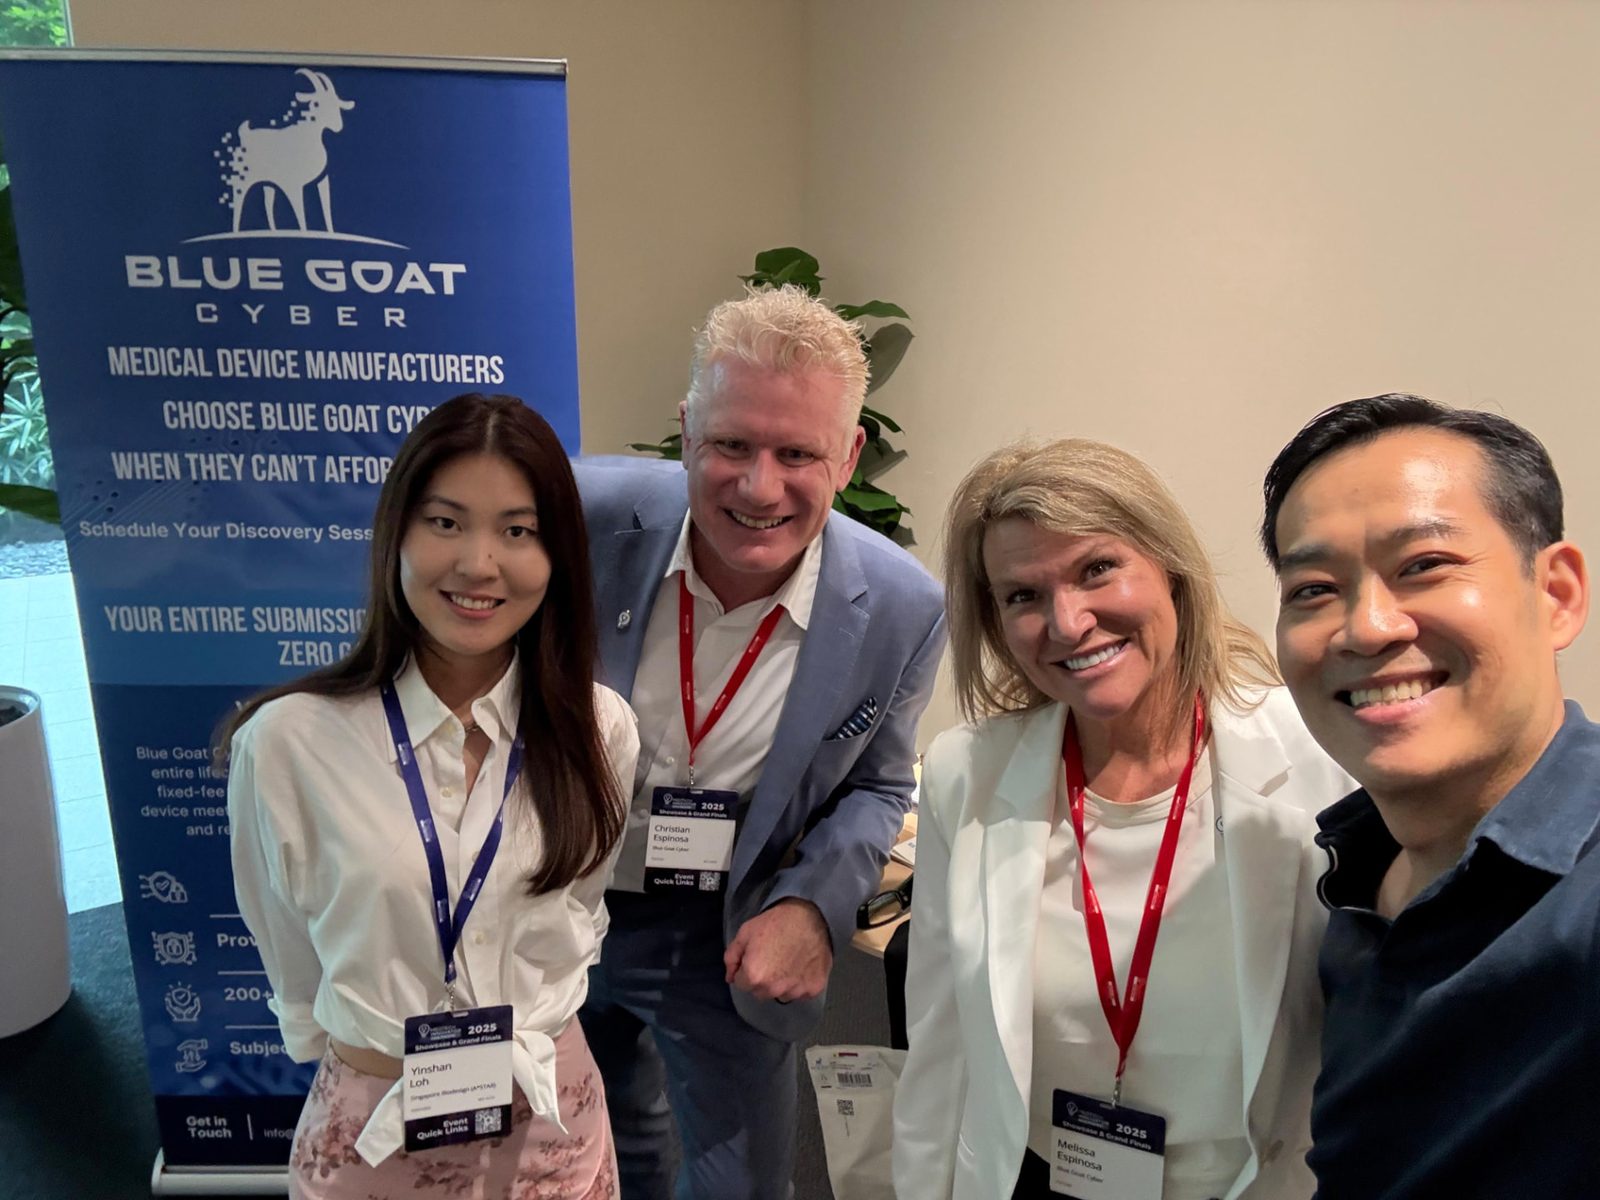
    Christian and Melissa Espinosa standing with partners in front of a Blue Goat Cyber banner at the MedTech Innovator APAC showcase in Singapore
    Partner showcase, SingaporeMeeting the accelerator teams we mentor across the Asia Pacific region.
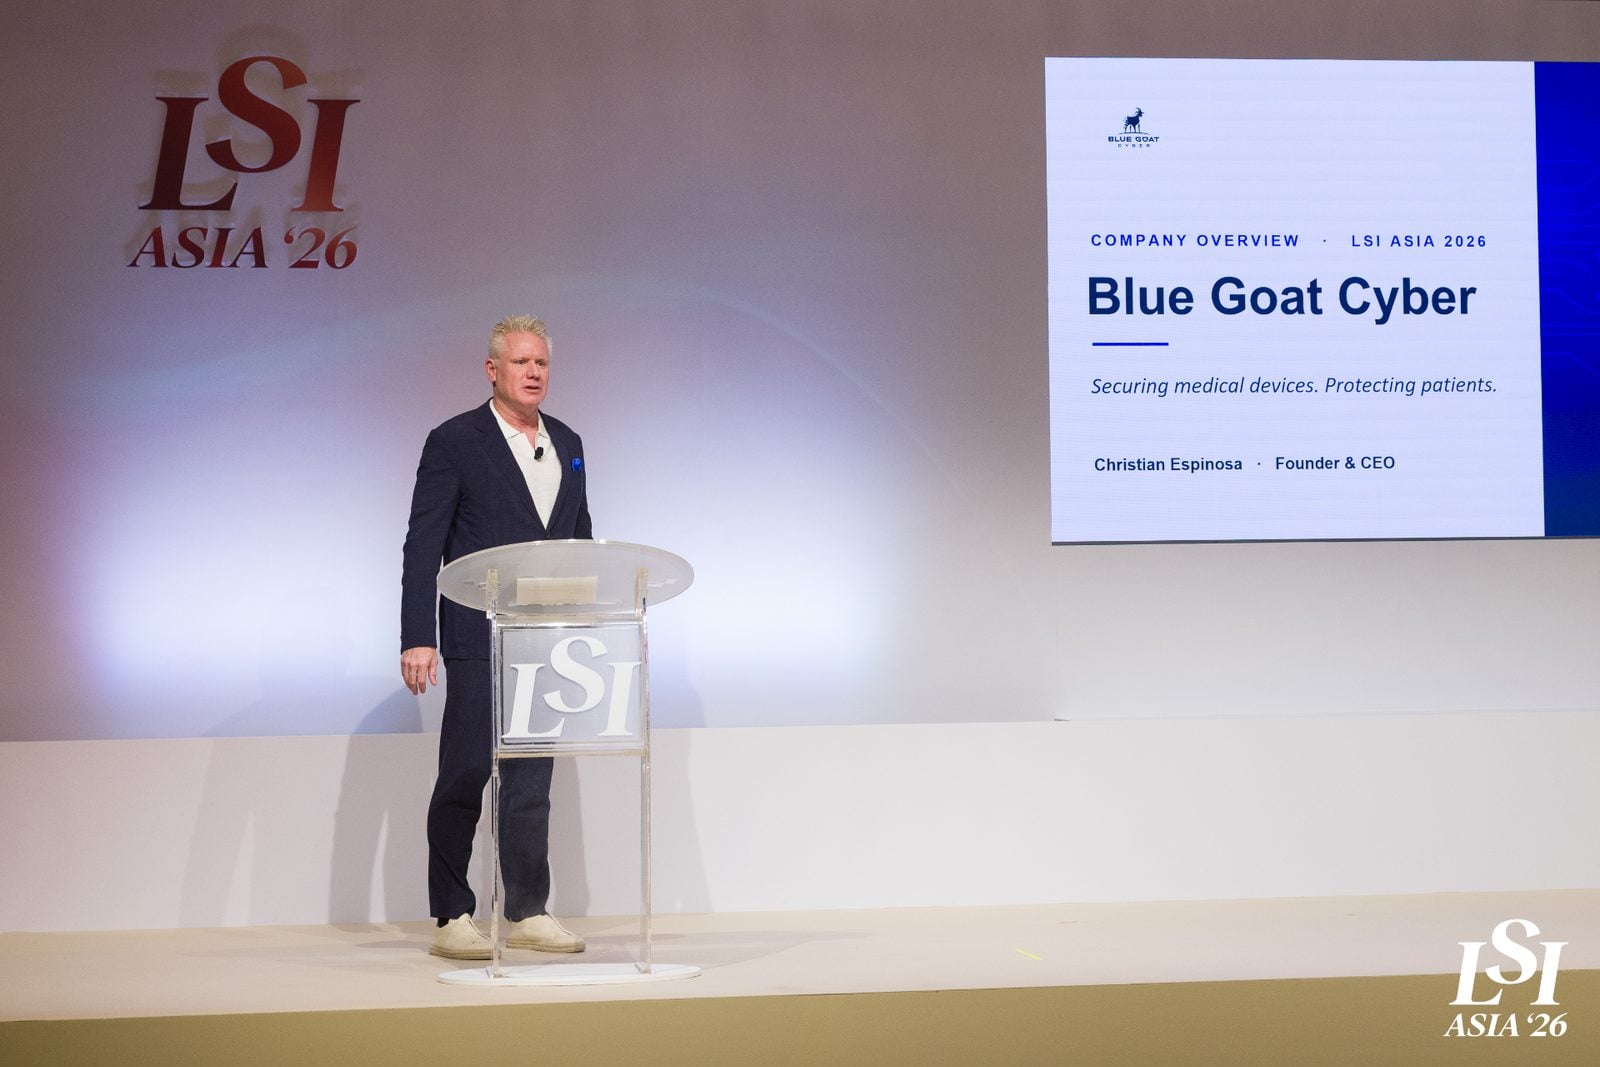
    Christian Espinosa presenting the Blue Goat Cyber company overview on stage at LSI Asia 2026 in Singapore, with a slide reading Securing medical devices, protecting patients
    Main stage, LSI Asia 2026Explaining to investors and founders why device security starts at design.
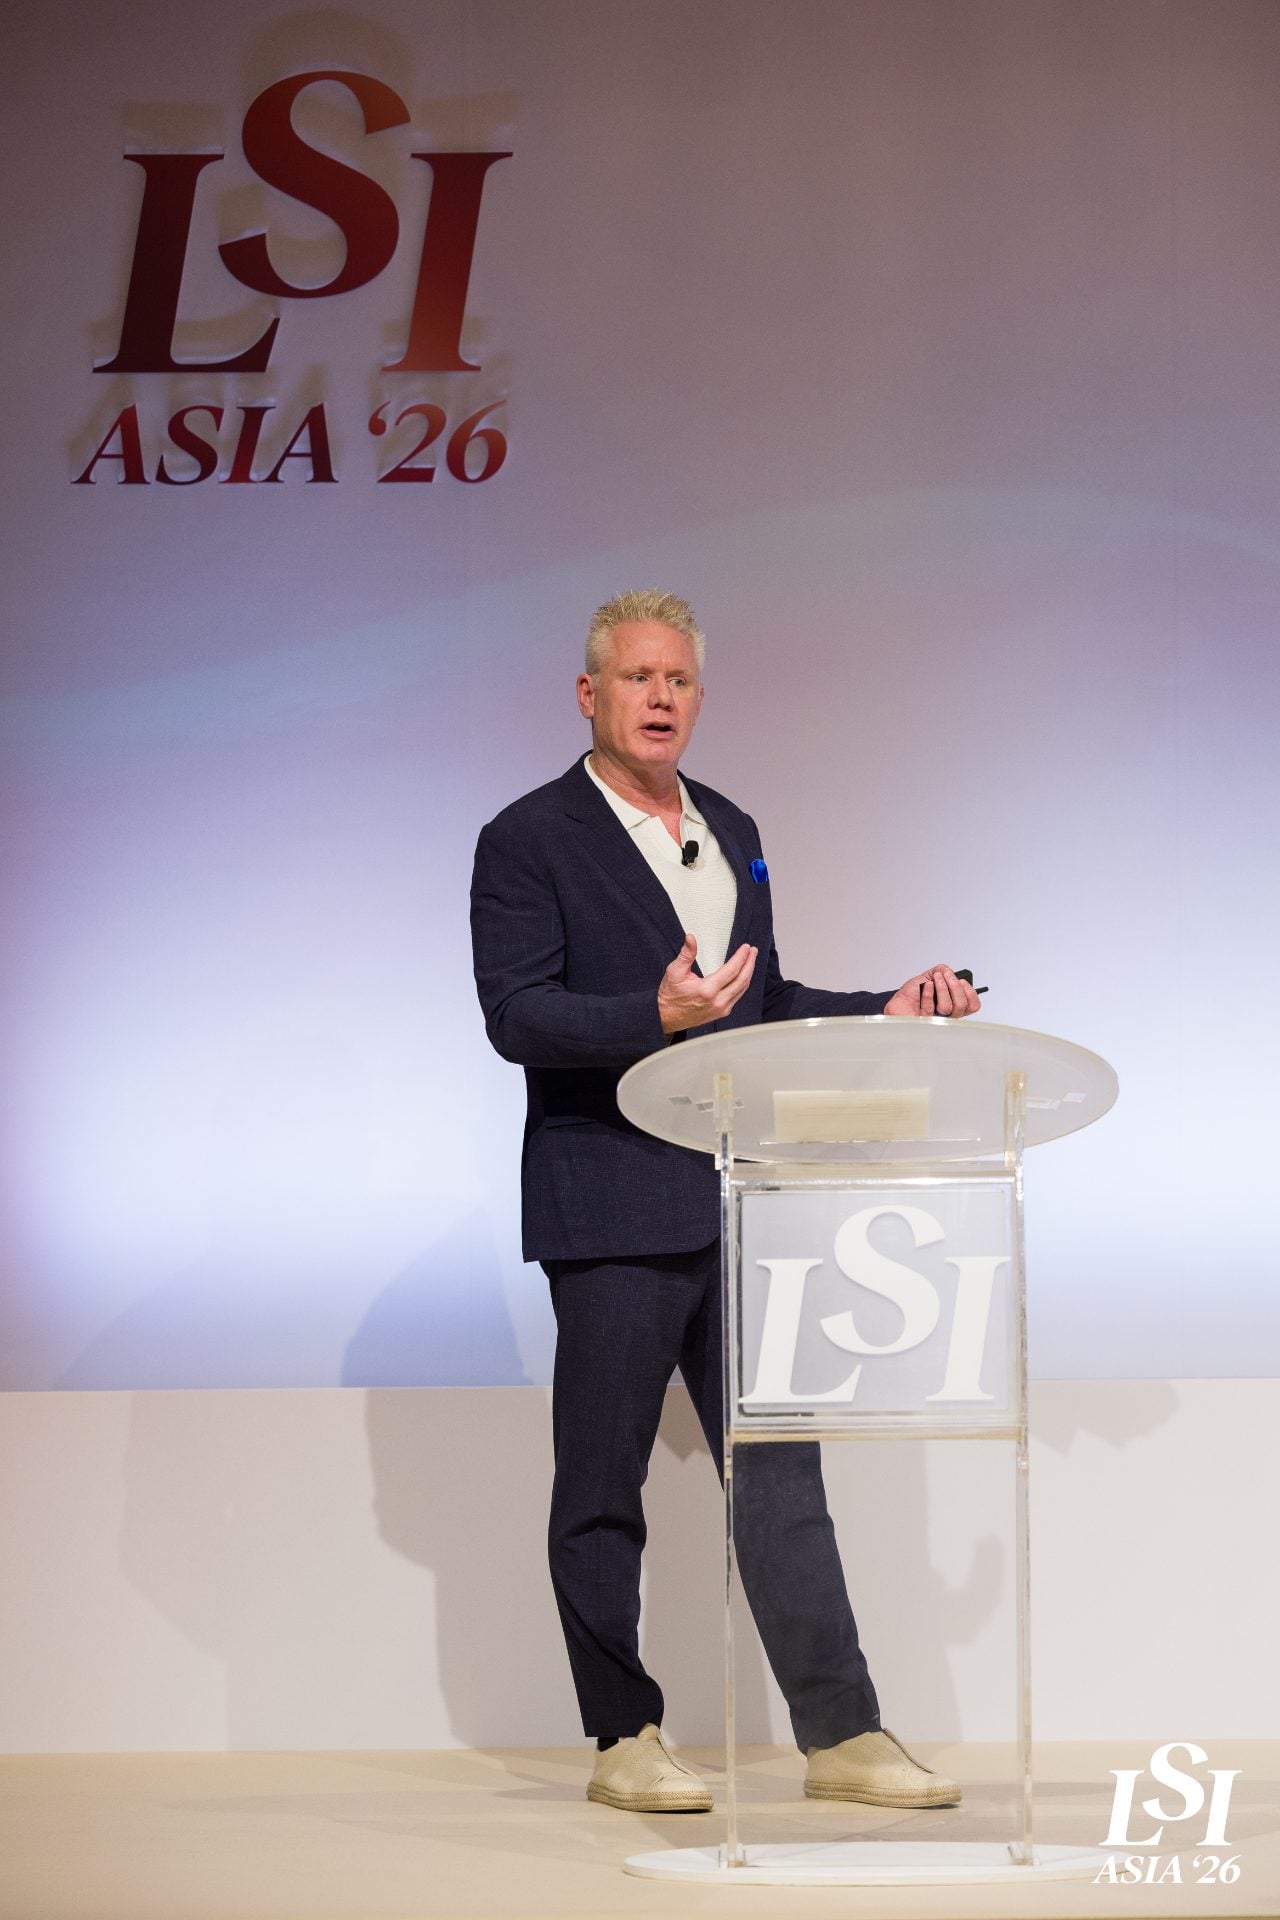
    Christian Espinosa speaking at a clear podium under the LSI Asia 2026 logo during a conference session in Singapore
    Conference session, LSI Asia 2026Fielding questions from device teams preparing their first submission.
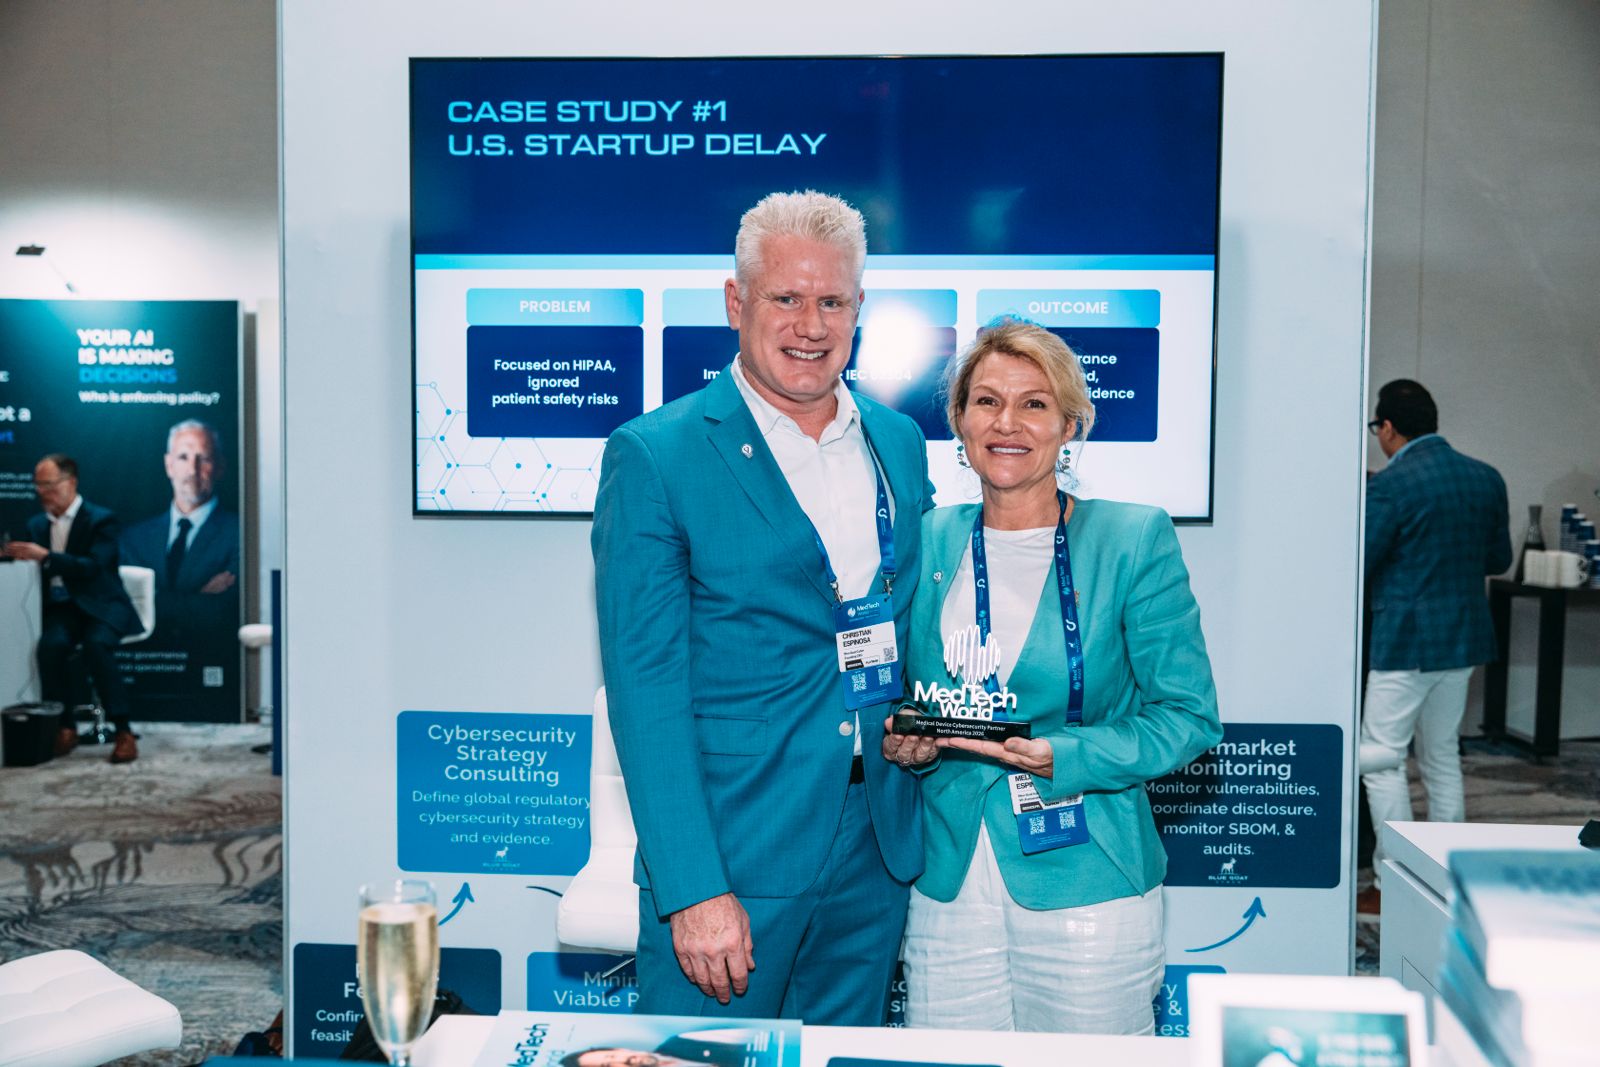
    Christian and Melissa Espinosa accepting the MedTech World North America 2026 Cybersecurity Partner of the Year award
    Partner of the Year, MedTech World North America 2026Recognition for the work the whole team puts into every submission.
    Blue Goat Cyber team members at the company booth during a medtech conference
    Team booth, medtech conferenceTalking with device makers face to face about what is blocking their submission.
    Christian Espinosa with CTO Myles Kellerman at the MedTech World gala
    MedTech World galaLeadership you will actually work alongside, not just read about.
    Christian Espinosa on the main stage panel at MedTech World 2026
    Main stage panel, MedTech World 2026Sharing what we learn in the lab with the wider medtech industry.

    What the pen testing work looks like

    No lab glamour shots, just an honest picture of the job.

    1. 01

      Understand

      Device architecture · clinical use · threats

      See the whole system

    2. 02

      Investigate

      Attack paths · interfaces · security controls

      Find the weaknesses

    3. 03

      Communicate

      Findings · evidence · manufacturer decisions

      Make the work usable

    4. 04

      Keep learning

      Training · certifications · shared experience

      Grow your expertise

    Responsibilities depend on your role. This is the work, not a hiring timeline.
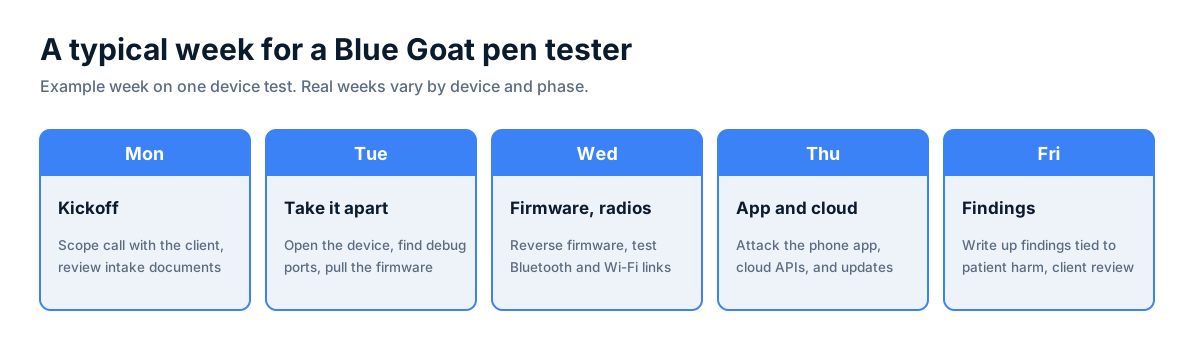
    A typical week for a Blue Goat pen tester: Monday kickoff, Tuesday take the device apart, Wednesday firmware and radios, Thursday app and cloud, Friday findings
    Example week on one device test. Monday: scope call and intake review. Tuesday: open the device, find debug ports, and pull the firmware. Wednesday: reverse the firmware and test Bluetooth and Wi-Fi. Thursday: attack the phone app, cloud APIs, and updates. Friday: write findings tied to patient harm and review them with the client.
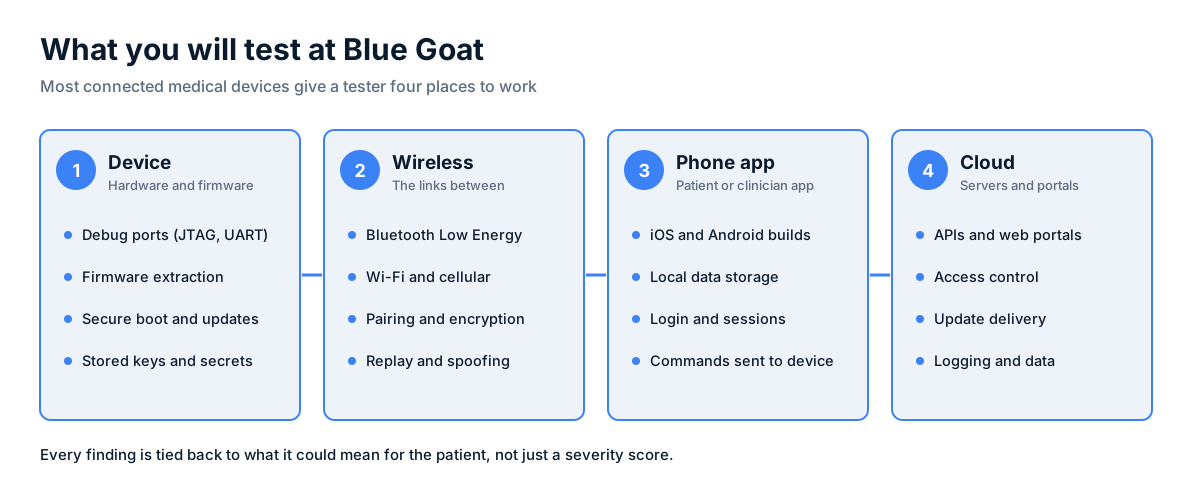
    Four test areas: the device, wireless links, the phone app, and the cloud
    Device: debug ports, firmware, secure boot, updates, and stored keys. Wireless: Bluetooth Low Energy, Wi-Fi, cellular, pairing, encryption, replay, and spoofing. Phone app: iOS and Android builds, local storage, login, sessions, and device commands. Cloud: APIs, portals, access control, update delivery, and logging.

    Meet the team

    A small team, all named and reachable. No layers between you and the people making decisions.

    Headshot of Christian Espinosa, Founder & CEO at Blue Goat Cyber

    Christian Espinosa

    Founder & CEO

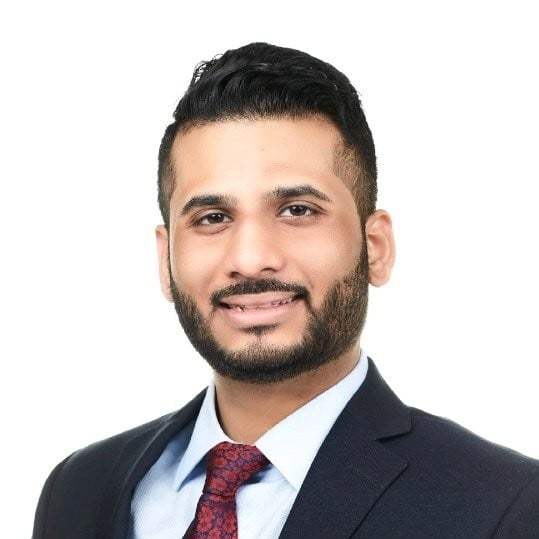
    Professional headshot of Jordan John, VP of Regulatory Affairs & Compliance at Blue Goat Cyber - a smiling man with short dark hair and a beard, wearing a navy suit, light blue shirt, and red patterned tie, photographed against a plain white background.

    Jordan John

    VP, Regulatory Affairs & Compliance

    Headshot of Melissa Espinosa, VP, Strategic Partnerships at Blue Goat Cyber

    Melissa Espinosa

    VP, Strategic Partnerships

    Headshot of Kristy Kennedy, VP, Sales at Blue Goat Cyber

    Kristy Kennedy

    VP, Sales

    Professional headshot of Michelle Hughes, Director of Operations at Blue Goat Cyber - a smiling Black woman with short curly hair, wearing coral-pink top and a blue-and-white striped blazer, photographed indoors against a soft neutral background.

    Michelle Hughes

    Director of Operations

    Professional headshot of Sarah Beach, Senior Project Manager at Blue Goat Cyber - a white woman with long straight auburn hair, wearing a white blouse, photographed against a plain light-gray background with a neutral expression.

    Sarah Beach

    Senior Project Manager

    Read the full team bios
    Why we exist

    Why we exist

    The same purpose, vision, and mission we hold clients to. It is the reason these roles exist.

    Purpose

    Medical device security is patient safety.

    Why we exist: so the devices people depend on can't be turned against them.

    Vision

    Connected medical devices that are secure by design and resilient for their entire service life.

    The world we are working toward, with no end date.

    Mission

    By 2028, help medical device teams get 1,000 devices through FDA review with zero cybersecurity-driven rejections, and teach the industry to start cybersecurity early.

    What we do daily, with a deadline: secure the devices in front of us, and through books, stages, podcasts, webinars, and mentoring, help every other team understand what cybersecurity means for their device before it costs them.

    Read the manifesto →

    Get to know the company

    Read what we believe and who you would be working with before you apply.

    Who we are

    How the firm started, how it grew, and the medtech-only focus that shapes every engagement.

    About Blue Goat Cyber

    Our core values

    The five values we hire and promote against, with what each one looks like in practice and what it is not.

    Read the values

    The manifesto

    What we believe, what we promise clients, and the line we will not cross for a deadline.

    Read the manifesto

    Who you would work with

    The leadership team you would report to and learn from, and the people behind the research we publish.

    Meet the team

    How we work

    Five things that describe the job before you read a single description.

    Patient safety is the point

    Every threat model, test, and document we produce ends up in front of a regulator and, eventually, in a device attached to a person. That is the standard the work is held to.

    Own it end to end

    You hold your deliverables, your dates, and your client relationships. Nobody chases you for status, and you flag risk before it becomes an escalation.

    Depth over volume

    Tooling helps, but the majority of every engagement is manual work. We hire people who go past scanner output and can explain exactly why a finding matters.

    Write like it will be read by a reviewer

    Clear, structured, technically accurate writing is a core skill in every role here, not an afterthought handed to someone else.

    Remote, high trust, no ego

    We are distributed across the United States. We assume good faith, share what we learn, and judge work by outcomes rather than hours visible online.

    These are the working standards. What we believe and why the company exists is set out in our core values and our manifesto. Read both before you apply. If you disagree with them, this is not the right company for you, and that is a useful thing to find out now.

    This is not an IT security job

    Most cybersecurity jobs are enterprise IT jobs. If you are coming from that world, the work here is a different discipline, and the differences are the whole job.

    Enterprise IT securityHere
    What is at stakeData breach, downtime, fines, reputation.A patient. Harm is physical: a wrong dose, a missed alarm, a therapy that stops. That is the risk we are analyzing, not the record.
    Who reads your workAn internal security team, an auditor, a compliance checklist.An FDA reviewer, a quality system, and a manufacturer's design history file. Your writing becomes part of a regulatory submission.
    What good looks likeClose the finding, patch the system, pass the audit.Show the rationale. A finding with no clinical impact analysis and no traceability to a requirement and a test is not finished work here.
    The targetManaged endpoints, cloud accounts, corporate networks.Embedded firmware, radios, medical protocols, and devices that cannot be rebooted mid-procedure or patched on Patch Tuesday.
    Risk framingCVSS score, asset criticality, business impact.ISO 14971 risk management, patient harm severity, and essential performance. A high CVSS with no patient impact may be the lower priority.
    The deliverableA scan report or a ticket queue.A written argument a regulator can follow, defended months later when the deficiency letter arrives.

    Coming from enterprise IT is fine, and several people here did. What does not transfer is the assumption that finding the vulnerability is the job. Here it is the start of the job.

    This is probably not for you if

    We would rather you rule yourself out now than six weeks into a client engagement. These are the things people most often discover too late.

    You want to be told exactly what to do

    There is no queue of tickets and nobody checks your progress daily. You are given an objective, a client, and a date, and you are expected to work out the rest and ask when you are stuck.

    You want to run scanners and move on

    Tooling is a starting point here, not the deliverable. If manual analysis, reading firmware, and explaining why a finding matters clinically is not the part you enjoy, this will be a grind.

    You do not want to write

    Every role here produces written work that a regulator or a client executive reads. If writing feels like the tax you pay for the real job, you will not enjoy this one.

    You round up

    We say what we know, what we tested, and what we did not. Overstating findings, coverage, or a completion date is the fastest way to not work here, and it is the one thing we do not coach through.

    You need an office and a team around you

    We are fully remote and deliberately small. Plenty of people do their best work this way and plenty do not, and the second group is not a worse engineer, just a bad match for us.

    You wait to be told

    Gaps and problems that sit until someone else raises them are the pattern we screen hardest for. If you notice something that is not clearly your job, we expect you to say so.

    Your commitments slip quietly

    Every commitment here has a date, and you say so before it slips, not after. People who find that uncomfortable struggle with client work.

    You want a title track more than the work

    Growth here comes from what you can own, not from a ladder. If your next step has to be a title by a fixed date, a larger company will serve you better.

    What hiring looks like

    No take-home projects and no ten-round gauntlet. Here is the whole process.

    1. 1

      Apply

      Reviewed within 5 business days

      Fill out the application form on this site with your resume, links to your work, and a short note about why the role fits. We read every one.

    2. 2

      Intro conversation

      About 30 minutes

      A 30-minute call about your background, what you want to work on, and how we operate. Bring questions.

    3. 3

      Working conversation

      60 to 90 minutes

      A deeper session with the team you would join. Expect to talk through real problems: a device you would threat model, a document you would restructure, a project you would rescue.

    4. 4

      Career walkthrough

      60 to 90 minutes

      We go through your jobs in order, oldest first, with the same questions each time: what you were hired to do, what went well, what went badly, who you reported to, and why you left. It is the longest conversation in the process and the most useful one. We will also ask you to arrange short calls with your former managers, and we will ask them the same questions we asked you.

    5. 5

      Final conversation and references

      About 45 minutes

      A call with leadership on fit, expectations, and compensation, plus the reference calls you arranged.

    6. 6

      Offer

      Usually within a week of the final call

      We move quickly once we decide. Start dates are flexible for the right person.

    What excellence looks like here

    People ask what we mean by A players. We mean people who already work like this on several of these standards, and want to grow into the rest. This is the same bar our current team holds itself to.

    The one that comes first: patient safety

    Raise a safety, quality or compliance concern even when it is inconvenient, unpopular, or costs a deadline or a client conversation. For a tester that might be a finding in a device. For finance it might be a number that does not reconcile. If you are not sure it is significant enough to mention, mention it anyway. This one is not a spectrum. It is a habit, and we hire people who already have it.

    1. Standard 1

      Role competence

      Performs at a level others on the team learn from. Catches what others miss.

    2. Standard 2

      Client and team trust

      Clients and teammates seek this person out. Communication reduces risk instead of creating it.

    3. Standard 3

      Ownership

      Closes gaps that are not clearly anyone's job. Outcomes improve because this person was involved.

    4. Standard 4

      Judgment under ambiguity

      Makes the right call with incomplete information. Others check their own judgment against this person's.

    5. Standard 5

      Growth and coachability

      Seeks feedback before it is offered. Adapts ahead of the role's changing needs.

    6. Standard 6

      Rigor and attention to detail

      Catches the gap in their own work before anyone else has to: the missing field, the number that does not match, the step skipped under pressure.

    7. Standard 7

      Proactive risk anticipation

      Surfaces risks before being asked to look, early enough that the fix is still cheap.

    8. Standard 8

      Innovation and forward thinking

      Finds a way to make things better for the client without compromising what they are responsible for protecting, rather than trading one for the other.

    Nobody arrives at the top of all eight. Once you are here, we share the full growth guide, with a concrete first and next move for each standard. It carries no score and is not used to rank anyone.

    How we decide

    We read applications in a specific order, and it is not the order most companies use. Knowing it up front is worth more to you than any interview tip.

    What moves you forward

    • Your written answers, first

      The scenarios and the work sample are read before anything else, and they carry the most weight. We are looking for how you reason when the question is underspecified, not whether you reached our answer.

    • The work sample over the credentials

      A clear paragraph of technical writing, a defensible test scope, or a well-argued risk rationale tells us more than a certification list. We have hired people with no certifications and passed on people with all of them.

    • Whether you read the posting

      One question in the form is answered directly by the job page. Missing it is not disqualifying on its own, but paired with a low knowledge score it tells us the application went out in bulk.

    • Honesty about what you do not know

      Every role here touches regulation, engineering and clinical risk, and nobody arrives strong in all three. Saying which one you would need to learn reads as credible. Claiming all three does not.

    What carries less weight than you think

    • Where you worked

      A recognizable employer does not move you forward, and an unknown one does not hold you back. We care what you personally produced there.

    • A polished resume

      We open it, and it rarely changes the decision. It confirms dates and scope; it does not demonstrate thinking.

    • Using AI to write

      We use it daily ourselves and we ask you to disclose it, not avoid it. What we notice is an answer with no specifics in it, which is what unedited AI output reads like.

    If you are not moving forward, you will hear from us rather than hearing nothing. A real person reads every application, and no one is screened out automatically.

    Where these roles lead

    Every open role sits on a track with somewhere to go. Here is what growth looks like on each one, and what we pay for along the way.

    Regulatory and documentation

    You start by assembling submission evidence against a checklist and end up owning the regulatory strategy for a whole device program.

    1. Regulatory Affairs Technical Writer

      Year 1

      Assemble threat models, SBOMs, and test evidence into submission-ready packages. Learn Section 524B, the premarket cybersecurity guidance, and what a reviewer actually reads first.

    2. Senior Regulatory Analyst

      Years 2 to 3

      Own full submissions end to end, draft deficiency responses, and run the internal review that catches problems before the FDA does.

    3. Regulatory Lead

      Year 4 and beyond

      Set strategy for client programs, advise on pathway and predicate decisions, and mentor analysts. Authoring guides and speaking at industry events is part of the job at this level.

    What we invest in

    • RAC certification support
    • AAMI and standards committee participation
    • Published guides under your own byline
    Start as Senior Regulatory Affairs Technical Writer

    Security testing

    You start on scoped engagements and grow into the tester we route the hardest devices to, shaping how we test a whole device class.

    1. First engagements

      Early work

      Run scoped tests across device firmware, wireless interfaces, mobile apps, and cloud backends. Write findings that survive an FDA reviewer reading them.

    2. Steady engagement flow

      As trust builds

      Lead multi-surface engagements, define test plans from the threat model, and take the hardware and radio work that nobody else on the bench can take.

    3. Lead tester on a device class

      Long term

      Become the person we route a whole device class to, shape our testing methodology, review other testers' reports, and act as the technical voice with clients and reviewers.

    What we invest in

    • Hardware and RF lab equipment when a project needs it
    • Named credit on published research and conference talks
    • Certification and training support through the educational allowance
    Start as Medical Device Penetration Tester

    Senior security testing

    You join as an engagement lead, keep doing hands-on testing, and grow through technical leadership and mentoring.

    1. Lead engagements

      First engagements

      Set authorized scope, lead device and connected-system testing, and review findings and patient impact before client delivery.

    2. Develop the testing team

      As the role develops

      Mentor other testers, improve test plans and evidence quality, and take ownership of complex device classes.

    3. Shape testing methodology

      Long term

      Lead improvements in hardware, wireless, application, and cloud testing, and help the team apply them consistently across authorized engagements.

    What we invest in

    • Project-specific hardware and RF testing equipment
    • Technical mentoring and methodology ownership
    • Certification and training support through the educational allowance
    Start as Senior Medical Device Penetration Tester

    Delivery and operations

    You start by keeping engagements on schedule and grow into running how the whole delivery organization works.

    1. Project Manager

      Year 1

      Run concurrent client engagements, keep scope and schedule honest, and be the single point of contact clients trust.

    2. Senior Project Manager

      Years 2 to 3

      Own the largest and most complex programs, improve the delivery playbook, and onboard new project managers.

    3. Delivery or Operations Lead

      Year 4 and beyond

      Own capacity planning, delivery quality, and the systems the team runs on. This track reports into the Director of Operations and grows toward it.

    What we invest in

    • PMP or equivalent certification support
    • Direct client relationship ownership
    • Say in how the delivery process is designed
    Start as Project Manager, Medical Device Cybersecurity

    Growth and events

    You start by owning conversations and our event presence, and grow into owning how the firm goes to market.

    1. Business Development Manager

      Year 1

      Build pipeline with device manufacturers, own the event calendar, and turn conference presence into booked meetings and signed work.

    2. Senior Business Development Manager

      Years 2 to 3

      Own the largest accounts and partner relationships, shape sponsorship and speaking strategy, and mentor the next hire on the team.

    3. Growth Lead

      Year 4 and beyond

      Own the go-to-market plan, the event budget, and how marketing, sales engineering, and delivery work together.

    What we invest in

    • Event and sponsorship budget ownership
    • Speaking slots and industry visibility
    • Incentive tied to what you actually build
    Start as Business Development Manager

    Sales engineering

    You start by scoping engagements accurately and grow into owning how we define, price, and explain the work.

    1. Sales Engineer

      Year 1

      Run discovery, scope engagements, and write proposals that hold up at delivery. Learn our methodology deeply enough to defend it on a call.

    2. Senior Sales Engineer

      Years 2 to 3

      Own the hardest scopes, handle enterprise security questionnaires and RFPs, and tighten the scoping model with delivered-versus-scoped data.

    3. Solutions Lead

      Year 4 and beyond

      Own how services are packaged and priced, shape new offerings with the CTO, and represent our methodology publicly.

    What we invest in

    • Technical certification support in your track
    • Time with delivery to keep your hands in the work
    • A say in which services we build next
    Start as Medical Device Cybersecurity Sales Engineer

    Marketing

    You start by owning our channels and grow into owning how the market hears about us at all.

    1. Social Media Manager

      Year 1

      Own the calendar, grow LinkedIn and YouTube, and turn the team's technical work into content the industry actually reads.

    2. Content and Brand Manager

      Years 2 to 3

      Own the editorial plan across social, the blog, video, and the podcast, and run event and launch campaigns end to end.

    3. Marketing Lead

      Year 4 and beyond

      Own demand generation, brand, and the budget behind them, working alongside business development and sales engineering.

    What we invest in

    • Budget ownership for campaigns and paid social
    • Conference access and on-site coverage
    • A say in what the company publishes next
    Start as Content and Social Media Manager

    See the work before you apply

    Most of what we do is public. Read it, listen to it, and decide whether it is the work you want.

    The MedDevice Cyber Podcast

    Our founder interviews device makers, regulators, and clinicians every week. It is the fastest way to hear how we think.

    Listen to episodes

    Published guides and research

    Dozens of long-form guides on FDA premarket cybersecurity, threat modeling, SBOM, and testing. This is the depth the work runs at.

    Read the guides

    Where you will find us

    We speak and exhibit at medtech events including the LSI conferences in the United States and APAC.

    See our events

    How we deliver

    Our service pages describe exactly what clients receive. The roles here support that delivery directly.

    Explore services

    Recognized for this work

    Industry awards for medical device cybersecurity. You would be joining the team that earned them.

    • Medical Device Cybersecurity Partner of the Year - 2026

      MedTech World North America 2026 Awards (in collaboration with CS Lifesciences)

    • Medical Device Cybersecurity Solution of the Year - 2026

      Medical Tech Outlook (cover story)

    • MedTech Service Provider Excellence Award of the Year - 2025

      MedTech World Malta 2025 Awards Gala (sponsored by the Malta Medicines Authority)

    • Medical Device Cybersecurity Services Company of the Year - 2025

      Healthcare Business Review

    See all awards

    Careers FAQ

    The questions candidates ask most. There are fuller answers on applying, the interview timeline, pay and benefits, and what the work is really like.

    Where can I work from?
    All of our roles are remote within the United States. We are not able to sponsor visas or hire outside the US at this time. The Project Manager role asks for overlap with 9 to 5 Eastern; the other roles are flexible as long as you make team and client meetings.
    Is there travel?
    It depends on the role. The Penetration Tester role can reach up to 40 percent travel for onsite device testing. The Business Development Manager role travels regularly to medtech events. The Sales Engineer and Social Media Manager roles travel occasionally for client meetings and events. The Regulatory Affairs Technical Writer and Project Manager roles are minimal travel.
    Are these full-time roles?
    Yes. Every open role is a full-time position with benefits including health, dental, vision, a 401(k), and an educational allowance, paid every two weeks.
    Do I need medical device experience?
    Not always. We care most about depth in your own discipline plus the ability to learn the regulatory context quickly. For the Regulatory Affairs Technical Writer role we ask for medical device industry experience or education in regulatory affairs or cybersecurity.
    What does compensation look like?
    Competitive and commensurate with experience, paid every two weeks. We discuss specific numbers in the first conversation rather than posting a wide range, and we do not lowball people we want to hire.
    Read the full careers FAQ

    How to apply

    Use the application form. Attach your resume, add any links to your work, and tell us in a few honest paragraphs why the role fits. Do not see a role that matches? Send an open application and tell us what you do best. We keep applications on file and open roles as client demand grows.

    Start an applicationOr email careers@bluegoatcyber.com
    Not looking for a role?

    Need help with a device submission instead?

    Book a 30-minute strategy session with our team.

    Book strategy sessionExplore services