Before you invest in or acquire a company with a cyber device, find out whether its FDA cybersecurity package is ready, or whether it carries hidden delay and cost.
Short answer
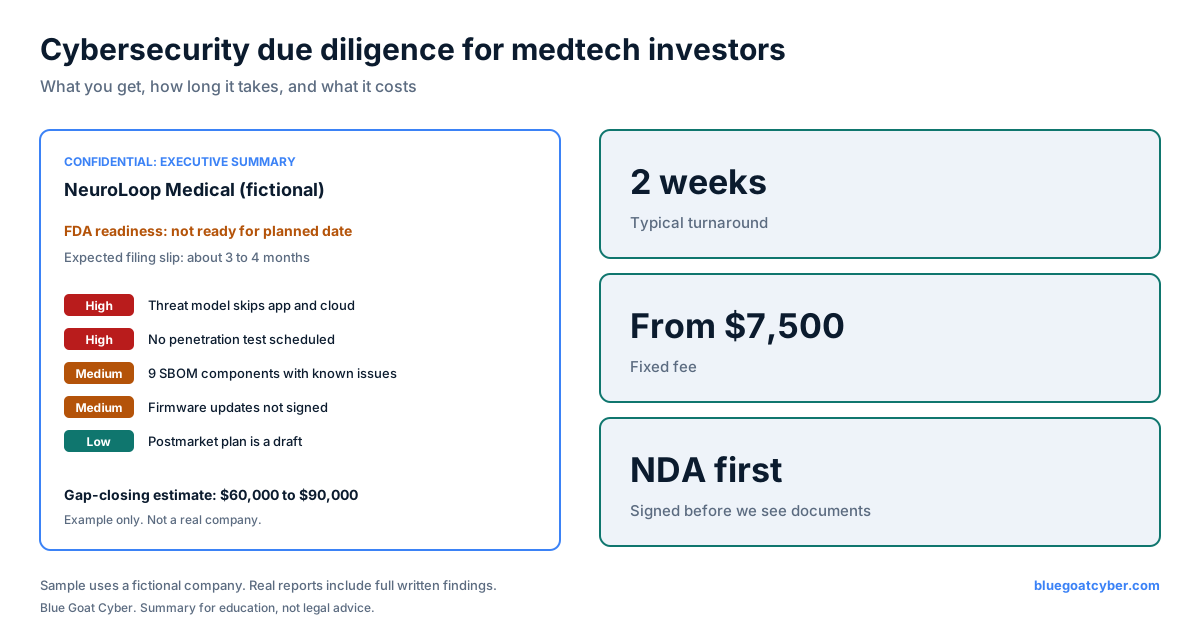
Investor cyber risk in a medical device deal comes down to one question: will the target's cybersecurity evidence satisfy the FDA on the planned timeline? Cybersecurity due diligence for medical devices reviews the threat model, SBOM, security testing and postmarket plan, then tells you what is missing and what it will cost. Blue Goat Cyber does this as a confidential, fixed-fee assessment, starting at $7,500 with results typically in about 2 weeks.
Price
From $7,500, fixed fee after scoping
Turnaround
Typically about 2 weeks
Confidentiality
We sign an NDA before seeing documents
Why it matters to the deal
Section 524B requires cybersecurity evidence in premarket submissions for cyber devices. If it is thin, the FDA can refuse to accept the file or send deficiency questions, and clearance moves out. Founders often underestimate this work, so the timeline in the pitch deck may not include it. Read Section 524B explained for the legal background.
Red flags to look for
No threat model, or one written after the design was locked
No SBOM, or an SBOM nobody has checked for known vulnerabilities
Penetration testing planned for the month before filing
No plan for finding and fixing vulnerabilities after launch
Cybersecurity owned by nobody, or by a contractor who has moved on
A prior FDA deficiency letter with open cybersecurity questions
Questions to ask management
Is the device a cyber device under Section 524B, and does the team know it?
Which of the 18 FDA cybersecurity deliverables exist today, and which are drafts?
Who did the security testing, and were they independent of the developers?
How are third-party software components tracked and patched?
What happens when a researcher reports a vulnerability after launch?
Is the cybersecurity budget and schedule in the filing plan you were shown?
The startups guide shows what a well-run early-stage company should have in place.
What our fixed-fee assessment includes
Review of the target's threat model, risk assessment, SBOM, test reports and postmarket plan
Gap check against Section 524B and the FDA's February 2026 premarket cybersecurity guidance
Written findings: what is missing, what is weak, and what it means for filing timeline
An estimate of the work needed to close the gaps
A call with your deal team to walk through the findings
What is cybersecurity due diligence for medical devices?
It is a review of a target company's cybersecurity evidence before you invest or acquire. For a cyber device, the FDA expects a threat model, risk assessment, SBOM, security testing and a postmarket vulnerability plan. Diligence checks whether those exist, whether they hold up, and what it will cost to fix what is missing.
Why does investor cyber risk matter for a medical device deal?
A weak cybersecurity package can stop the FDA from accepting a submission or lead to deficiency questions that push clearance back by months. That delay hits revenue plans and runway. After launch, an unpatched vulnerability can lead to field actions and reputational damage.
How much does it cost and how long does it take?
Assessments start at $7,500. We scope the review on a short call, then quote a fixed fee. Results typically arrive in about 2 weeks from receiving the target's documents, and we can discuss faster timing for tight deal deadlines.
Is the review confidential?
Yes. We sign your NDA, or ours, before we see any target documents, and the review and findings stay confidential to you and your deal team.
Which devices need this review?
Any device with software that can connect to a network, the internet, a phone or another device is likely a cyber device under Section 524B, whatever its FDA class. Those are the deals where cybersecurity gaps can delay clearance.
Can you help the company close the gaps after the deal?
Yes. Many portfolio companies use us to build the full FDA cybersecurity package after close. The diligence findings become the starting plan.
Request a diligence assessment
Tell us about the target and your deal timeline. We reply within one business day to scope a fixed-fee review.