
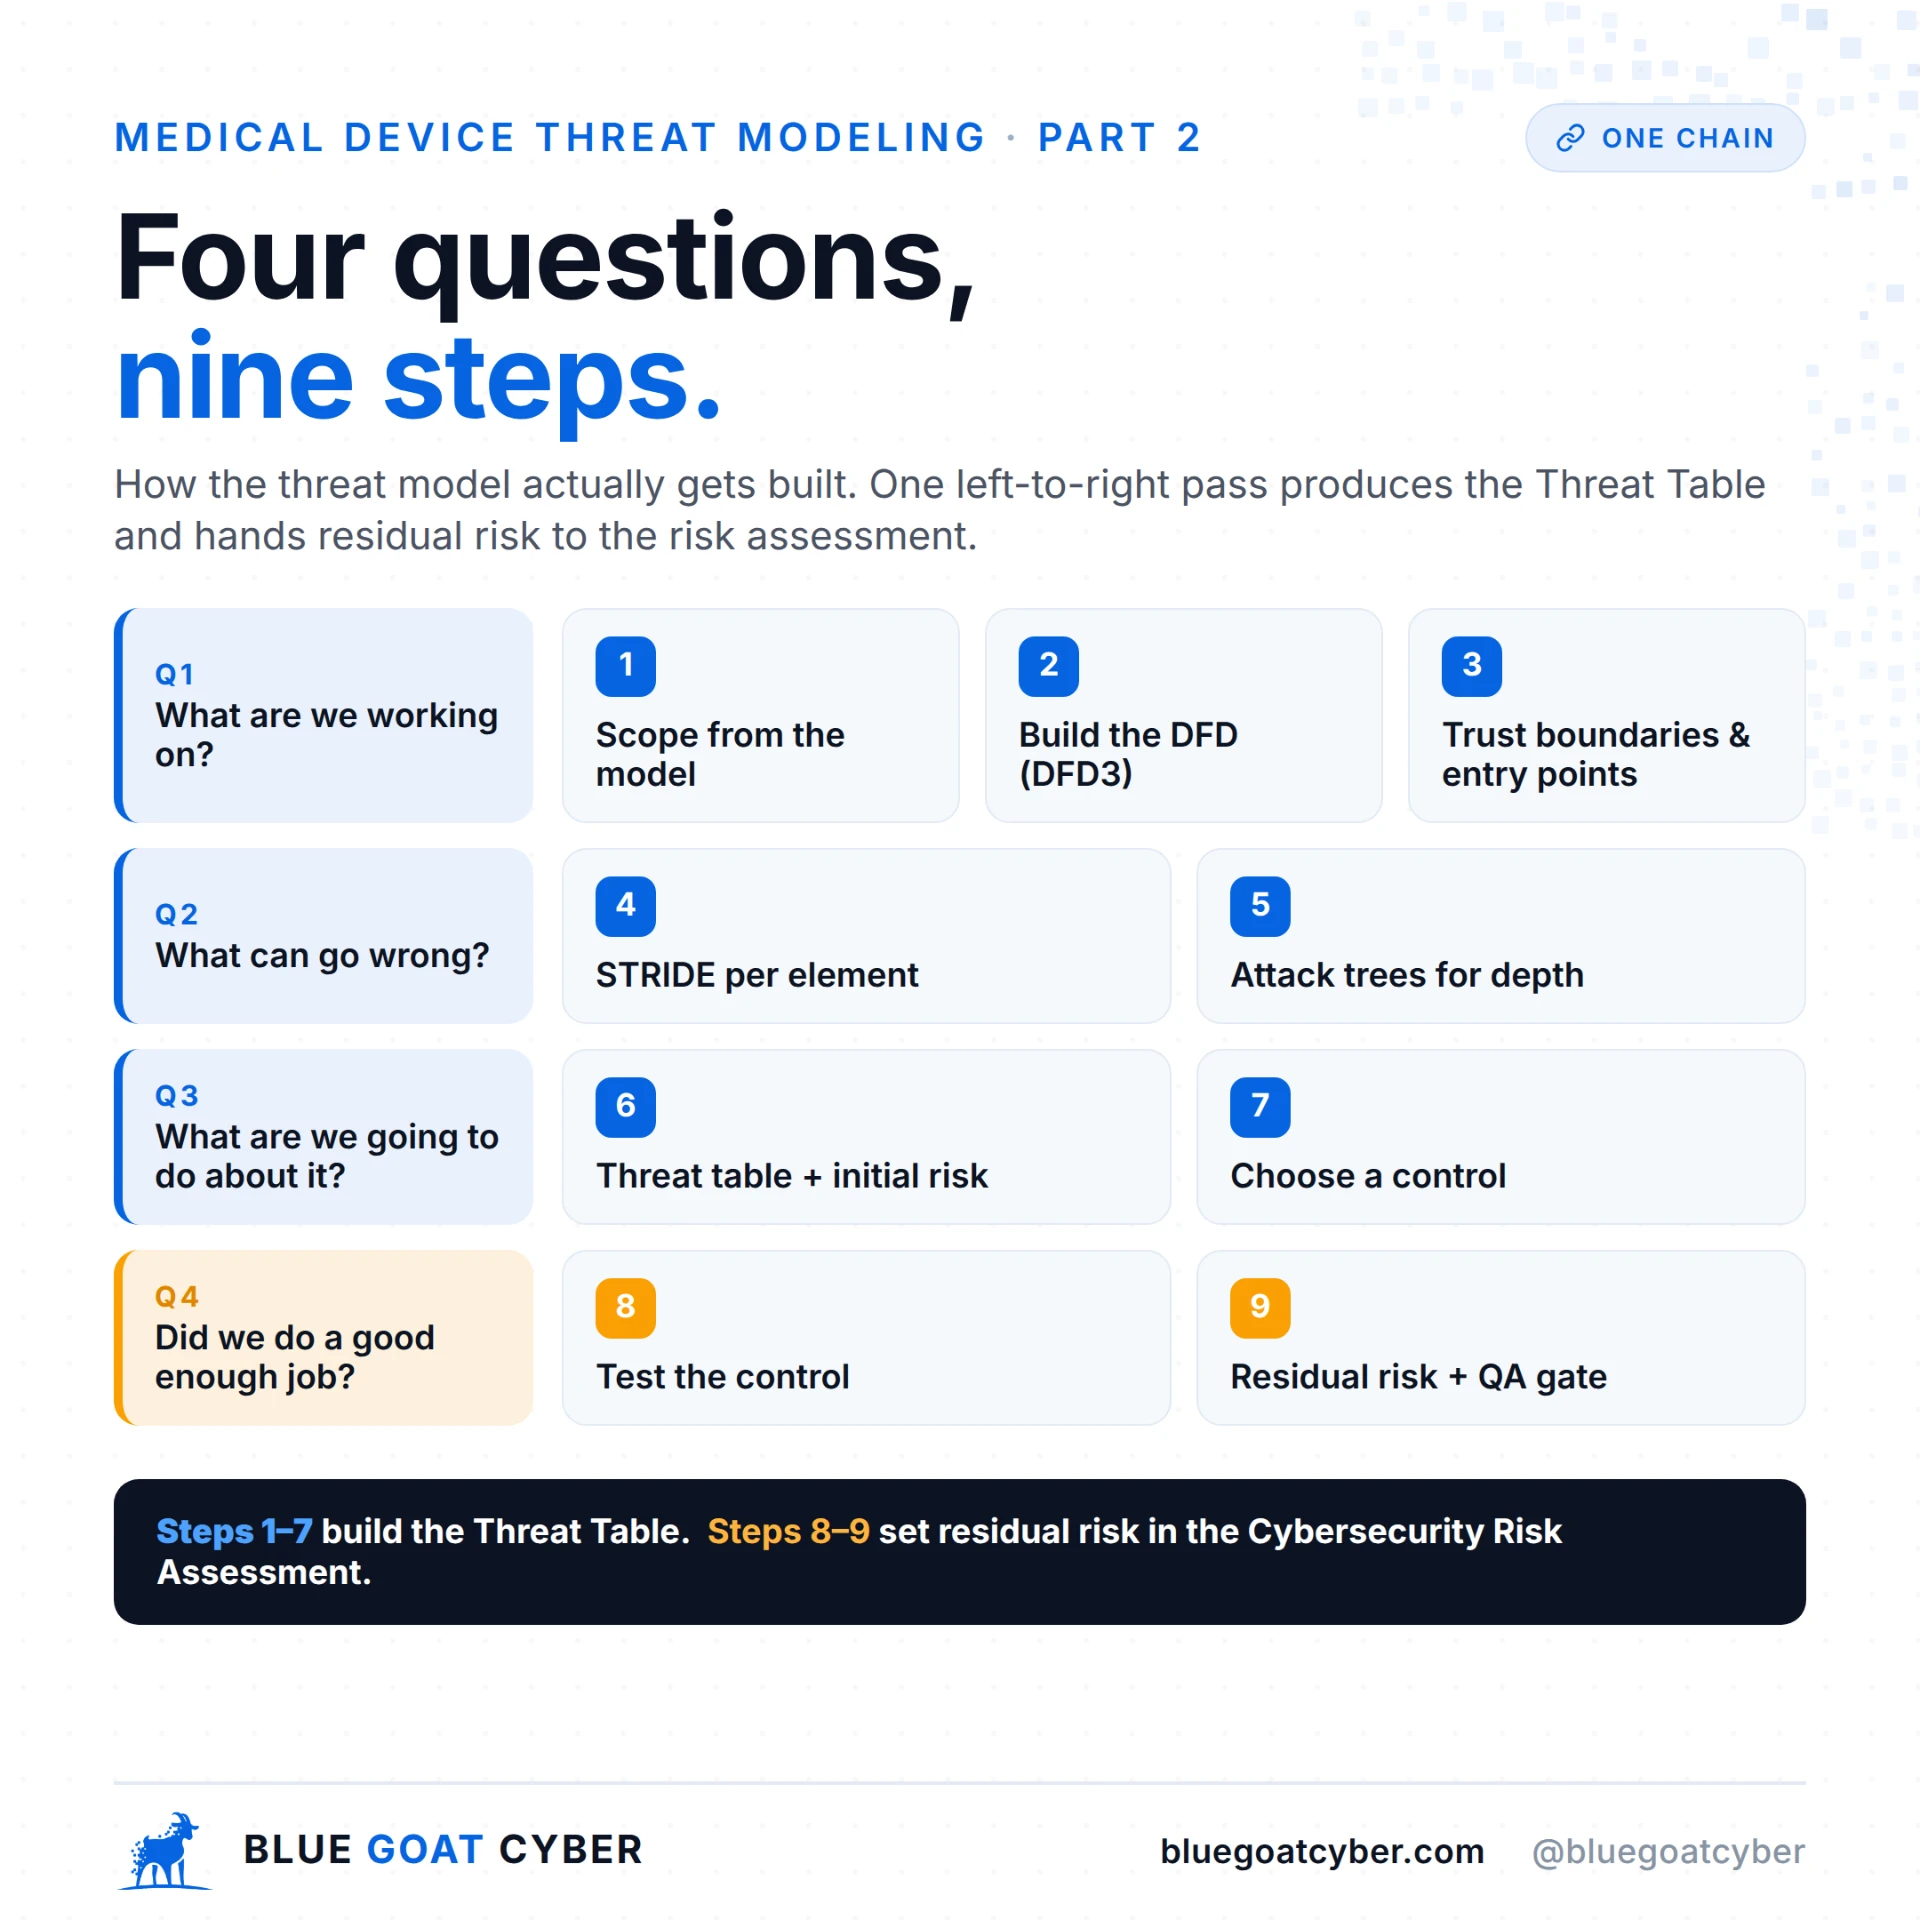
Threat Modeling · Part 1
Underneath it all, four questions
The four questions that structure a medical device threat model for FDA premarket submissions, and what each one has to produce.
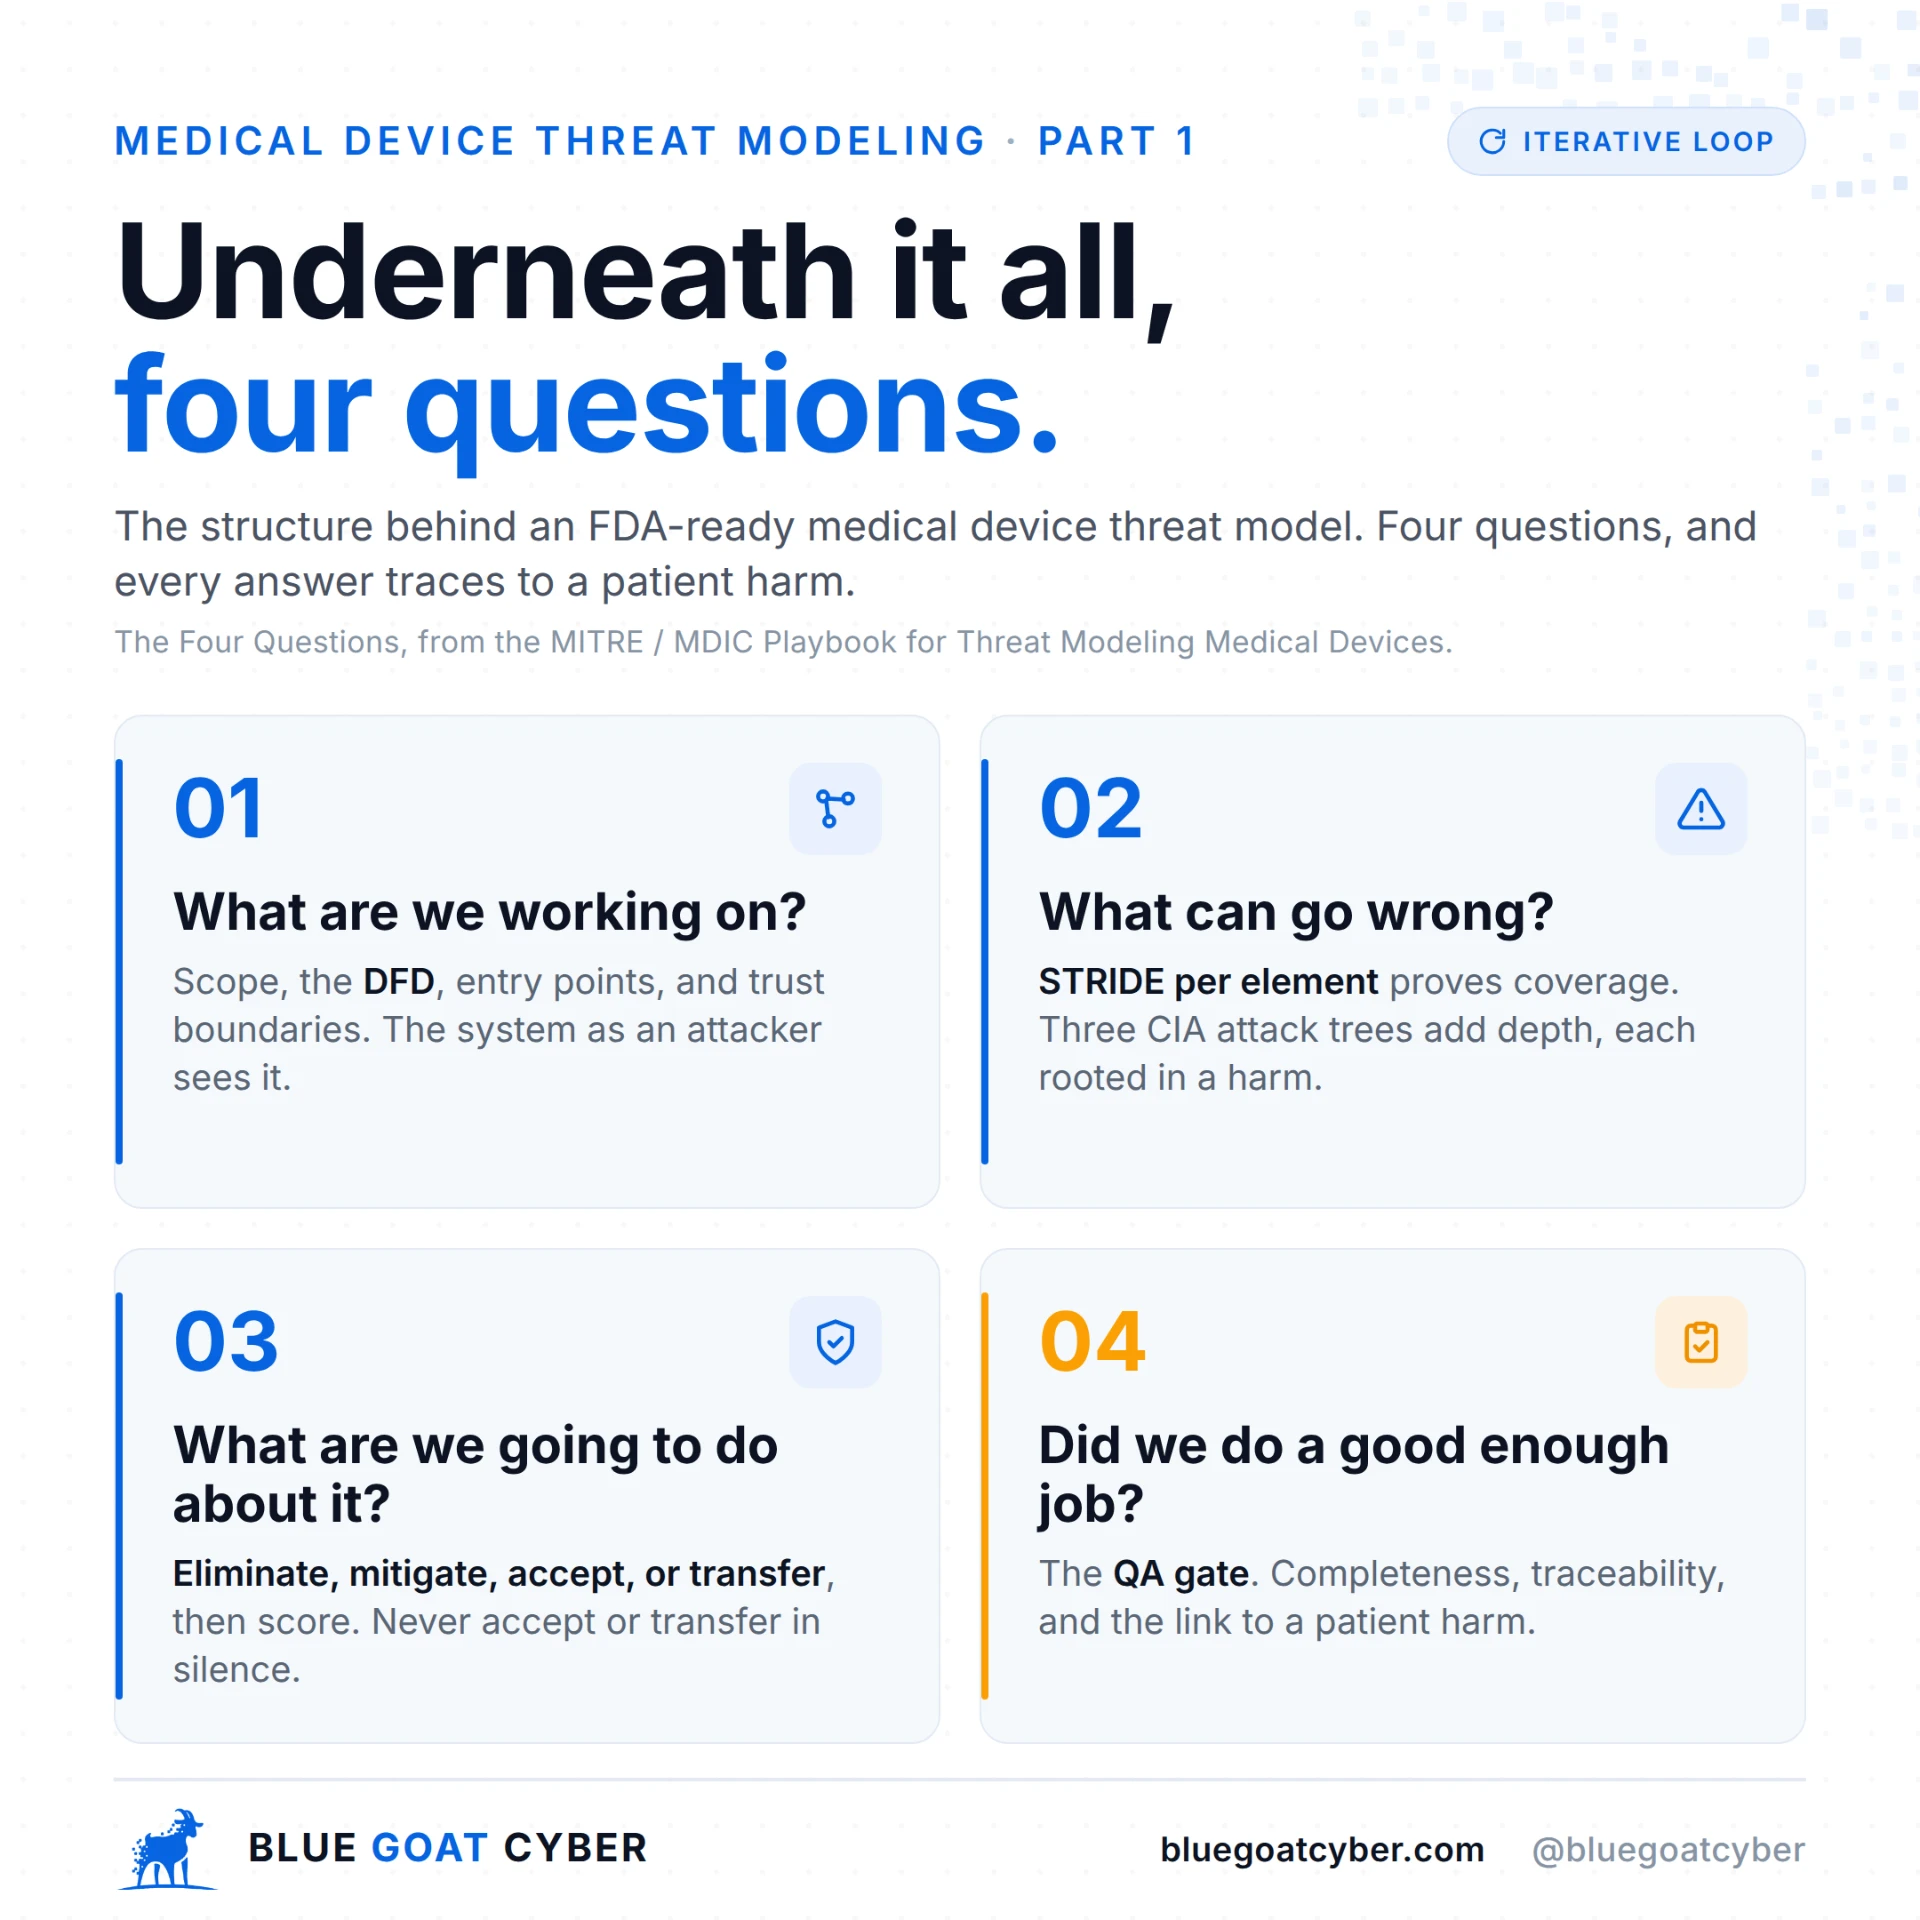
What the graphic says
The full text version, so the content is readable without the image.
The four questions
The structure behind a medical device threat model for FDA premarket submissions. Four questions, and every answer traces to a patient harm.
- 01. What are we working on?
- Scope, the data flow diagram (DFD), entry points, and trust boundaries. The system as an attacker sees it, not as the architecture deck draws it.
- 02. What can go wrong?
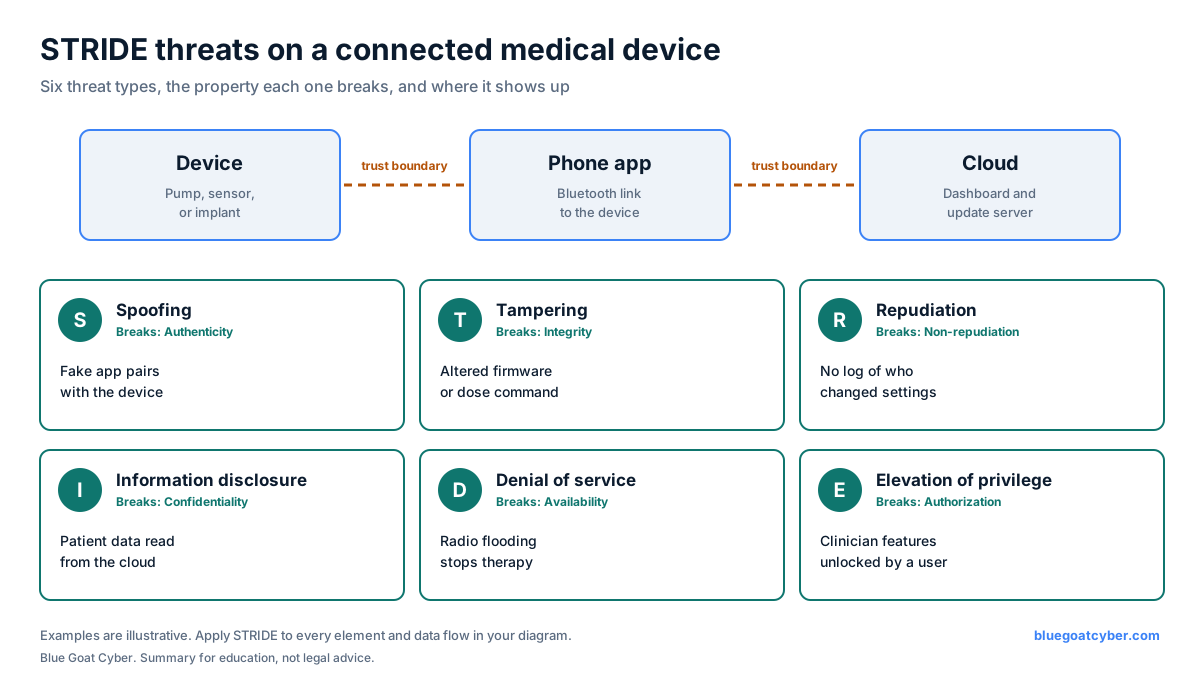
- STRIDE per element proves coverage. Three CIA attack trees add depth, each one rooted in a specific patient harm.
- 03. What are we going to do about it?
- Eliminate, mitigate, accept, or transfer - then score. Never accept or transfer in silence; the rationale is part of the record.
- 04. Did we do a good enough job?
- The QA gate. Completeness, traceability, and the link from every threat to a patient harm.
The Four Questions, from the MITRE / MDIC Playbook for Threat Modeling Medical Devices.
Ready when you are
Secure your device before it reaches patients.
30-minute strategy session. No cost, no commitment - just answers from people who've supported 275+ FDA submissions, with zero cybersecurity rejections.