
Working with Blue Goat
How a medical device penetration test runs
The eight steps of a Blue Goat medical device penetration test, from kickoff to unlimited retests.
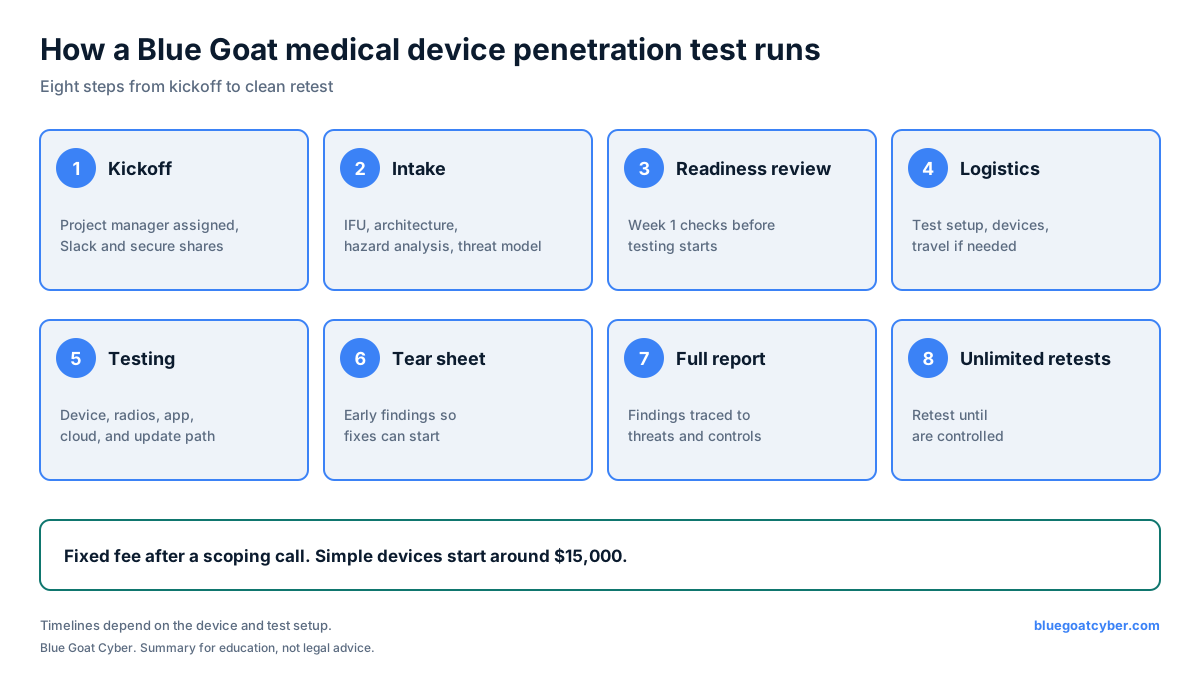
What the graphic says
The full text version, so the content is readable without the image.
Eight steps
- 1. Kickoff
- A project manager is assigned and we set up Slack and secure file shares.
- 2. Intake
- IFU, architecture, hazard analysis, and threat model. We can build the threat model if you do not have one.
- 3. Readiness review
- Week 1 checks before testing starts.
- 4. Logistics
- Test setup, devices, and travel if needed.
- 5. Testing
- Device, radios, app, cloud, and update path.
- 6. Tear sheet
- Early findings so fixes can start.
- 7. Full report
- Findings traced to threats and controls.
- 8. Unlimited retests
- We retest until uncontrolled risks are closed.
Keep reading
More in Working with Blue Goat
Ready when you are
Secure your device before it reaches patients.
30-minute strategy session. No cost, no commitment - just answers from people who've supported 275+ FDA submissions, with zero cybersecurity rejections.