Blue Goat CyberBlue Goat CyberSMMedical Device Cybersecurity
    Start here
    Services
    • Medical Device Cybersecurity Consulting
    • FDA Premarket Cybersecurity Package
    • Medical Device Penetration Testing Services
    • FDA Deficiency Response
    • FDA Postmarket Cybersecurity
    • Medical Device Threat Modeling
    • eSTAR Cybersecurity Documentation Support
    See all services
    Products

    Blue Goat products

    • GoatWatch logoGoatWatchSBOM risk management for medical devices
    About
    Resources

    Learn

    • Blog
    • Podcast
    • Webinars
    • Talks & workshops
    • Glossary
    • FAQs

    Playbooks & Tools

    • Guides
    • Playbooks (PDF)
    • Infographics
    • Interactive Tools

    Signals & Proof

    • Goat FeedNew
    • News
    • Medical Device Security News
    • The Goat's Weekly
    • Case Studies
    • Proof / Receipts
    All resources, topic hubs, & collections →
    ⌘K
    Book Strategy SessionHow to prepare →
    Blue Goat Cyber

    Full-service medical device cybersecurity. We protect patients by securing connected medical devices from design through postmarket.

    275+ FDA submissions supported, zero cybersecurity rejections · Mission: 1,000 by 2028

    SDVOSB · Service-Disabled Veteran-Owned Small Business

    We sponsor 10 community projects →

    Services

    • FDA Premarket Cybersecurity Package
    • FDA Deficiency Response
    • Medical Device Threat Modeling
    • Medical Device Penetration Testing Services
    • FDA Postmarket Cybersecurity
    • All services →
    Services
    • FDA Premarket Cybersecurity Package
    • FDA Deficiency Response
    • Medical Device Threat Modeling
    • Medical Device Penetration Testing Services
    • FDA Postmarket Cybersecurity
    • All services →

    Company

    • About
    • Core values
    • Manifesto
    • Leadership
    • Why Us
    • Partners
    • Careers
    • Press
    • Press kit
    • Contact
    • Company overviewPDF
    Company
    • About
    • Core values
    • Manifesto
    • Leadership
    • Why Us
    • Partners
    • Careers
    • Press
    • Press kit
    • Contact
    • Company overviewPDF

    Resources

    • Blog
    • Guides
    • Podcast
    • Case studies
    • Monthly Pulse newsletter
    • All resources →
    Resources
    • Blog
    • Guides
    • Podcast
    • Case studies
    • Monthly Pulse newsletter
    • All resources →

    Get in touch

    • info@bluegoatcyber.com
    • 844-939-GOAT
    • Book a strategy session →
    • 1776 N Scottsdale Rd, Unit 727
      Scottsdale, AZ 85257Serving clients worldwide

    Follow

    © 2026 Blue Goat Cyber. All rights reserved.

    • Privacy
    • Terms
    • Cookies
    • Sitemap
    • Accessibility
    • CVD

    MedTech Cybersecurity · Since 2022

    All infographics
    Threat Modeling

    CVSS 4.0 at a glance, with a medical device example

    The four CVSS 4.0 metric groups and a worked infusion pump example that scores 8.7 High.
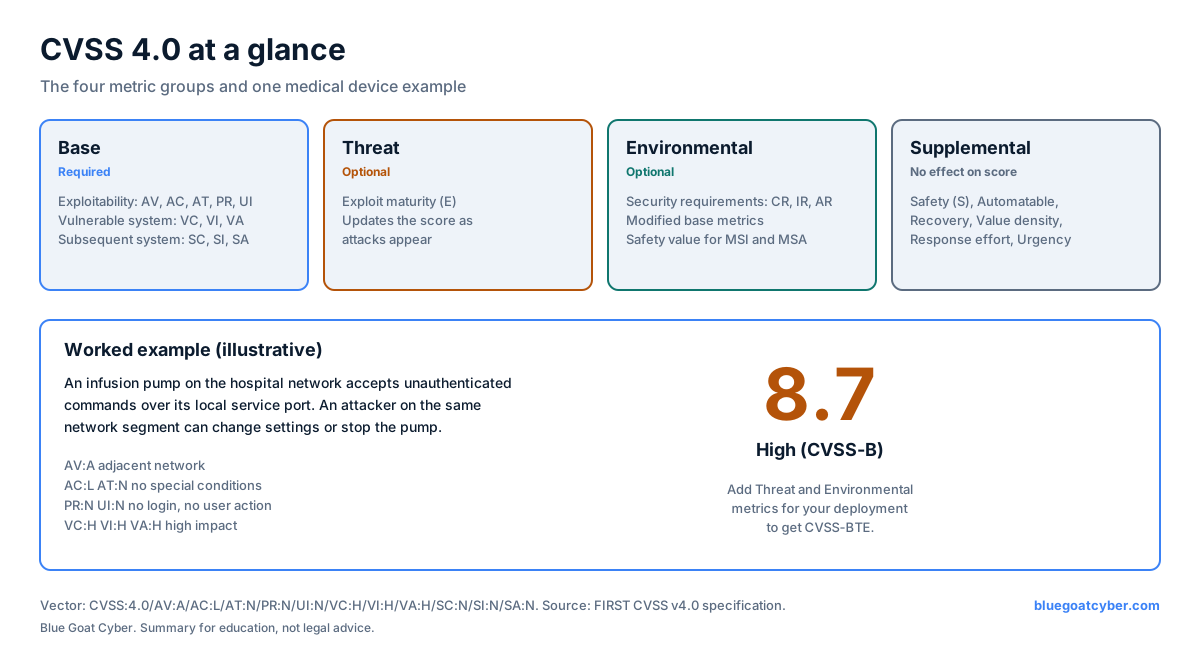
    Infographic of CVSS 4.0 Base, Threat, Environmental, and Supplemental metric groups, plus an illustrative infusion pump vulnerability with vector AV:A/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N scoring 8.7 High.
    The base score is a starting point. Add Threat and Environmental metrics for how your device is actually deployed.
    Download the graphicTalk through it with us

    What the graphic says

    The full text version, so the content is readable without the image.

    The four metric groups

    Base (required)
    Exploitability (AV, AC, AT, PR, UI), vulnerable system impact (VC, VI, VA), and subsequent system impact (SC, SI, SA).
    Threat (optional)
    Exploit maturity (E), which updates the score as attacks appear.
    Environmental (optional)
    Security requirements (CR, IR, AR), modified base metrics, and a Safety value for subsequent integrity and availability.
    Supplemental (no effect on score)
    Safety, Automatable, Recovery, Value density, Response effort, and Provider urgency.

    Worked example (illustrative)

    An infusion pump on the hospital network accepts unauthenticated commands over its local service port. An attacker on the same network segment can change settings or stop the pump.

    Vector
    CVSS:4.0/AV:A/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N
    Score
    8.7, High (CVSS-B, base metrics only).

    Source: FIRST CVSS v4.0 specification. Score computed with the same engine as our calculator.

    Keep reading

    • Free CVSS v4.0 calculator
    • CVSS score for medical devices
    • CVSS 3.1 vs 4.0 for medical devices

    More in Threat Modeling

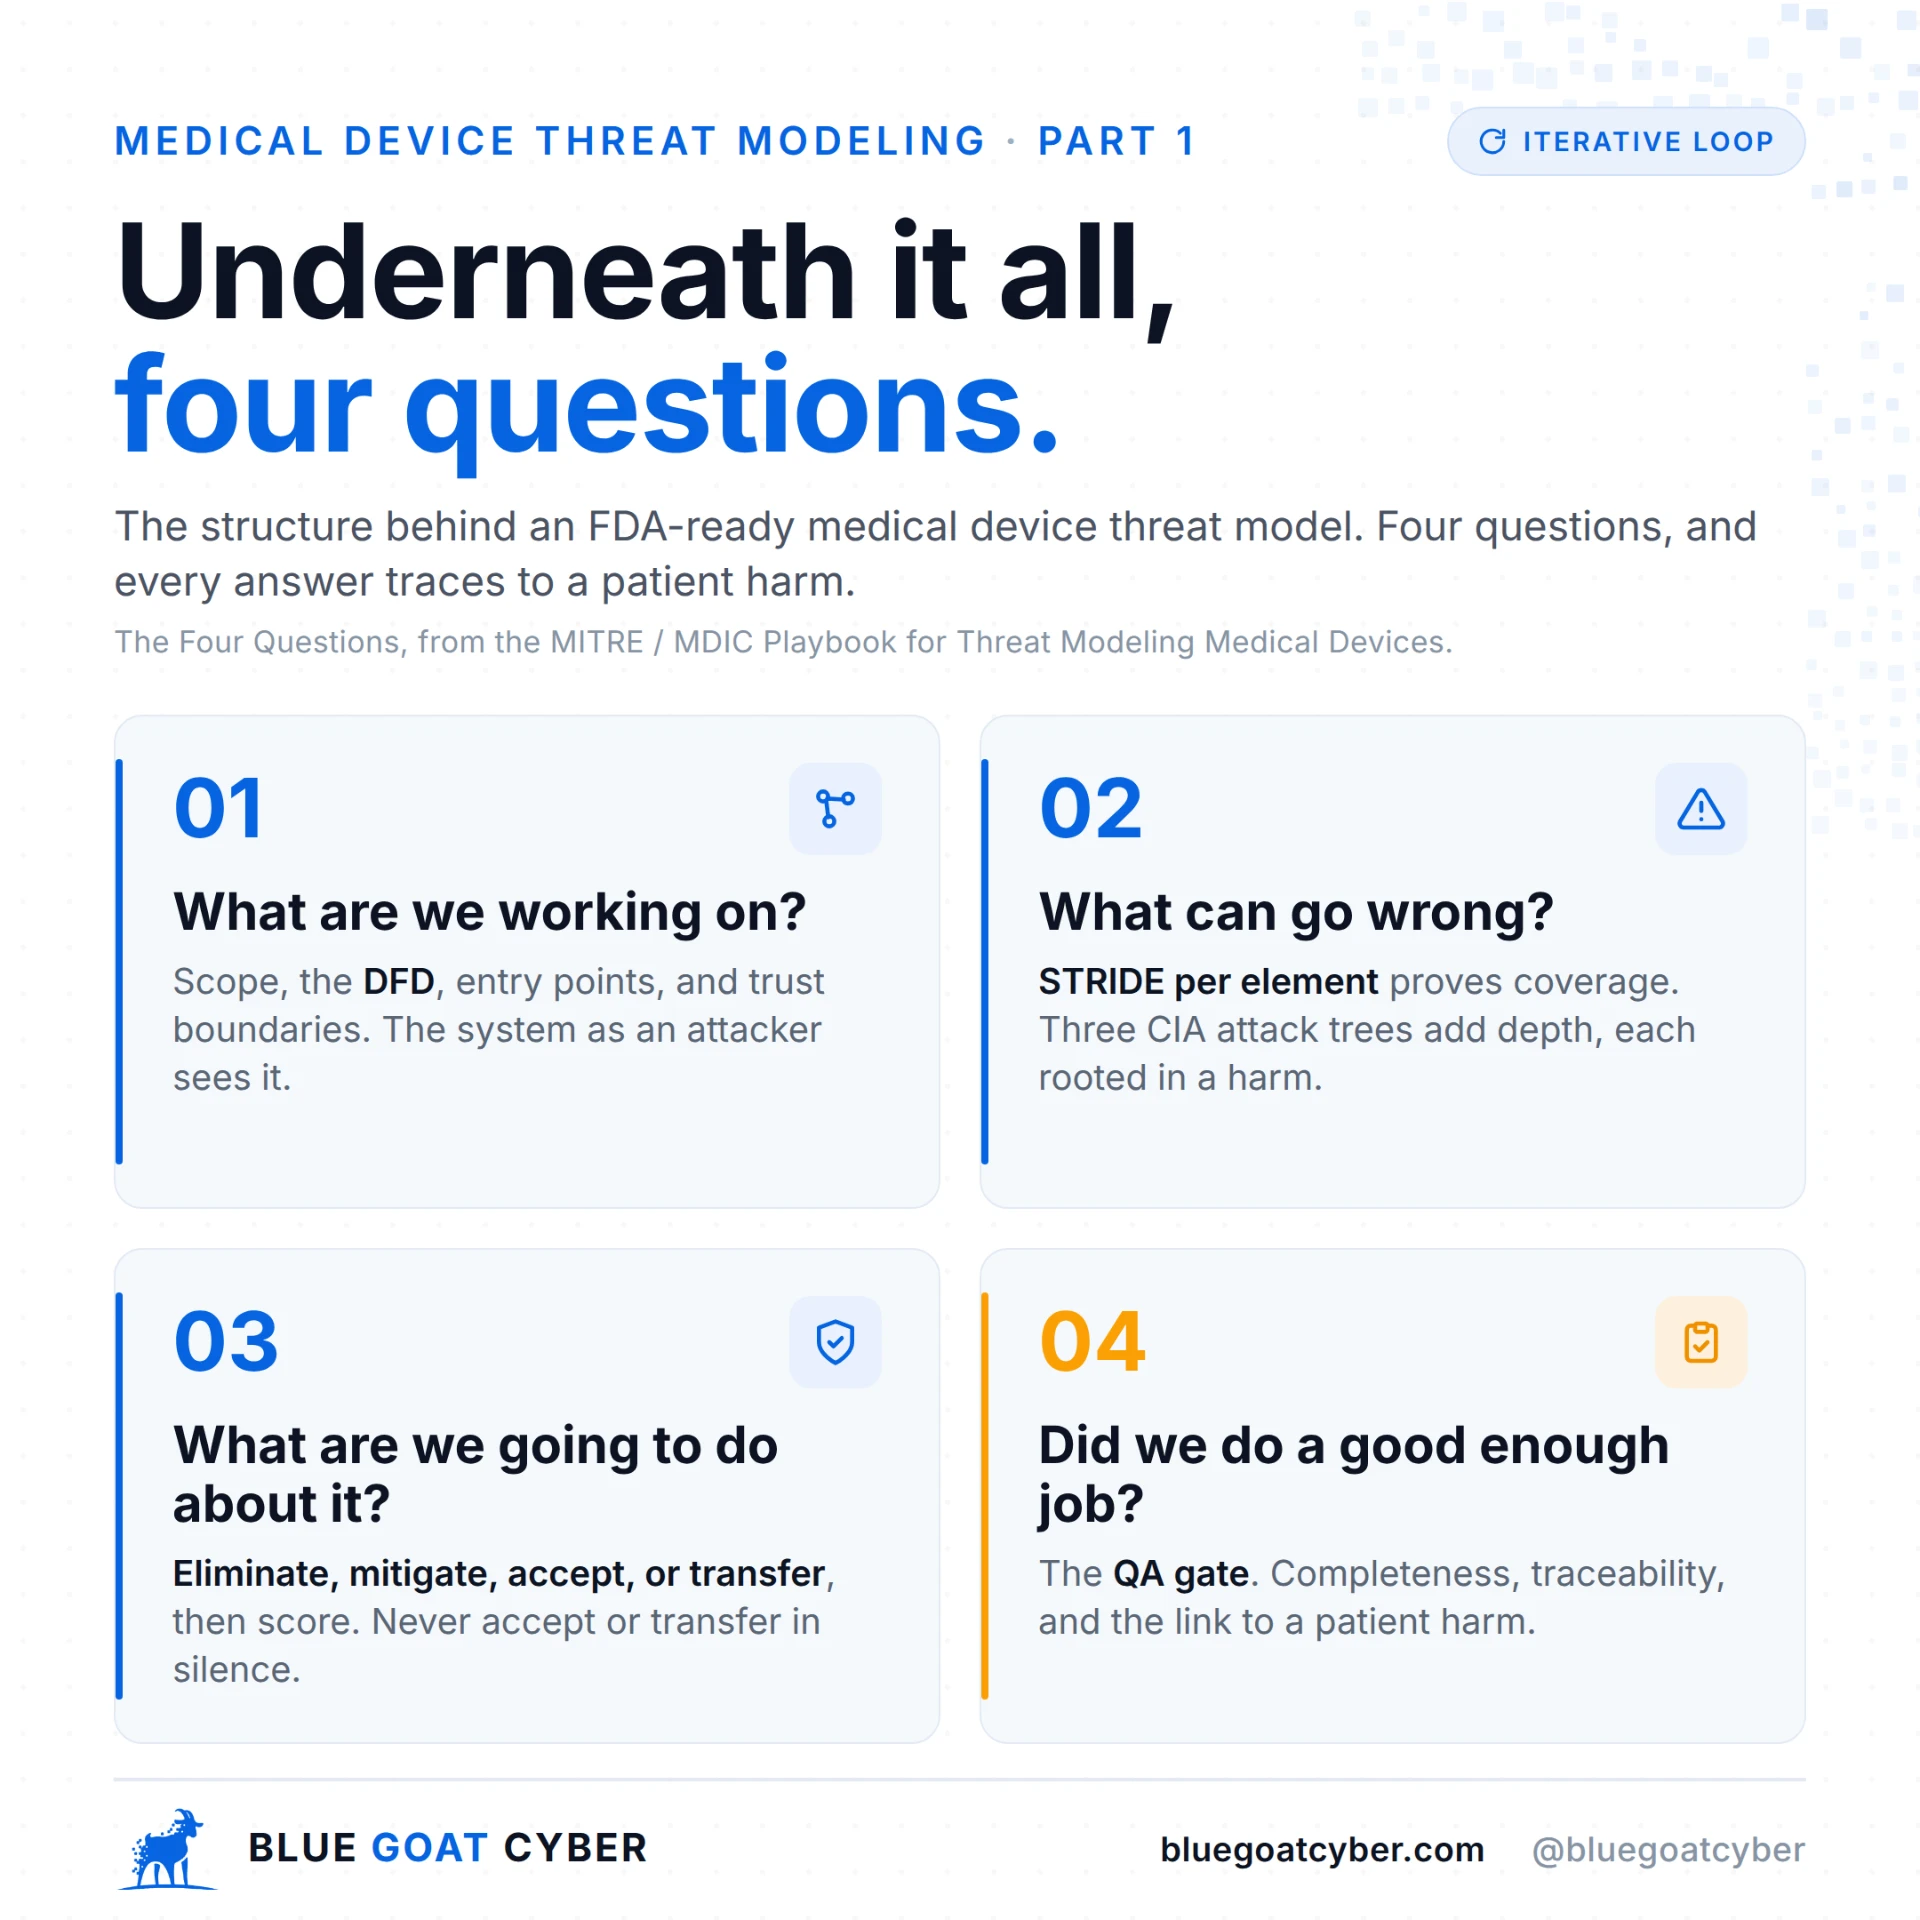
    Infographic: the four threat modeling questions - what are we working on, what can go wrong, what are we going to do about it, and did we do a good enough job - each with the artifacts it produces.
    Part 1

    Underneath it all, four questions

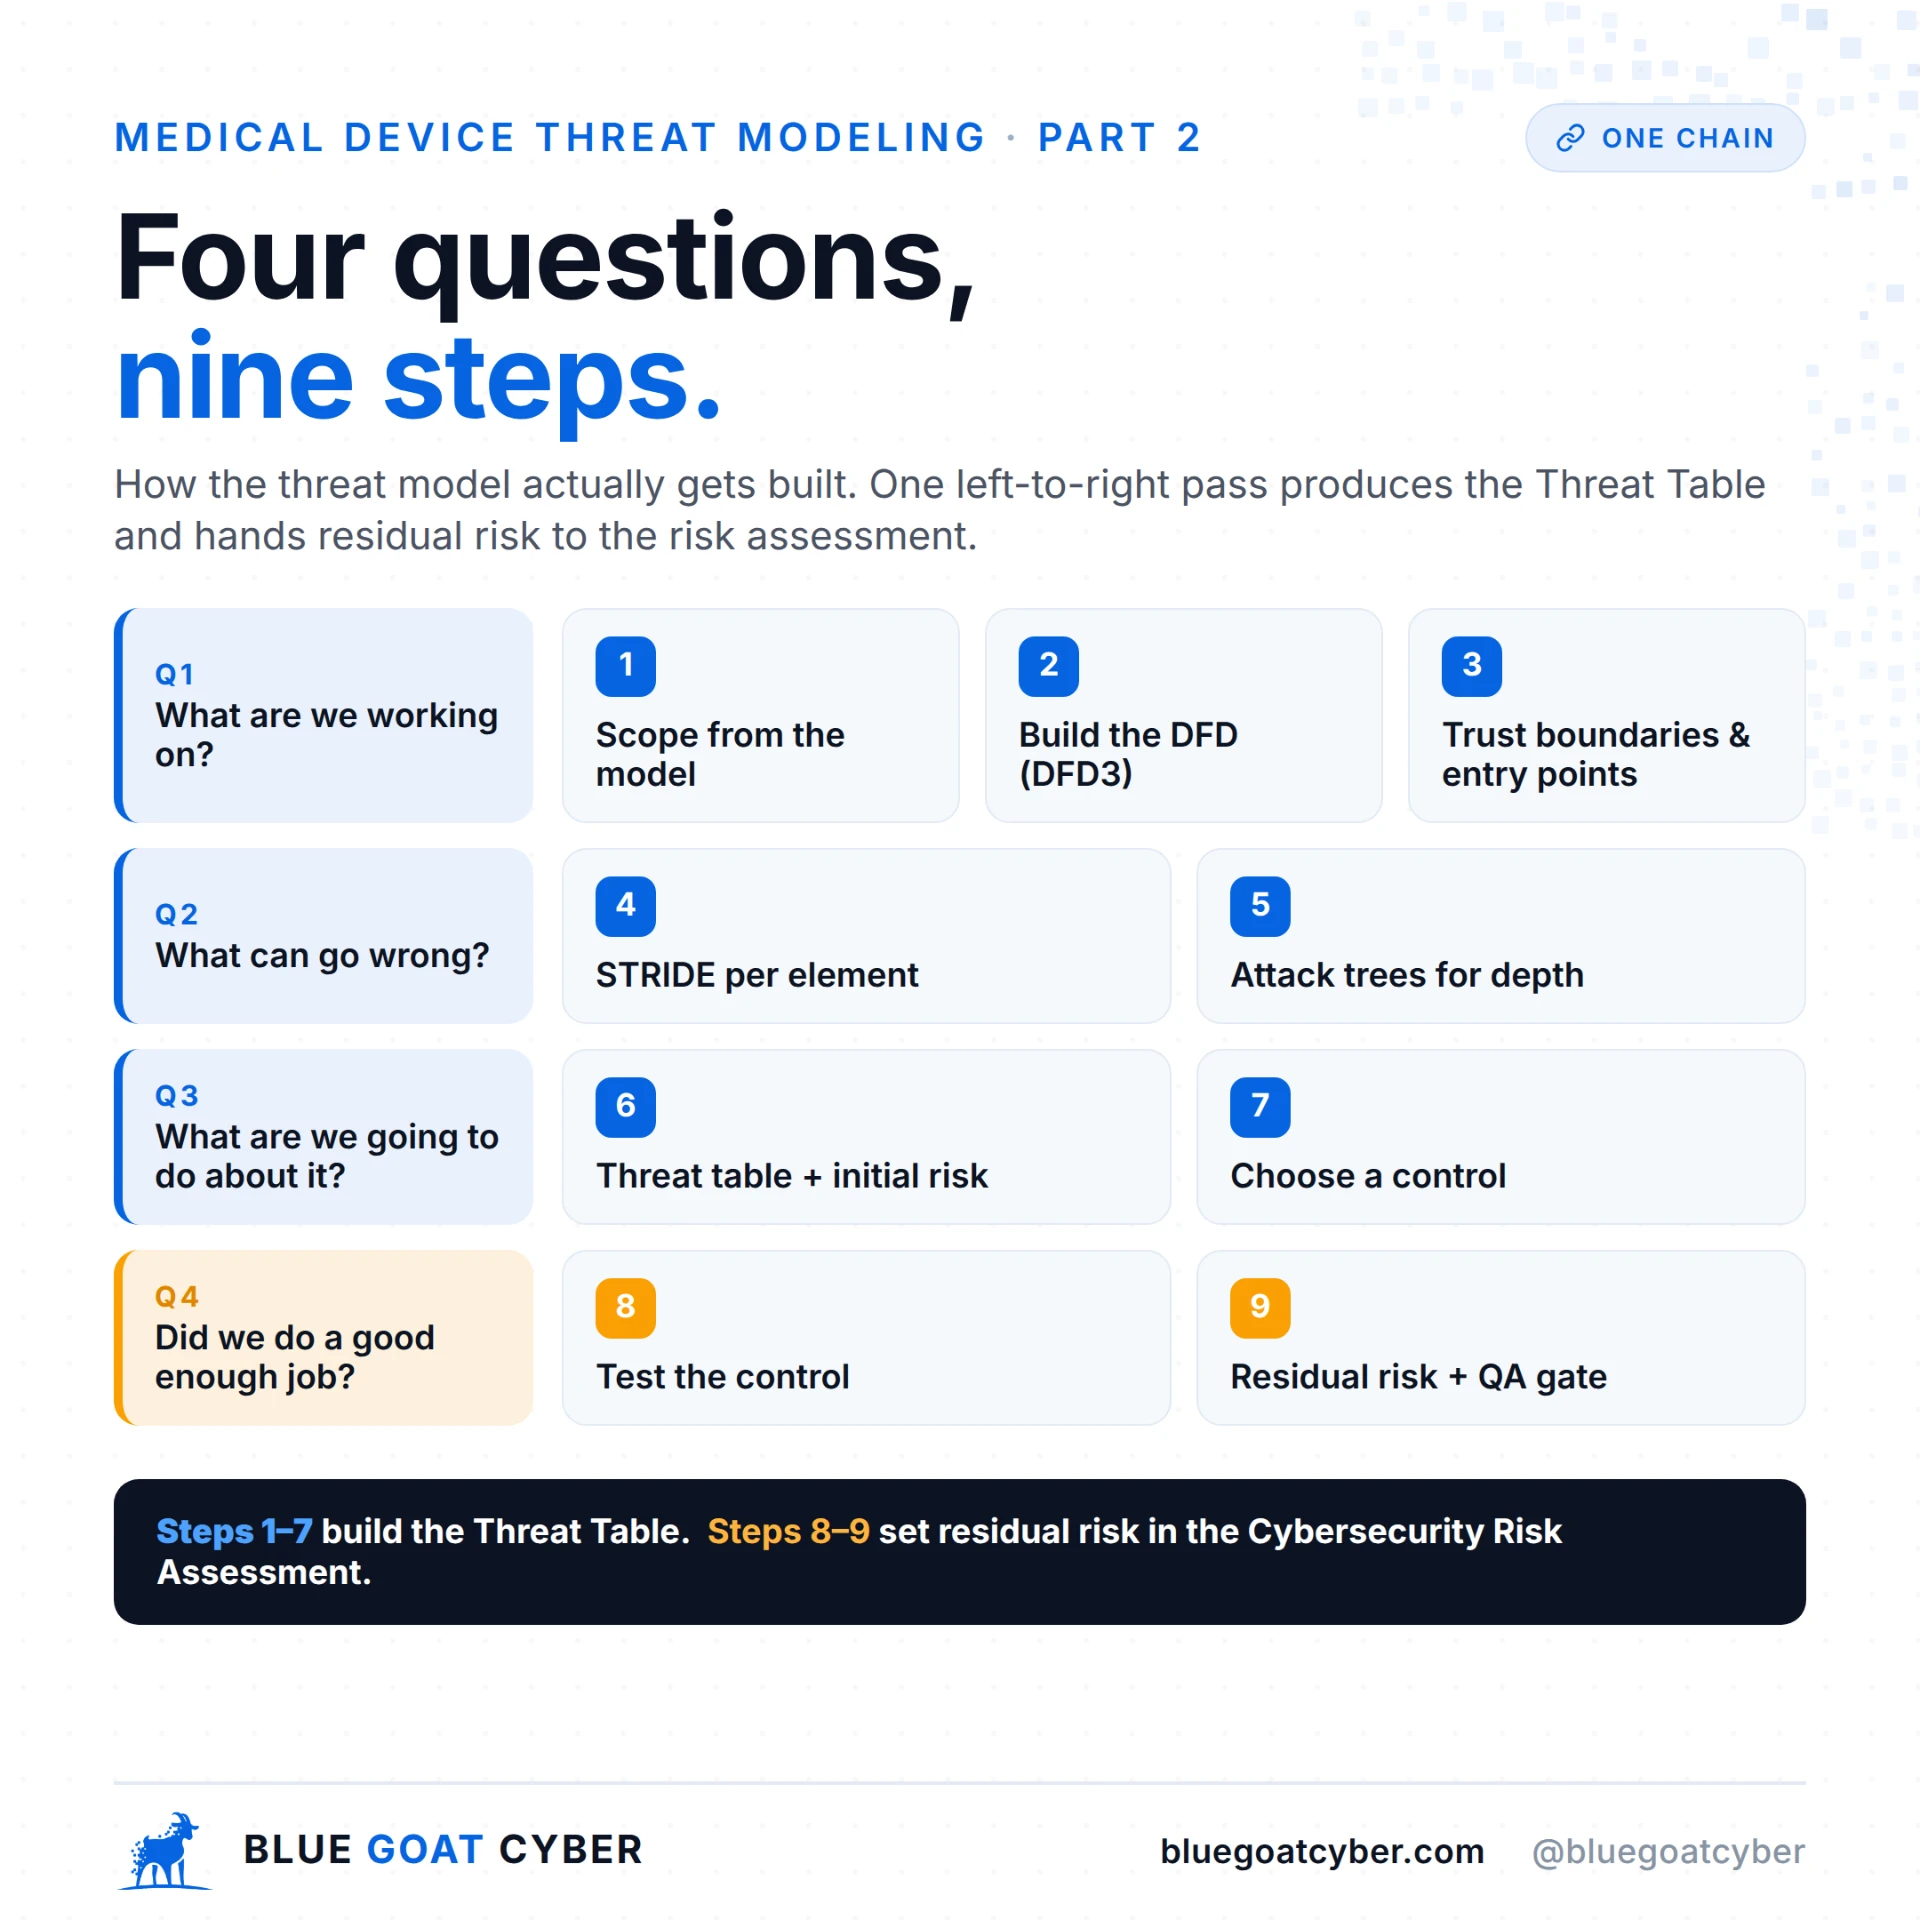
    Infographic: the nine-step medical device threat modeling workflow mapped to the four questions, from scoping and the DFD through STRIDE, attack trees, controls, testing, and the residual risk QA gate.
    Part 2

    Four questions, nine steps

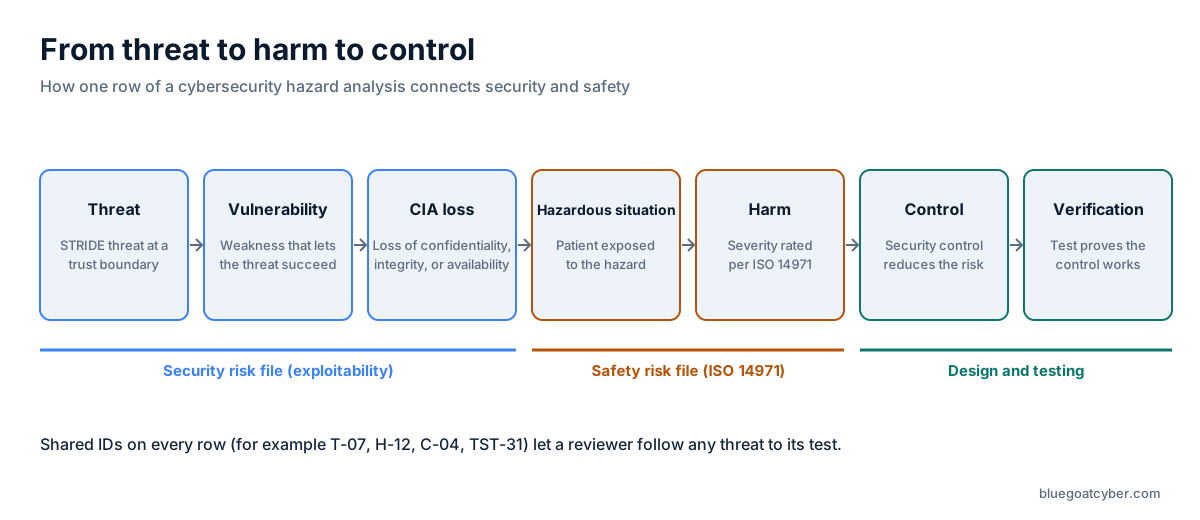
    Infographic chain of seven steps: threat, vulnerability, CIA loss, hazardous situation, harm rated per ISO 14971, security control, and verification, with shared IDs on every row.
    Part 3

    Cybersecurity hazard analysis: from threat to harm to control

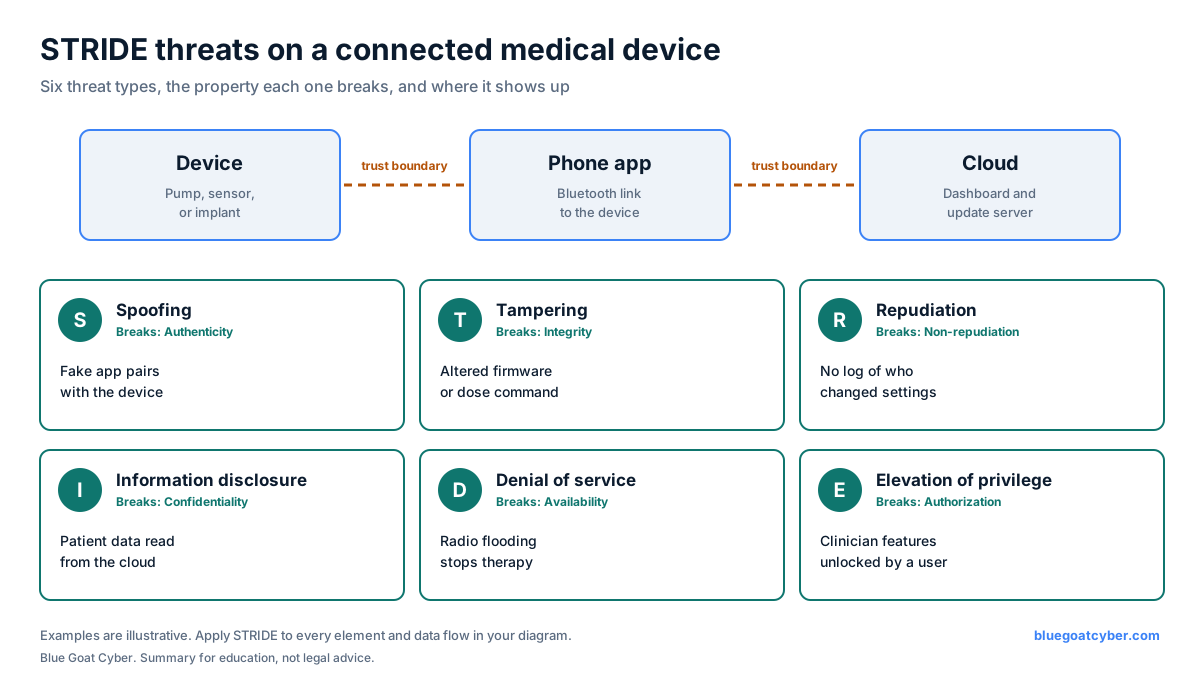
    Infographic of a device, phone app, and cloud separated by trust boundaries, with six STRIDE cards: spoofing, tampering, repudiation, information disclosure, denial of service, and elevation of privilege, each with the property it breaks and a device example.

    STRIDE threats on a connected medical device

    Ready when you are

    Secure your device before it reaches patients.

    30-minute strategy session. No cost, no commitment - just answers from people who've supported 275+ FDA submissions, with zero cybersecurity rejections.
    Book strategy sessionExplore services