
FDA Regulation
What goes in the eSTAR cybersecurity section
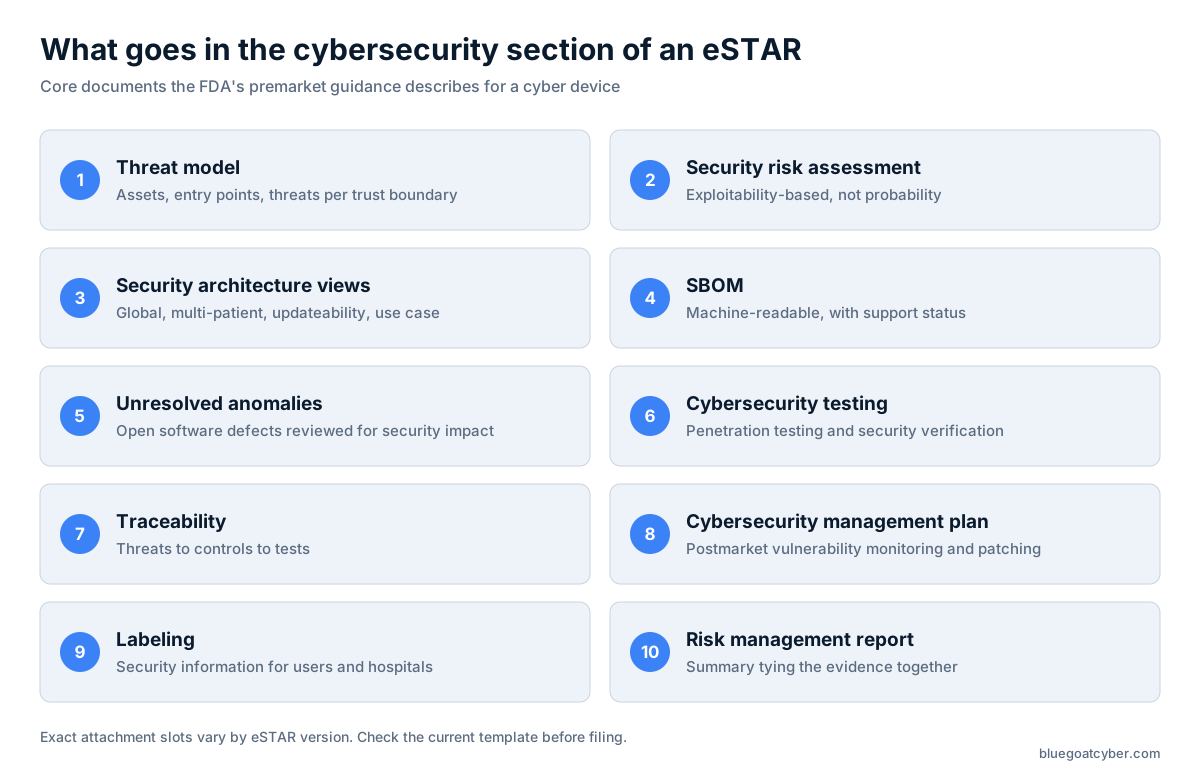
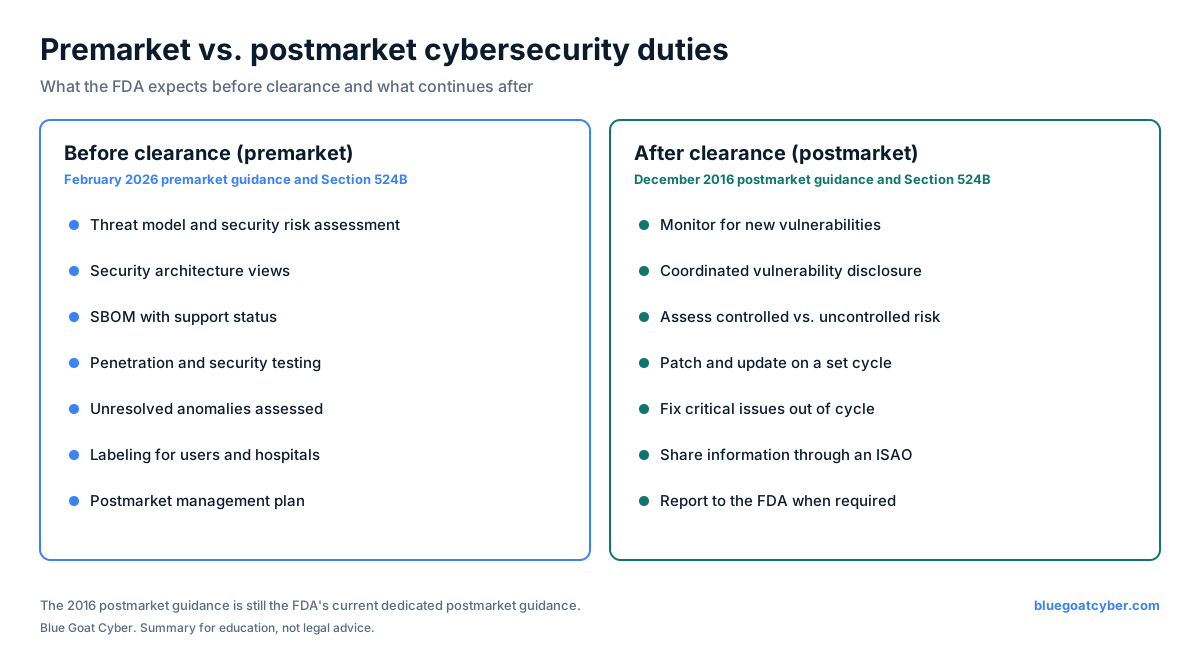
The ten core documents the FDA's premarket guidance describes for a cyber device, and what each one has to show in an eSTAR submission.
What the graphic says
The full text version, so the content is readable without the image.
Ten core documents
Core documents the FDA's premarket guidance describes for a cyber device.
- 1. Threat model
- Assets, entry points, and threats per trust boundary.
- 2. Security risk assessment
- Exploitability-based, not probability-based.
- 3. Security architecture views
- Global system, multi-patient harm, updateability, and security use case views.
- 4. SBOM
- Machine-readable, with support status for each component.
- 5. Unresolved anomalies
- Open software defects reviewed for security impact.
- 6. Cybersecurity testing
- Penetration testing and security verification.
- 7. Traceability
- Threats to controls to tests.
- 8. Cybersecurity management plan
- Postmarket vulnerability monitoring and patching.
- 9. Labeling
- Security information for users and hospitals.
- 10. Risk management report
- Summary tying the evidence together.
Keep reading
Ready when you are
Secure your device before it reaches patients.
30-minute strategy session. No cost, no commitment - just answers from people who've supported 275+ FDA submissions, with zero cybersecurity rejections.