
FDA Regulation
Section 524B checklist for cyber devices
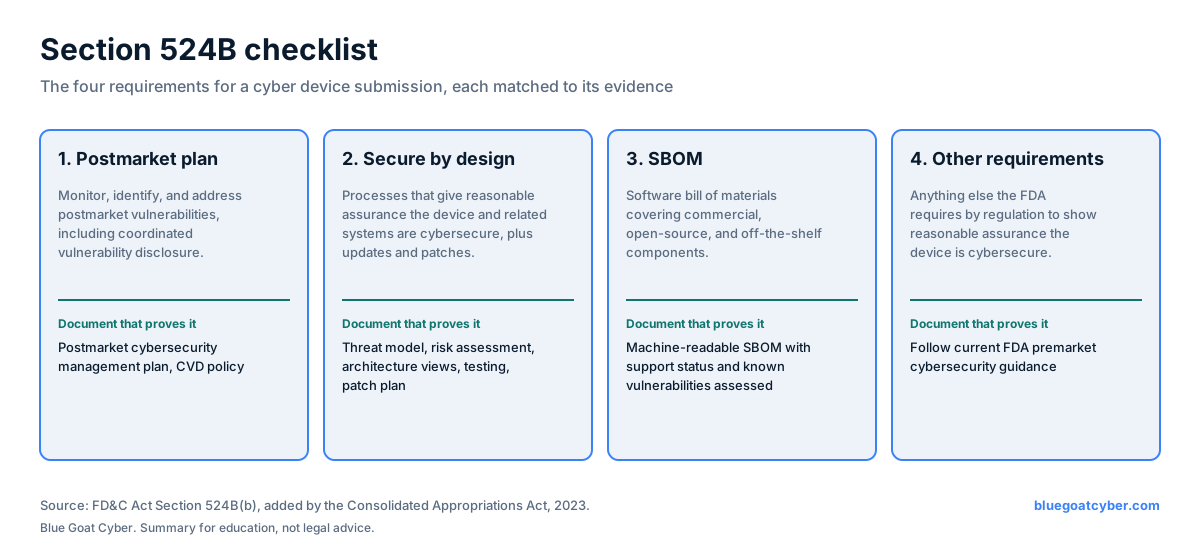
The four Section 524B requirements for a cyber device submission on one card, each matched to the document that proves it.
What the graphic says
The full text version, so the content is readable without the image.
The four requirements and their evidence
From FD&C Act Section 524B(b).
- 1. Postmarket plan
- Monitor, identify, and address postmarket vulnerabilities, including coordinated vulnerability disclosure. Evidence: postmarket cybersecurity management plan and CVD policy.
- 2. Secure by design
- Processes that give reasonable assurance the device and related systems are cybersecure, plus updates and patches. Evidence: threat model, risk assessment, architecture views, testing, and patch plan.
- 3. SBOM
- A software bill of materials covering commercial, open-source, and off-the-shelf components. Evidence: machine-readable SBOM with support status and known vulnerabilities assessed.
- 4. Other requirements
- Anything else the FDA requires by regulation to show reasonable assurance the device is cybersecure. Evidence: follow current FDA premarket cybersecurity guidance.
Source: FD&C Act Section 524B, added by the Consolidated Appropriations Act, 2023. Summary for education, not legal advice.
Keep reading
Ready when you are
Get FDA cleared without the cybersecurity headaches.
30-minute strategy session. No cost, no commitment - just answers from people who've shipped 275+ devices supported.