
FDA Regulation
Premarket vs. postmarket cybersecurity duties
What the FDA expects before clearance and what continues after, side by side.
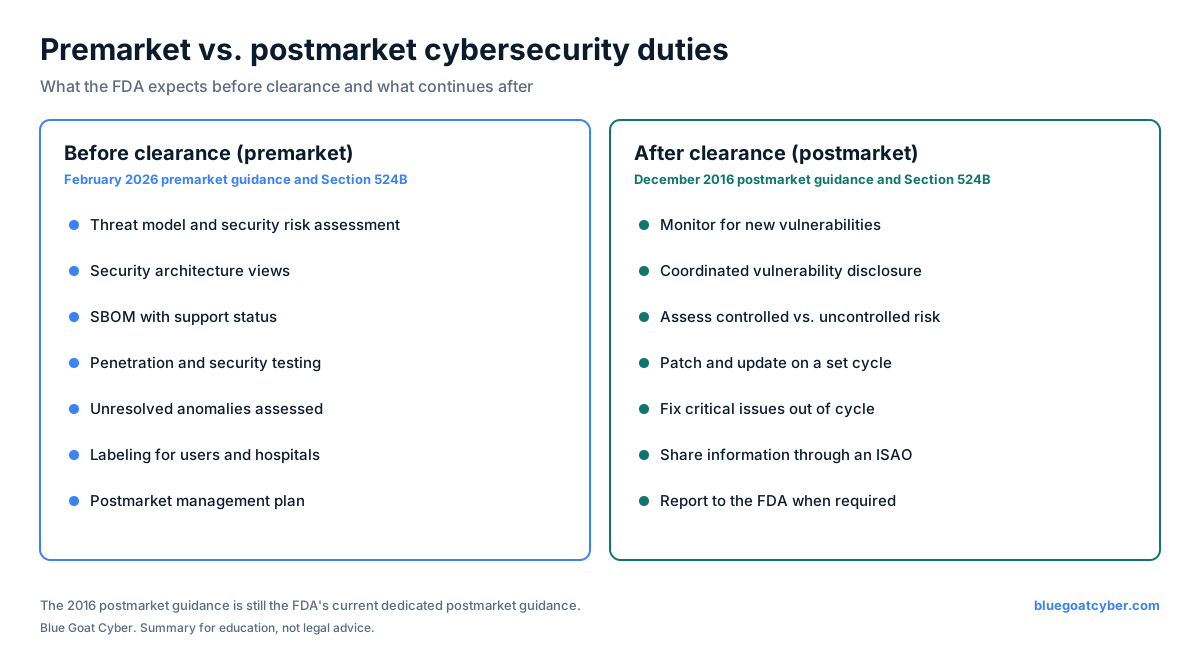
What the graphic says
The full text version, so the content is readable without the image.
Before clearance (premarket)
February 2026 premarket guidance and Section 524B.
- Threat model and risk assessment
- Security risk assessment tied to the threat model.
- Architecture views
- Security architecture views of the system.
- SBOM
- With support status for each component.
- Testing
- Penetration and security testing.
- Unresolved anomalies
- Assessed for security impact.
- Labeling
- Security information for users and hospitals.
- Postmarket plan
- How the device will be kept secure after clearance.
After clearance (postmarket)
December 2016 postmarket guidance and Section 524B.
- Monitoring
- Watch for new vulnerabilities.
- Coordinated disclosure
- Accept and act on outside vulnerability reports.
- Risk assessment
- Decide whether risk is controlled or uncontrolled.
- Patching
- Updates on a set cycle, critical fixes out of cycle.
- Information sharing
- Share through an ISAO.
- Reporting
- Report to the FDA when required.
Keep reading
Ready when you are
Secure your device before it reaches patients.
30-minute strategy session. No cost, no commitment - just answers from people who've supported 275+ FDA submissions, with zero cybersecurity rejections.