CVSS Scoring for Medical Devices: A Complete Walkthrough
How CVSS scoring works for medical devices, a worked scoring example, and why a raw score is not a patient risk score under FDA guidance.
Read articleEvery article in our archive tagged Primer.
Looking for a quick answer instead? The FDA medical device cybersecurity FAQ covers Section 524B scope, SBOMs, threat models, CR515 and GMLP, deficiencies, and postmarket duties.
Showing 12 of 104 articles tagged Primer · Page 1 of 9
How CVSS scoring works for medical devices, a worked scoring example, and why a raw score is not a patient risk score under FDA guidance.
Read article
How to evaluate healthcare cybersecurity companies by category, the questions to ask, and the evidence an FDA submission actually requires from a vendor.
Read article
Medical device software development explained: design controls, IEC 62304 safety classes, SOUP management, verification, validation, and FDA documentation.
Read article
Security requirements testing verifies your design inputs; penetration testing attacks the built device. What the FDA's Feb 2026 guidance expects for each.
Read article
You're two years into product development and still "not ready" for cybersecurity? You're already late.
Read article
A phase-by-phase mapping of the FDA's SPDF onto IEC 81001-5-1 activities, so dual FDA + EU submissions produce one artifact set instead of two.
Read article
IEC 62304 governs the software lifecycle. IEC 81001-5-1 adds security activities on top.
Read article
The FDA lists JSP2, SPDF, IEC 81001-5-1, and ISA/IEC 62443-4-1 as acceptable cybersecurity frameworks. Here's how to actually pick one for your submission.
Read article
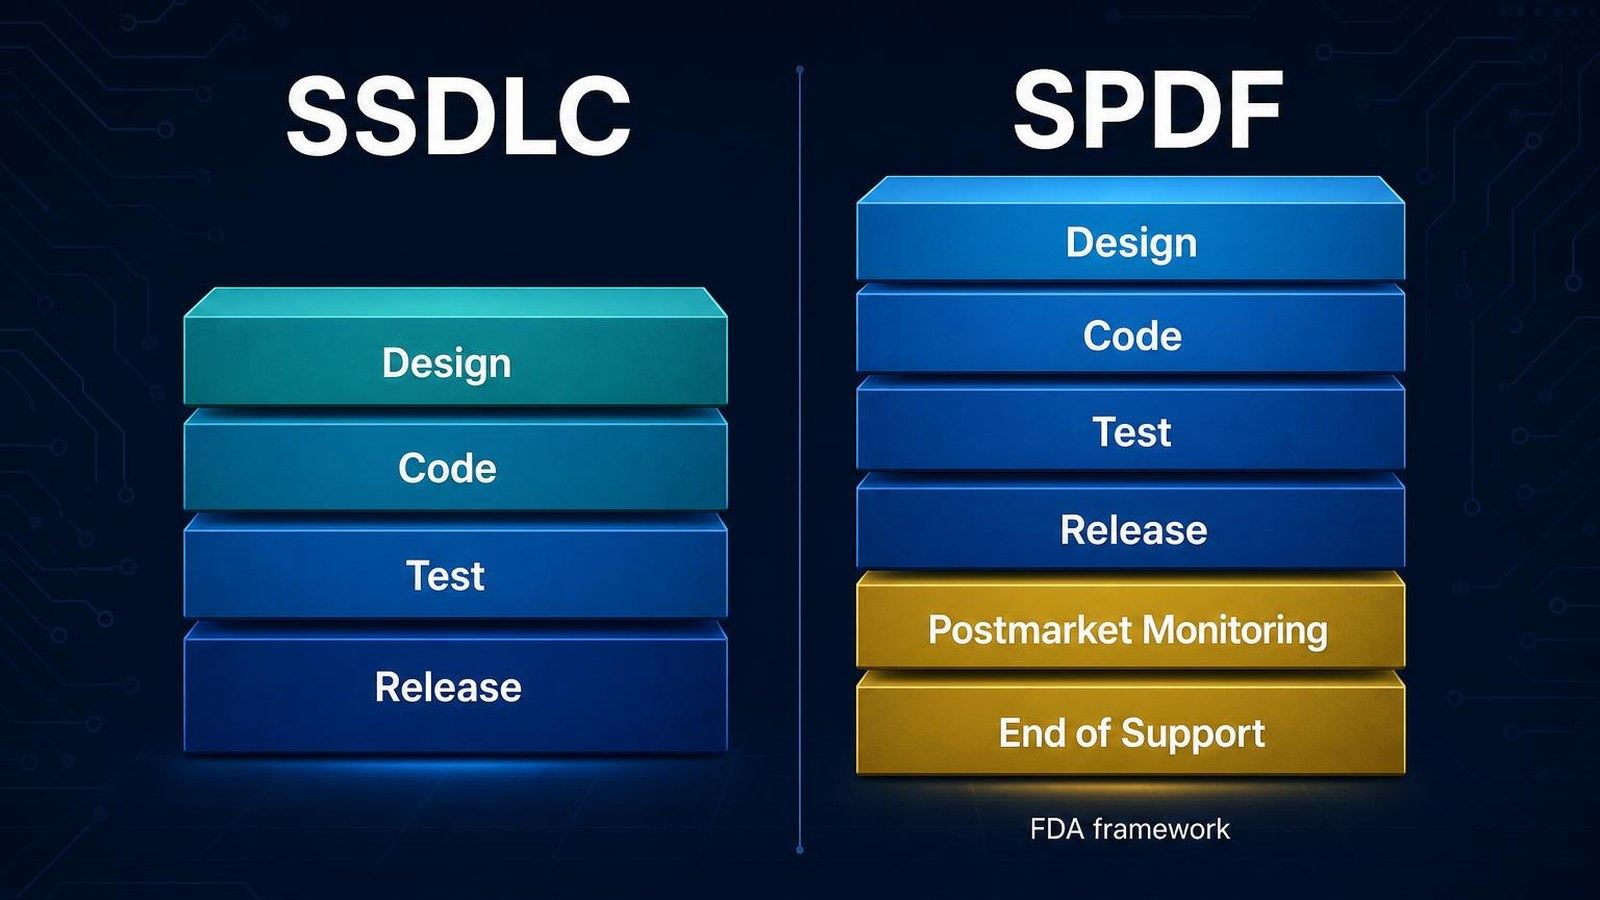
SPDF vs SSDLC for medical devices. Why the FDA's Secure Product Development Framework demands more than a standard Secure SDLC, and what to add.
Read article
What the FDA's Feb 2026 guidance recommends for IDE cybersecurity: informed consent, architecture views, SBOM, labeling, and what's not required yet.
Read article
MQTT is one of the most common protocols in IoMT and one of the most commonly misconfigured.
Read article
How to build FDA-defensible fuzz harnesses for the protocols medical devices actually speak.
Read article30-minute strategy session. No cost, no commitment - just answers from people who've shipped 275+ FDA submissions.