Docker Containers in Medical Devices: FDA Testing
Where containers appear in medical devices, the testing the FDA expects under the Feb 3, 2026 guidance, and how container evidence maps to eSTAR v7.0.
Read articleEvery article in our archive tagged Section 524B.
Looking for a quick answer instead? The FDA medical device cybersecurity FAQ covers Section 524B scope, SBOMs, threat models, CR515 and GMLP, deficiencies, and postmarket duties.
Showing 12 of 37 articles tagged Section 524B · Page 3 of 4
Where containers appear in medical devices, the testing the FDA expects under the Feb 3, 2026 guidance, and how container evidence maps to eSTAR v7.0.
Read article
When a chip vendor's SBOM is enough, when it isn't, and what changes the moment a MedTech team modifies modem, radio, or SoC firmware in the device.
Read article
Section 524B(b)(1) makes patchability statutory. What the FDA's Feb 2026 guidance expects in the patch and update mechanism test evidence, the test cases.
Read article
DAST is a subset of FDA-required penetration testing. What the Feb 2026 guidance expects in eSTAR Slot 7, and why a Burp scan alone will fail review.
Read article
How to design, isolate, and defend the update channel for connected medical devices - signed manifests, dual-bank A/B, rollback protection, HSM-backed.
Read article
Class I, II, III doesn't decide your FDA cybersecurity burden. Section 524B's cyber-device test and whether you file a premarket submission do.
Read article
What the FDA's Feb 2026 premarket cybersecurity guidance says (and doesn't say) about AI-run penetration testing, where AI helps, where it fails a 524B.
Read article
What the FDA's Feb 2026 premarket guidance actually requires for medical device penetration testing - what's inside a real pen test, what's separate.
Read article
When a cybersecurity change to a cleared device stays as a letter to file in the DHF, and when it forces a new 510(k). Decision framework and examples.
Read article
When the FDA accepts a Special 510(k) for cybersecurity changes - BLE, firmware signing, Secure Boot, SBOM swaps - and when it pushes you to Traditional.
Read article
EOS vs EOL vs Level of Support in your medical device SBOM: what Section 524B requires, how to express it in CycloneDX and SPDX, and how to defend it.
Read article
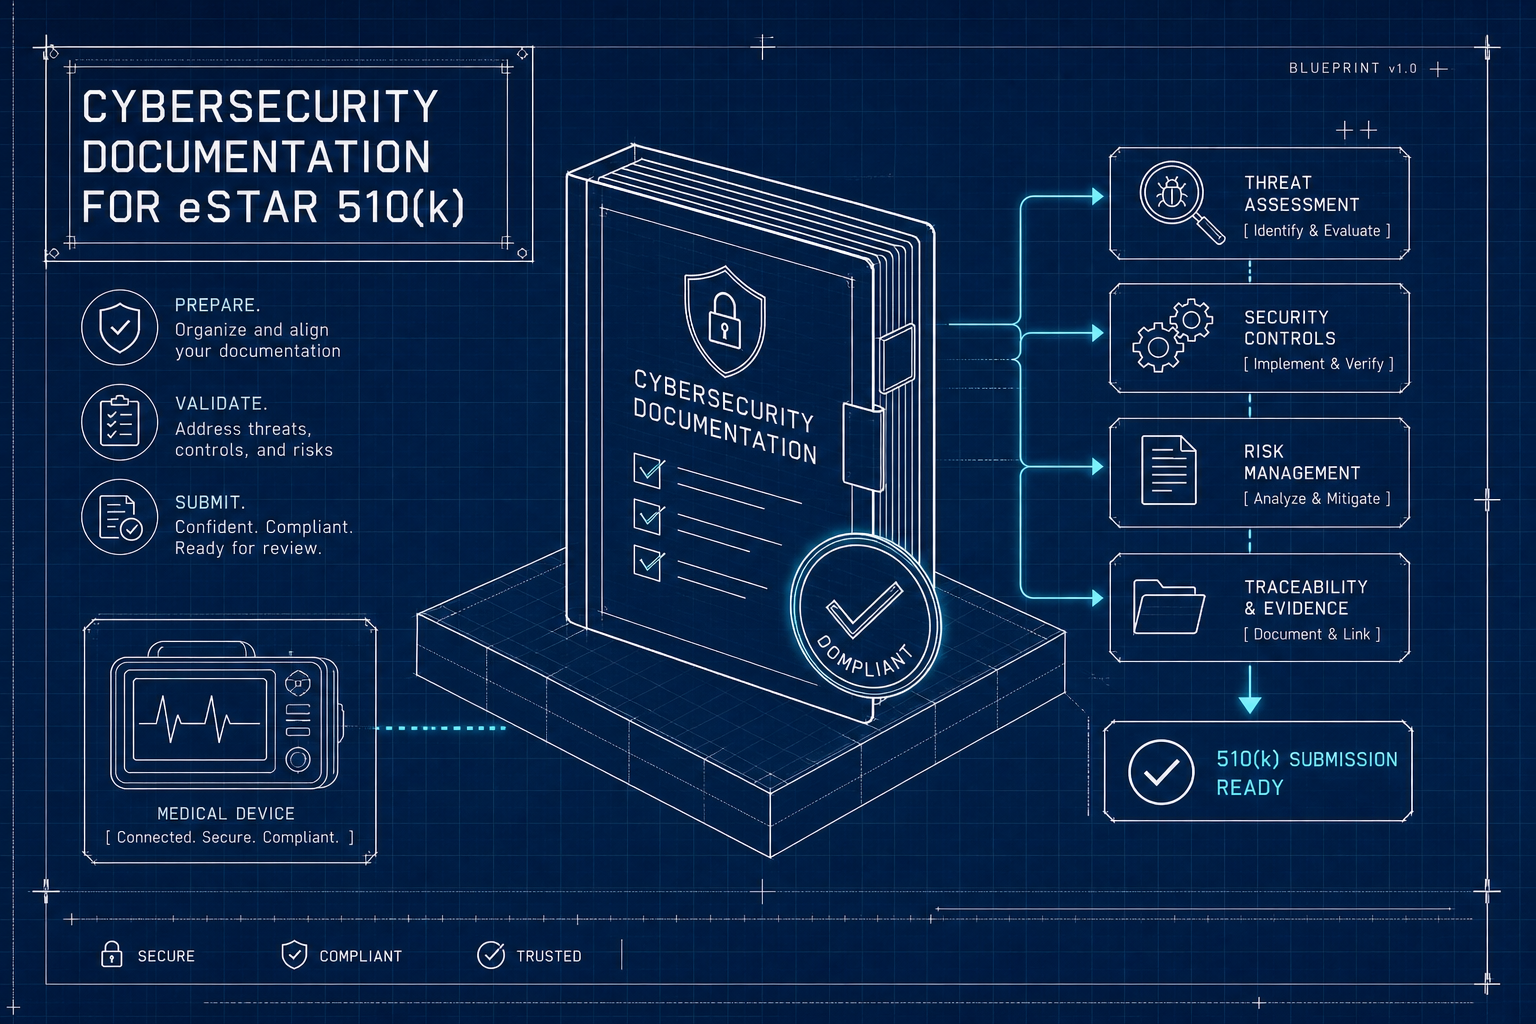
FDA cybersecurity documentation requirements (2026): SPDF artifacts, Section 524B evidence, SBOM, threat model, testing, and labeling reviewers expect.
Read article30-minute strategy session. No cost, no commitment - just answers from people who've shipped 275+ FDA submissions.